STX RAT: The .NET Backdoor Popular with Ransomware Affiliates
New malware called STX RAT was discovered as the first RAT to be able to use invisibility techniques and perform a variety of operations. This was first se...
Found 40 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
New malware called STX RAT was discovered as the first RAT to be able to use invisibility techniques and perform a variety of operations. This was first se...
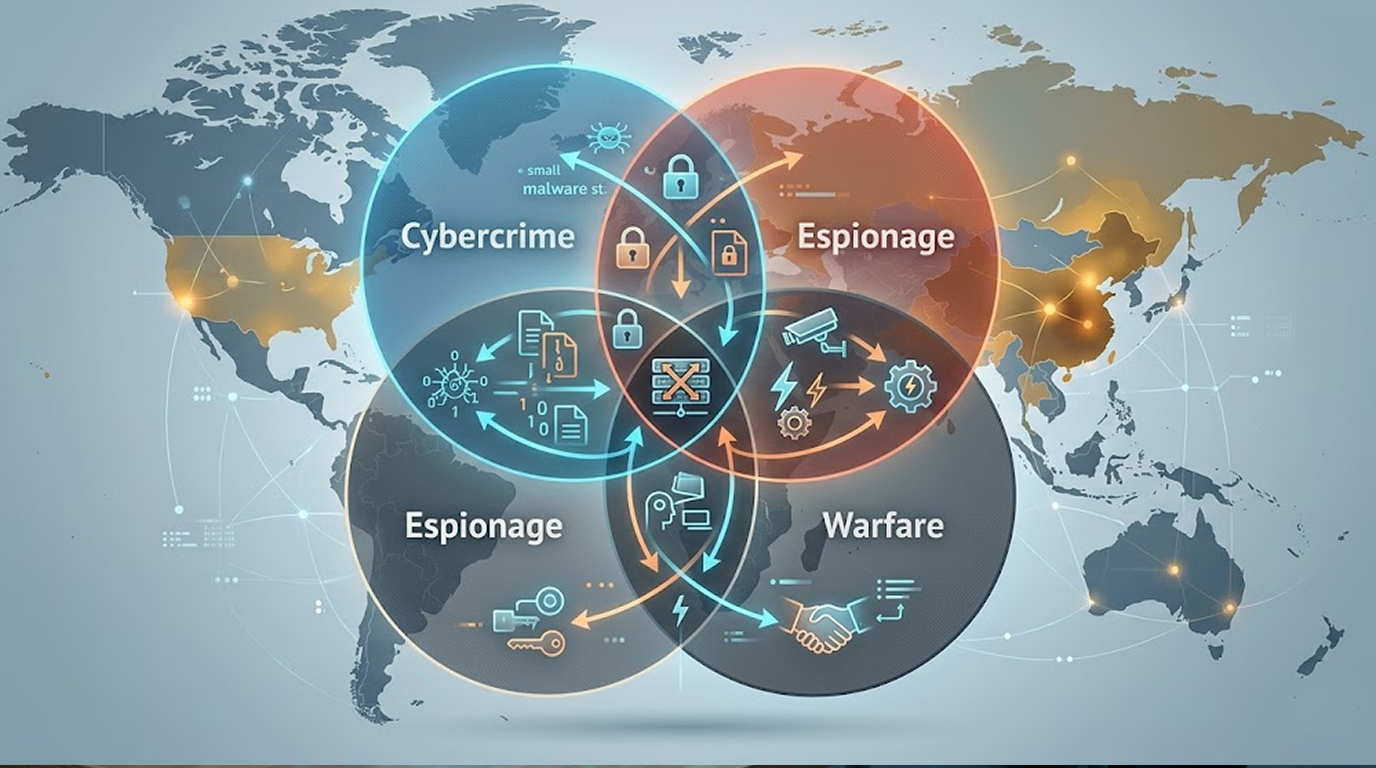
In 2026, the borders which had once separated different areas of cybercrime from government sponsored spying and that of cyber warfare is becoming less dis...
Ransomware used to be simple: encrypt your files, demand payment, and (hopefully) give you the decryption key. That model is now outdated. In 2026, almost...
One of the smartest and most satisfying defensive tricks is turning an attacker’s own reconnaissance against them. Instead of just closing exposed ba...
In 2026, the most damaging attacks rarely rely on exotic zero-days or nation-state tools. They exploit the same simple, long-standing gaps that companies k...
Leaked chats from ransomware groups (LockBit, ALPHV/BlackCat, Conti remnants, RansomHub affiliates, etc.) have given defenders a rare, unfiltered look into...
An example of unauthorized network authentication is when an attacker logs into your Wi-Fi, VPN, Active Directory, RDP, SSH, cloud console or any other ser...
Getting attackers out of a system or network feels like a win. But in many real cases, they come back. Why? Because they leave hidden ways in before you ev...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067