npm Malicious Packages Deploy Windows RAT Malware
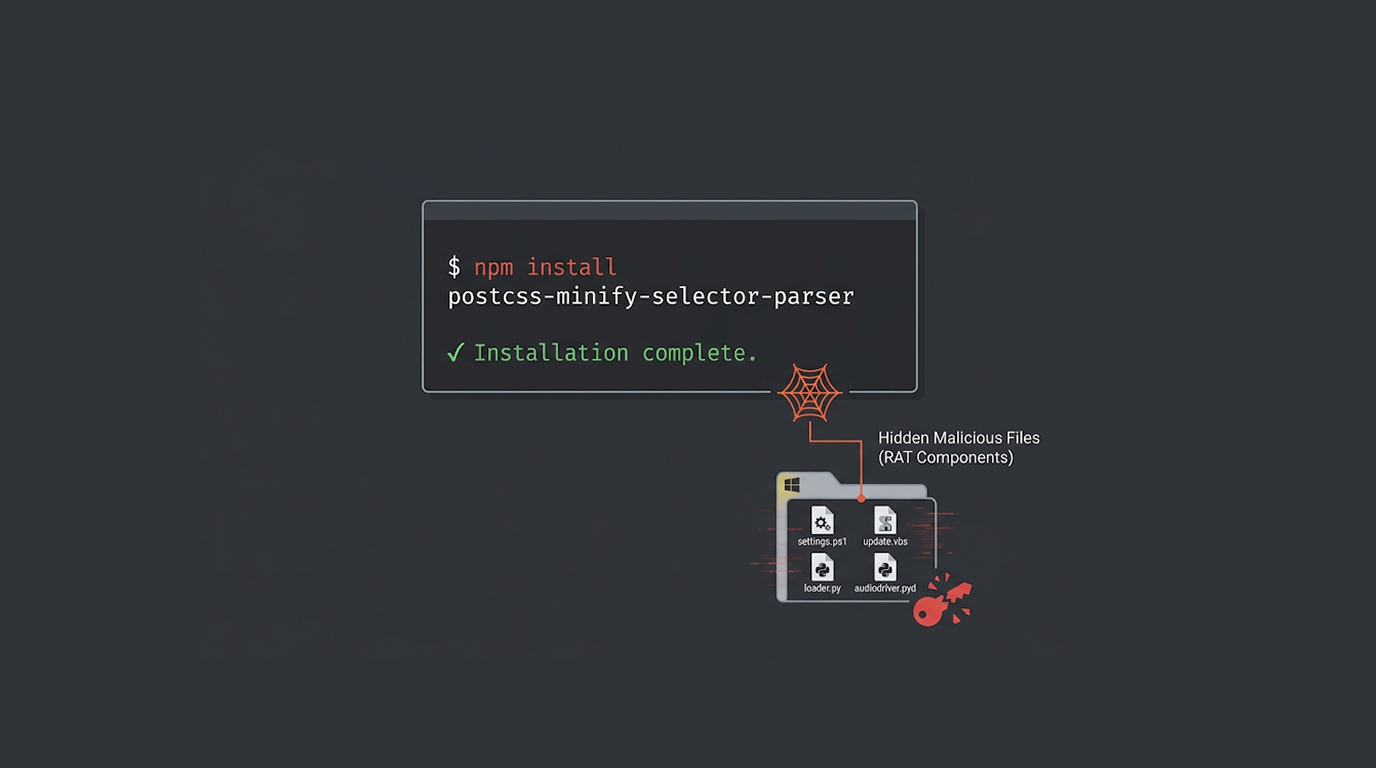
You install a package that looks like a legitimate build tool. It has a name similar to a popular library. It has hundreds of downloads. It seems safe. It...
Found 34 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You install a package that looks like a legitimate build tool. It has a name similar to a popular library. It has hundreds of downloads. It seems safe. It...
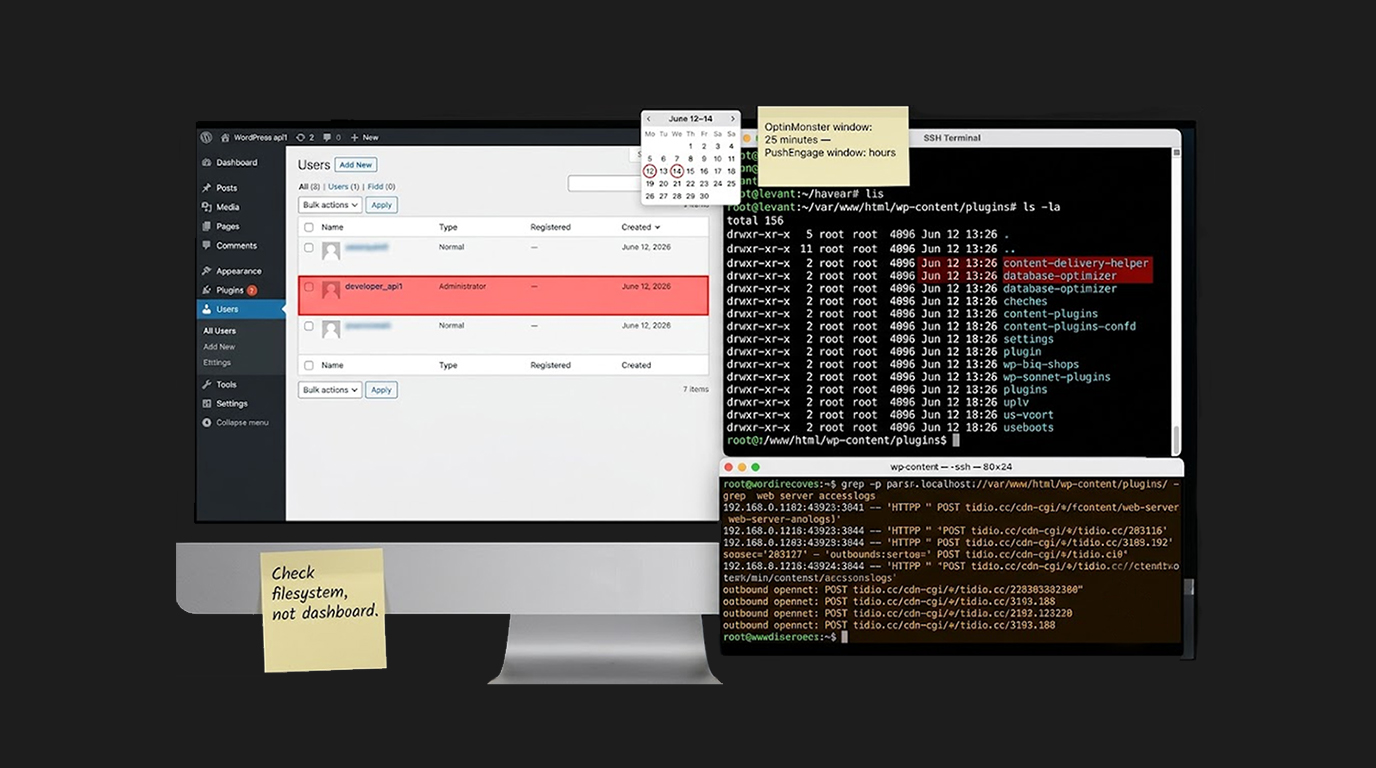
You install PushEngage for push notifications. OptinMonster for popups. TrustPulse for social proof. They are trusted brands. Millions of sites use them.La...
You are working on an important project. Your computer slows down. The cursor moves on its own. Files open and close without you touching the mouse. You a...
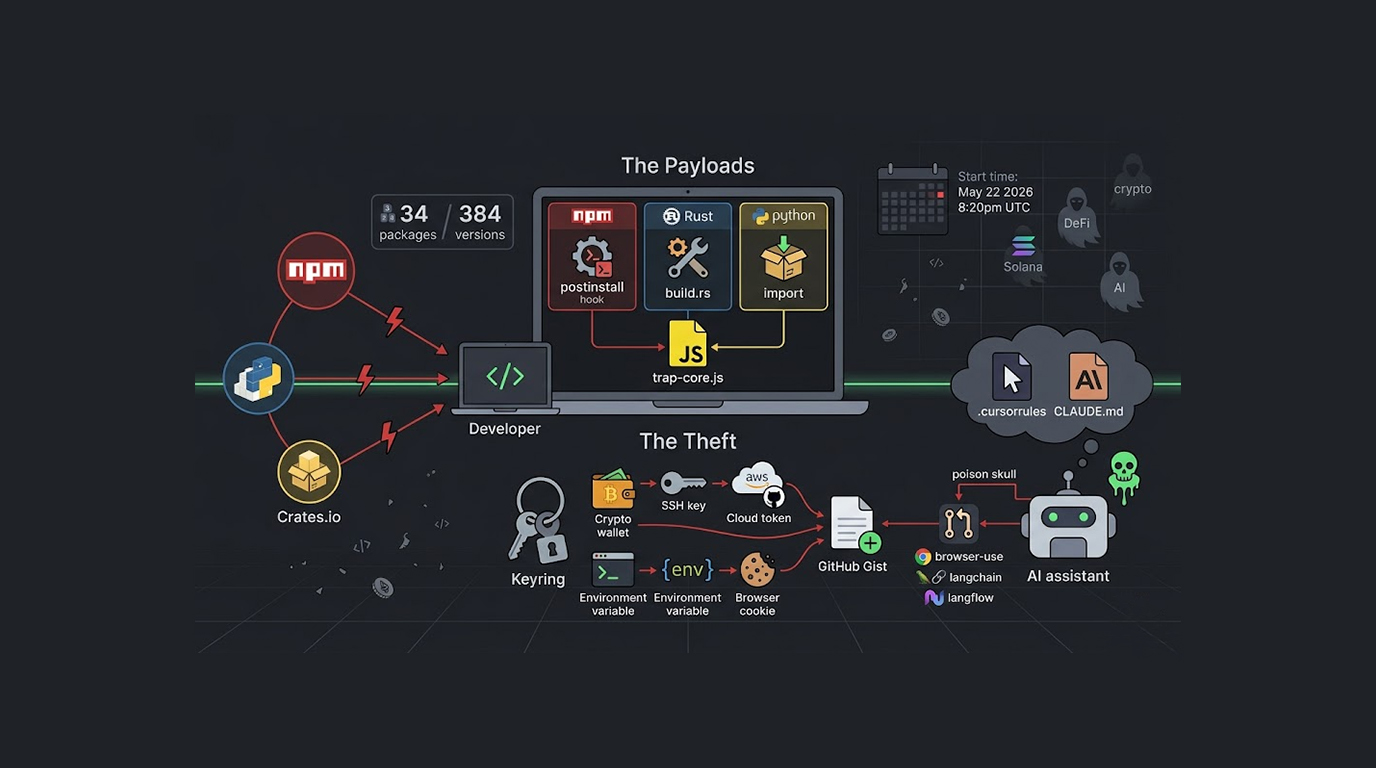
A new coordinated supply chain attack campaign has targeted three major package registries simultaneously, and the attackers are stealing developer credent...
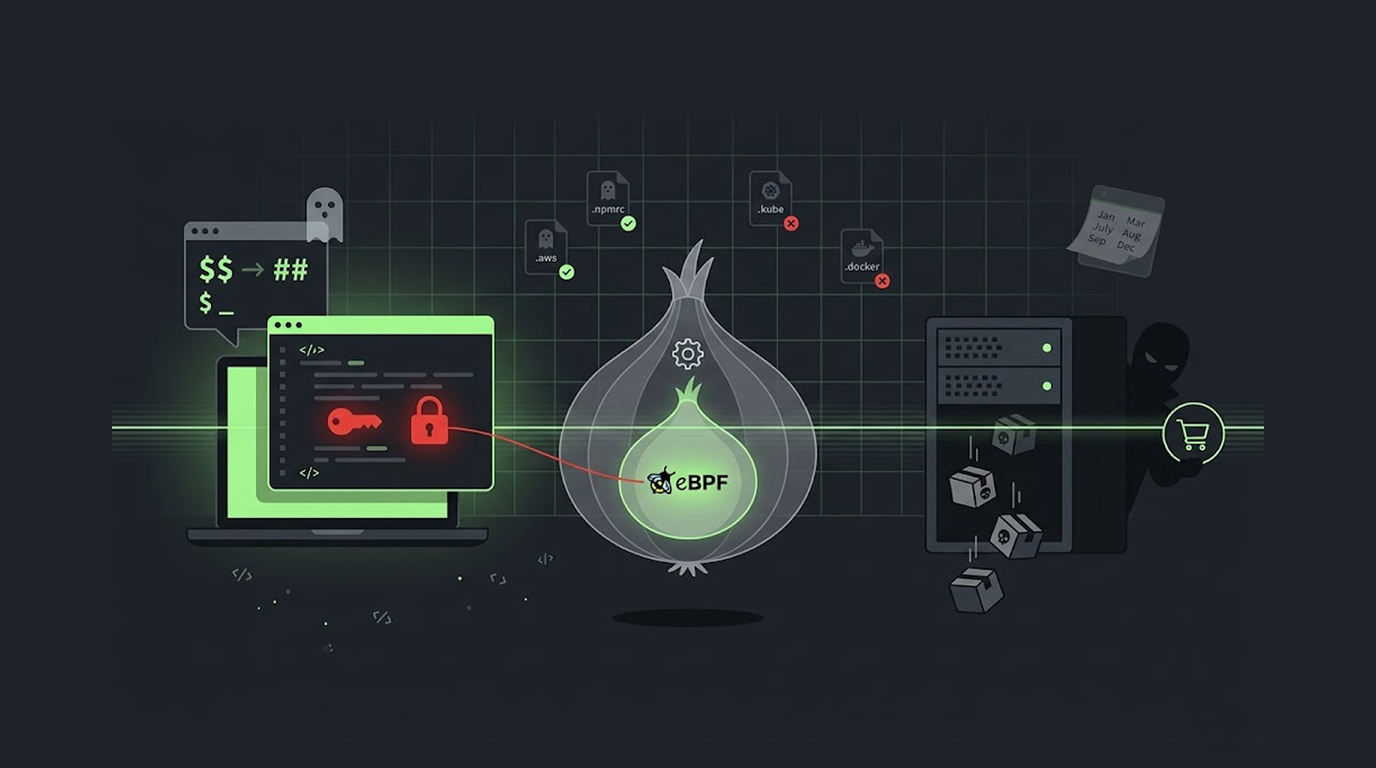
A developer sits down at their Linux workstation, pushes code, publishes packages, and manages cloud infrastructure, but they have no idea that every keyst...
On Discord, a friend sent you a file named "ZiChatBot_setup.exe" with a note saying to try it out because it's a great new chatbot app. You trusted your f...
A Chinese cybercrime group is pretending to be tax authorities in two different countries. Their goal? Deliver malware that steals data, controls systems,...
You do not have time for a 20-page threat intelligence report. You have a board meeting in an hour. Your SOC is flagging anomalies. And there is a new thre...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067