Car App Login Flaw: Default Password Unlocks Cars
Two researchers took over the login systems behind two car brands' mobile apps, and from there they unlocked doors and started engines. The entry point wa...
Found 389 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Two researchers took over the login systems behind two car brands' mobile apps, and from there they unlocked doors and started engines. The entry point wa...
There's a design decision at the centre of Claude Desktop that determines everything about its security posture, and it's not a bug or an oversight, it's t...
Nine hours. That is how long it took from CVE publication to the first exploitation attempt. The vulnerability is CVE-2026-123158, and it now has a name:...
OpenAI published two numbers on Thursday, and the second one is the interesting one. The first is 48.5%. That is GPT-6 Cyber's score on ExploitGym, a benc...
Scoping sounds like the easy part of incident response, because you already know how to search a filesystem and you already know how to read an audit log,...
Most people think of a browser extension as a small convenience. A password manager, an ad blocker, a tool that fixes some annoyance on a website. Forever...
A hosting control panel is a high-value target for one obvious reason. Root access to the panel is root access to every website on the server. Researchers...
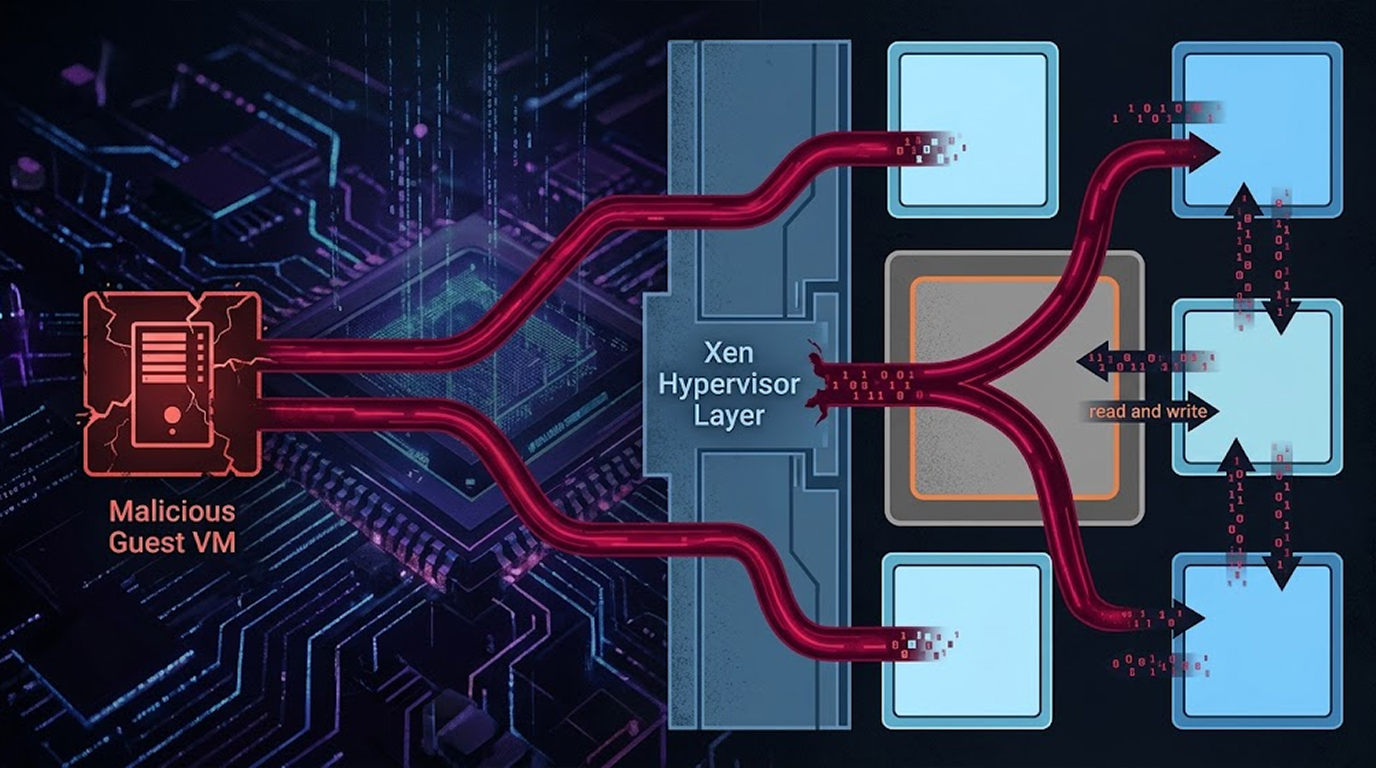
Two flaws in the Xen hypervisor allow a malicious guest virtual machine to read and write the memory of other VMs on the same host. That includes dom0, the...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067