Notepad++ Arbitrary Code Execution via config.xml Injection
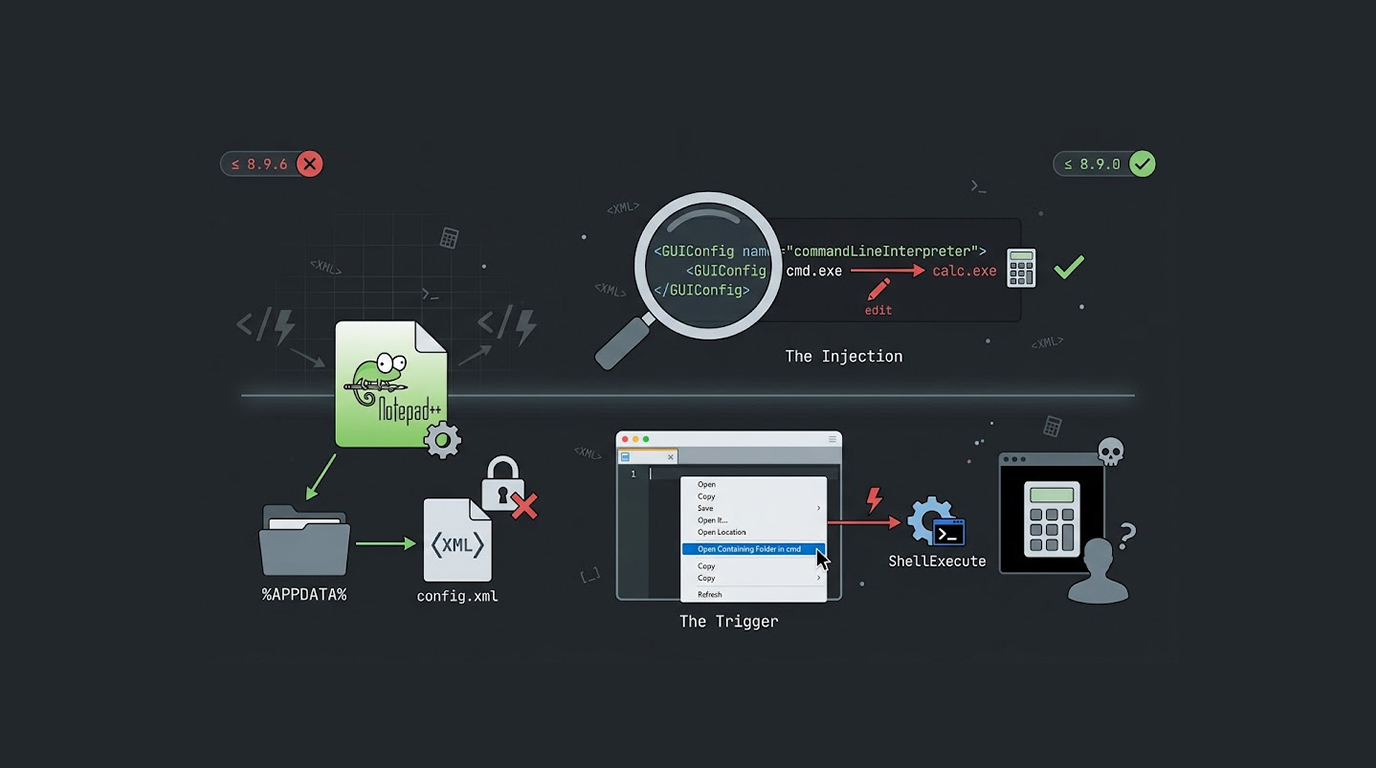
A vulnerability was found in Notepad++ that permits attackers to execute any arbitrary code by modifying a configuration file. The vulnerability affects al...
Found 27 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A vulnerability was found in Notepad++ that permits attackers to execute any arbitrary code by modifying a configuration file. The vulnerability affects al...
In 2026, malware developers are becoming interested in Zig due to its use as a modern day replacement for C as a systems programming language. Whereas legi...
A China-based cybercriminal group known as Silver Fox (also referred to as SwimSnake / Valley Thief / Void Arachne) is currently using a typosquatting tech...
Kaspersky has shed light on a persistent phishing campaign tied to the threat actor Bloody Wolf (tracked by Kaspersky as Stan Ghouls), which has been quiet...
Signed Windows tools are:1. Trusted by the operating system2. Often allowed by security policies3. Installed by default Attackers don’t need malware...
Breaking web apps usually doesn’t start with zero-days or Hollywood hacking.It starts with someone opening the same tools developers and testers alre...
Not every attack relies on PowerShell, SMB, or RDP.There’s a long tail of tools that look harmless, or “IT-related” in logs.That’s...
One of the more uncomfortable moments in incident response is realizing nothing new was installed.No malware alerts.No suspicious downloads.Everything used...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067