Microsoft Defender Privilege Escalation Exploited in Wild
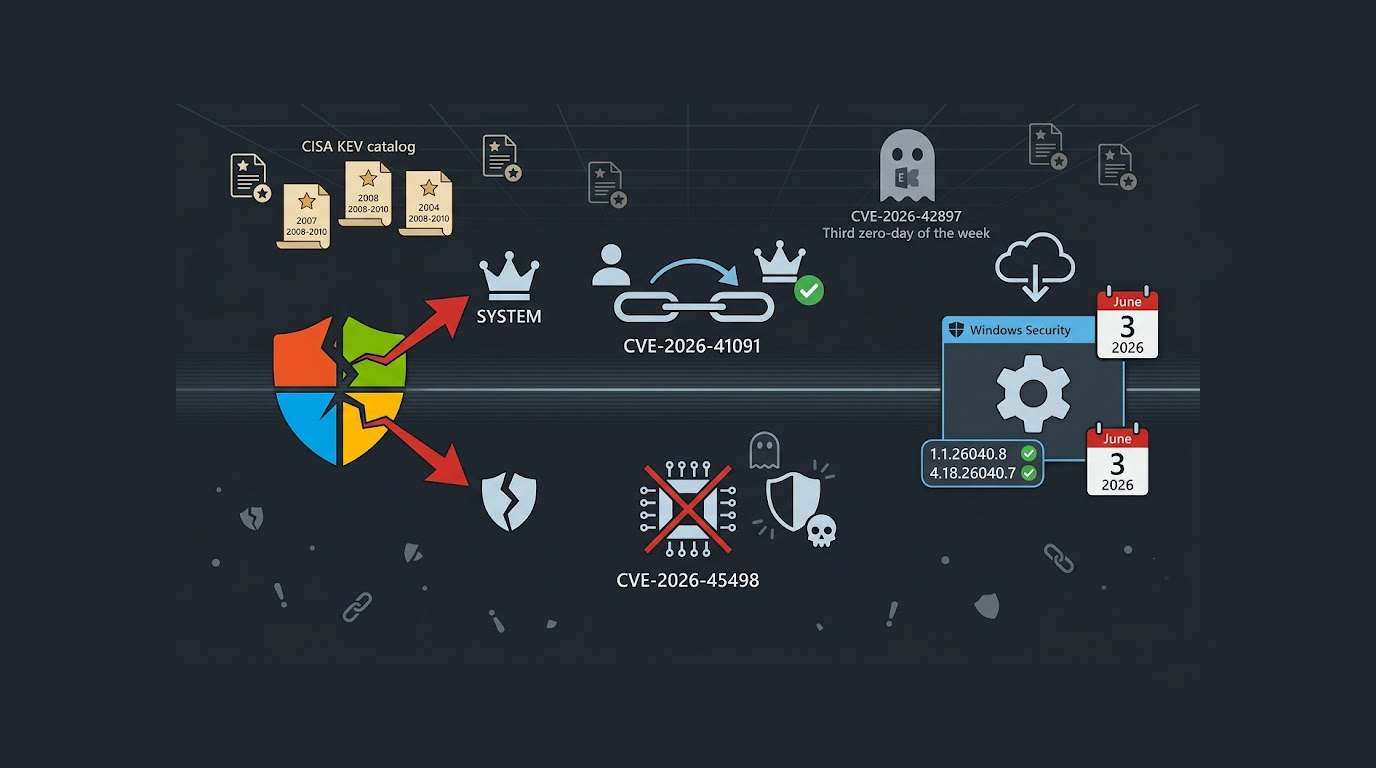
Microsoft has disclosed that two vulnerabilities in Microsoft Defender are under active exploitation, and one of these flaws allows an attacker to gain SYS...
Found 20 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Microsoft has disclosed that two vulnerabilities in Microsoft Defender are under active exploitation, and one of these flaws allows an attacker to gain SYS...
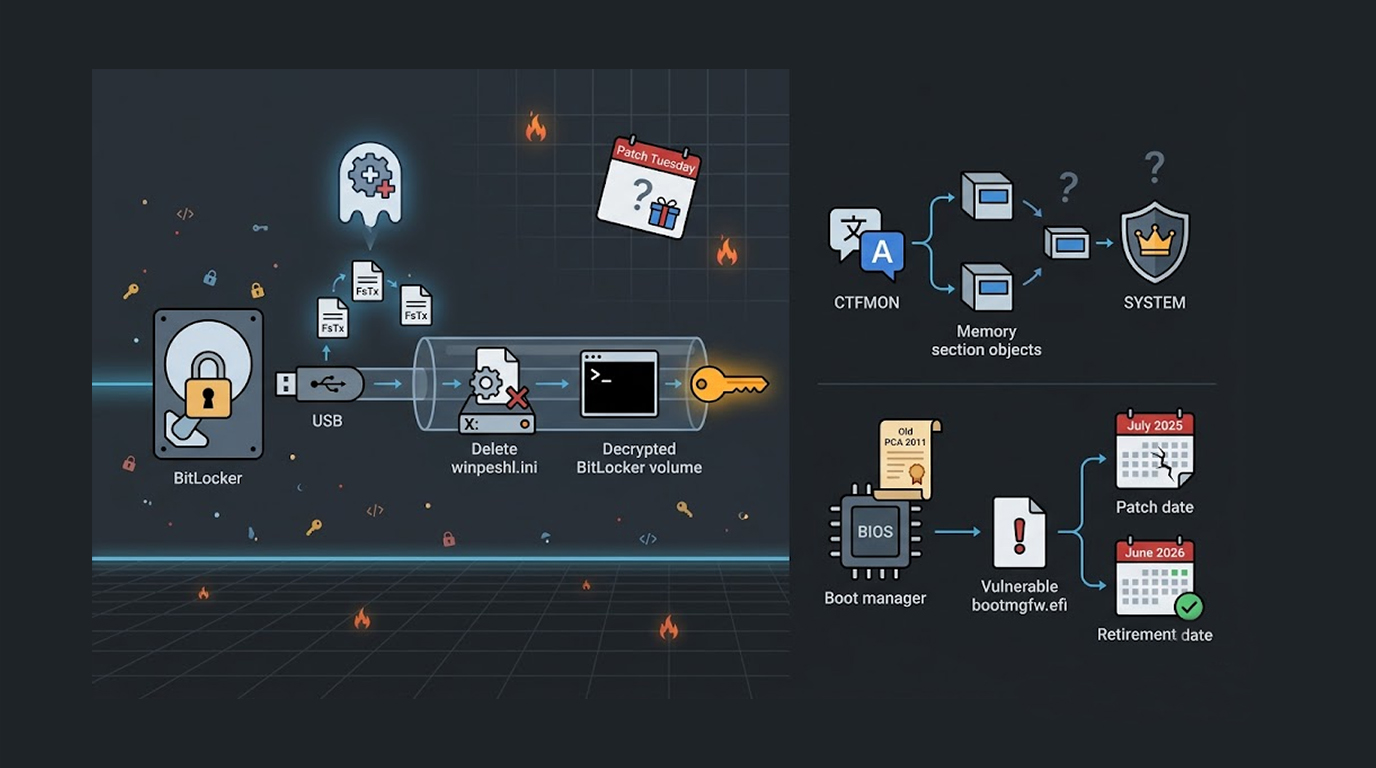
An anonymous security researcher who previously disclosed three Microsoft Defender zero-days is back with two more, and these new flaws affect BitLocker an...
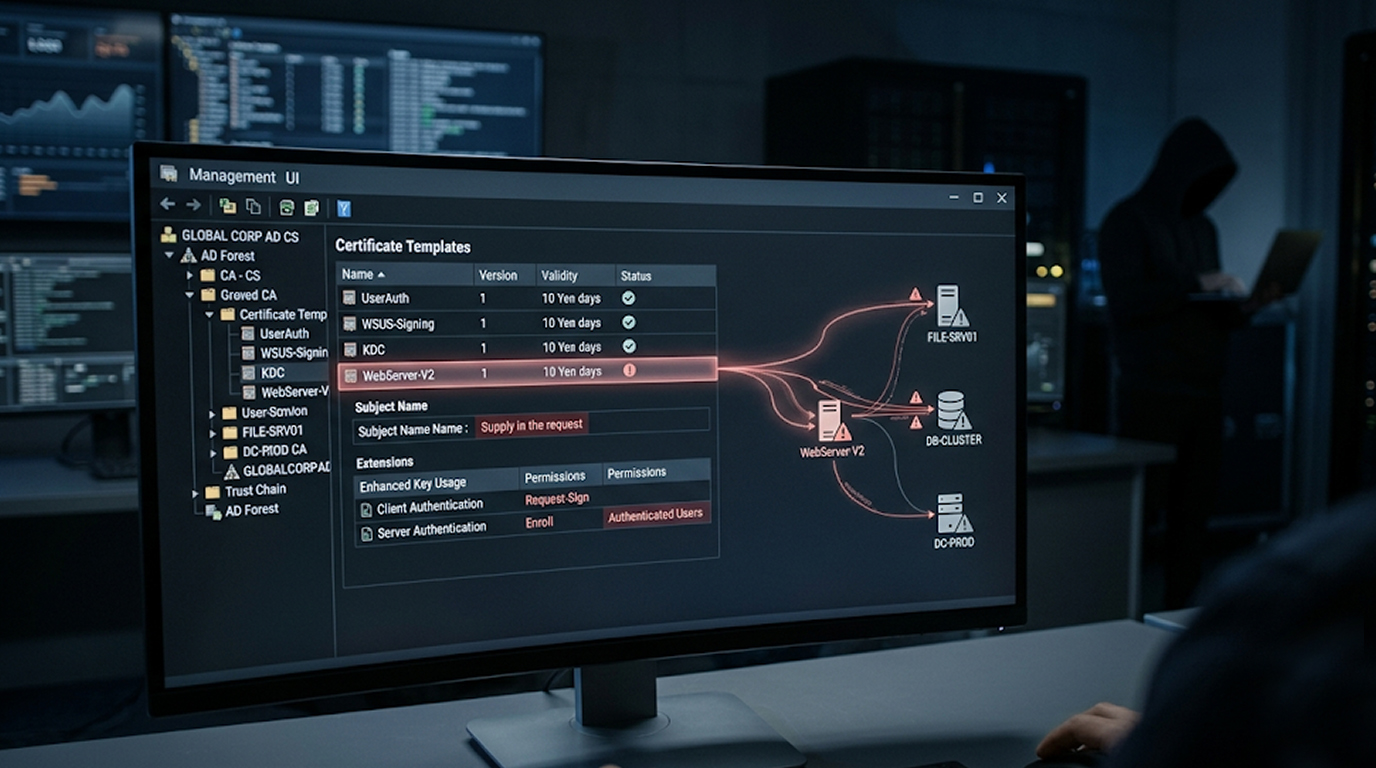
Active Directory Certificate Services (AD CS) is everywhere in enterprise Windows environments. And everywhere means opportunity.If you have done any inter...
A privilege escalation vulnerability has been identified in NetBT e-Fatura, a widely used electronic invoicing solution in Turkey. Tracked as CVE-2025-140...
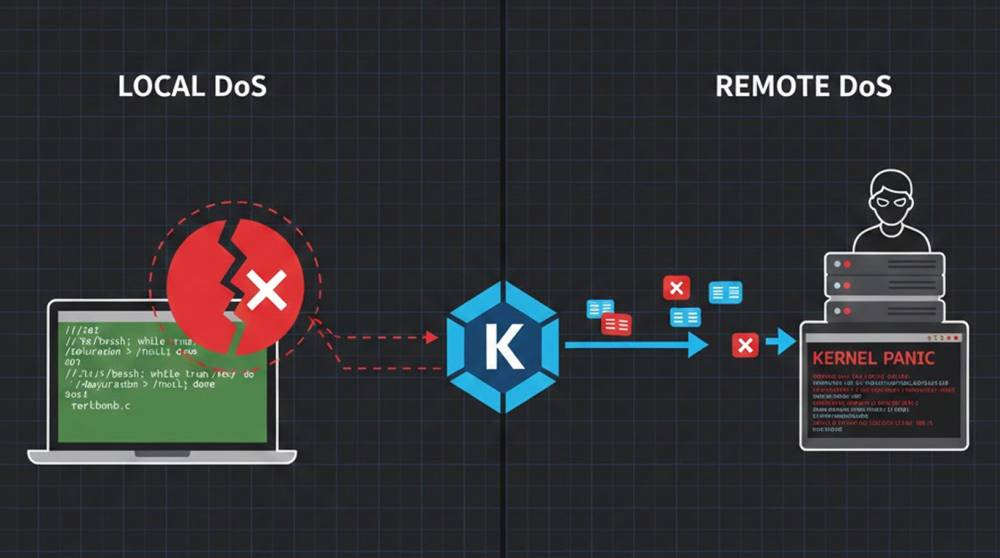
By exploiting the operating system kernel, attackers can create a denial of service through either crashing the OS kernel, freezing the system or consuming...
File upload vulnerabilities (CWE-434) let attackers drop webshells, small scripts that provide remote command execution, file management, and persistence o...
Running a vulnerability scanner often gives you a long list of findings. Many are low-priority noise, but a few high/critical issues appear again and again...
Ethical hacking can only be conducted legally and safely. Building a home lab allows you to establish a safe and legal environment to simulate attacks, dev...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067