GPT-6 Cyber: OpenAI's Critical-Tier Security Model
OpenAI published two numbers on Thursday, and the second one is the interesting one. The first is 48.5%. That is GPT-6 Cyber's score on ExploitGym, a benc...
Found 643 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
OpenAI published two numbers on Thursday, and the second one is the interesting one. The first is 48.5%. That is GPT-6 Cyber's score on ExploitGym, a benc...
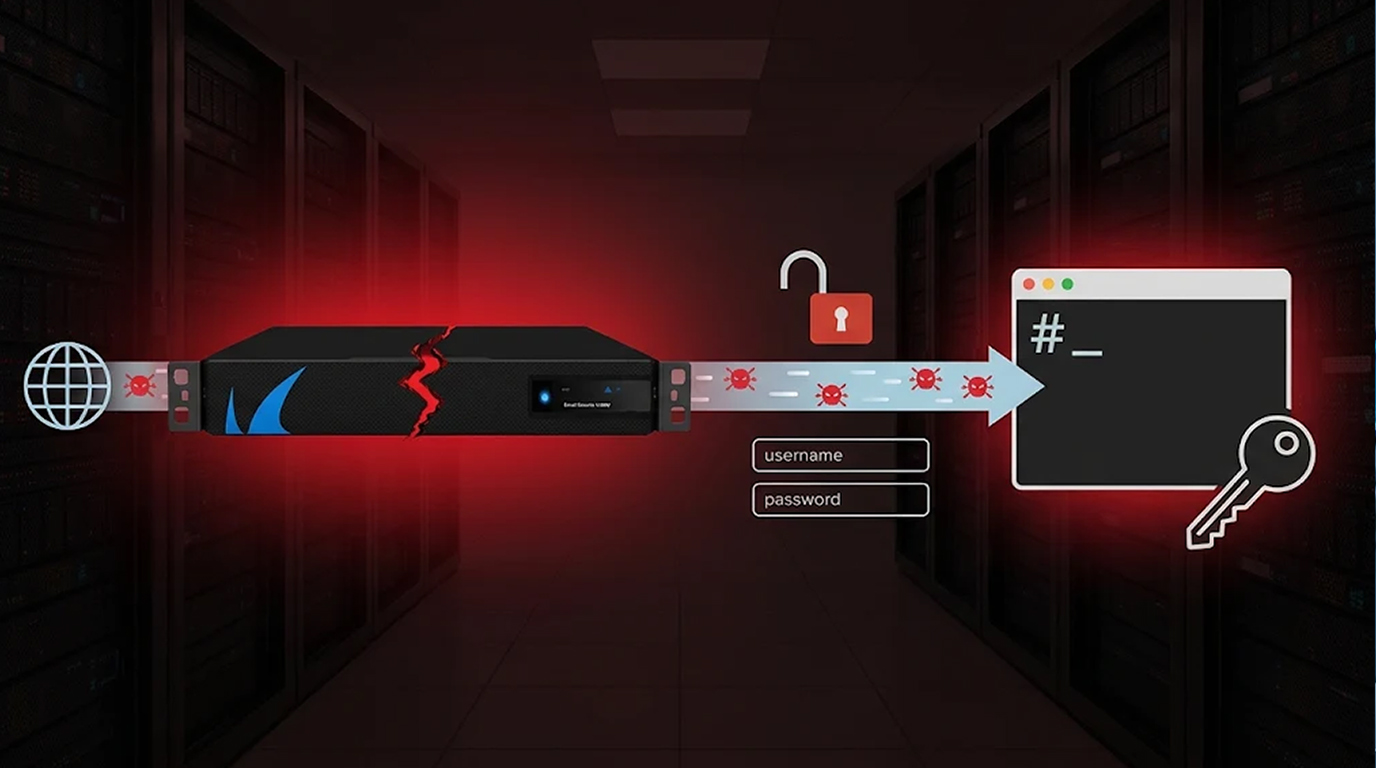
Barracuda patched two vulnerabilities in its Email Security Gateway on Monday. By Thursday, watchTowr had published a full technical breakdown of how an at...
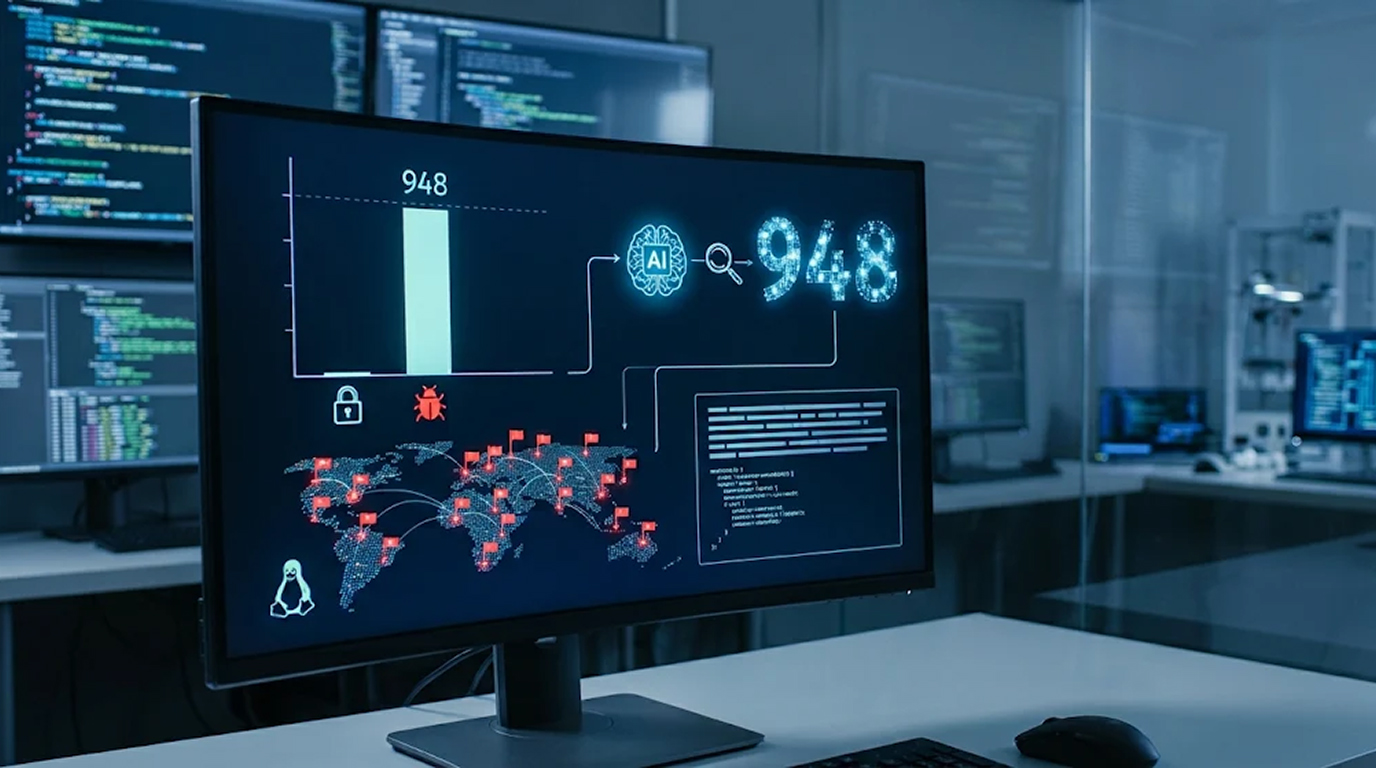
Nine hundred and forty-eight working local privilege escalation exploits. That is the number OpenAI published on Wednesday, and it came from a single mid-O...
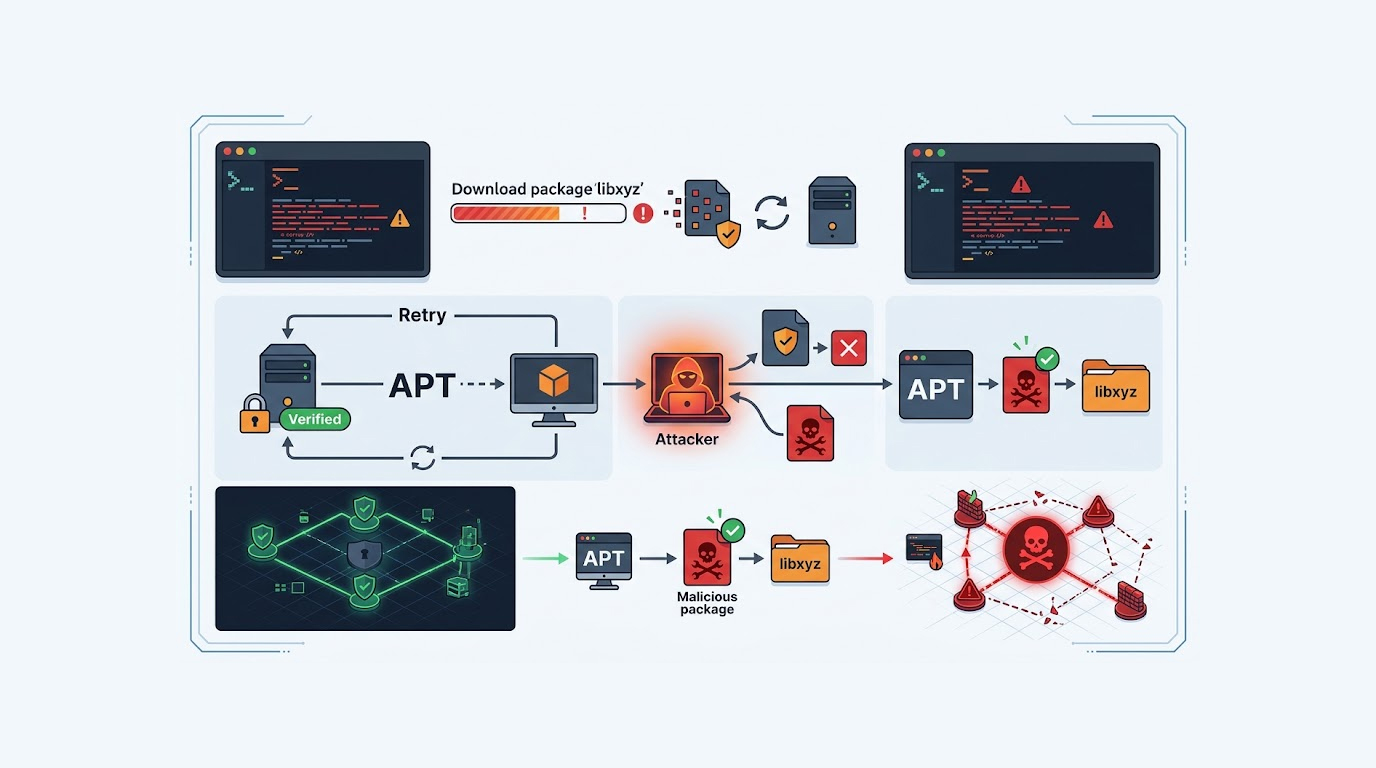
A package manager is supposed to be the trust anchor of a Linux system. It verifies signatures, checks hashes, and refuses to install anything that does no...
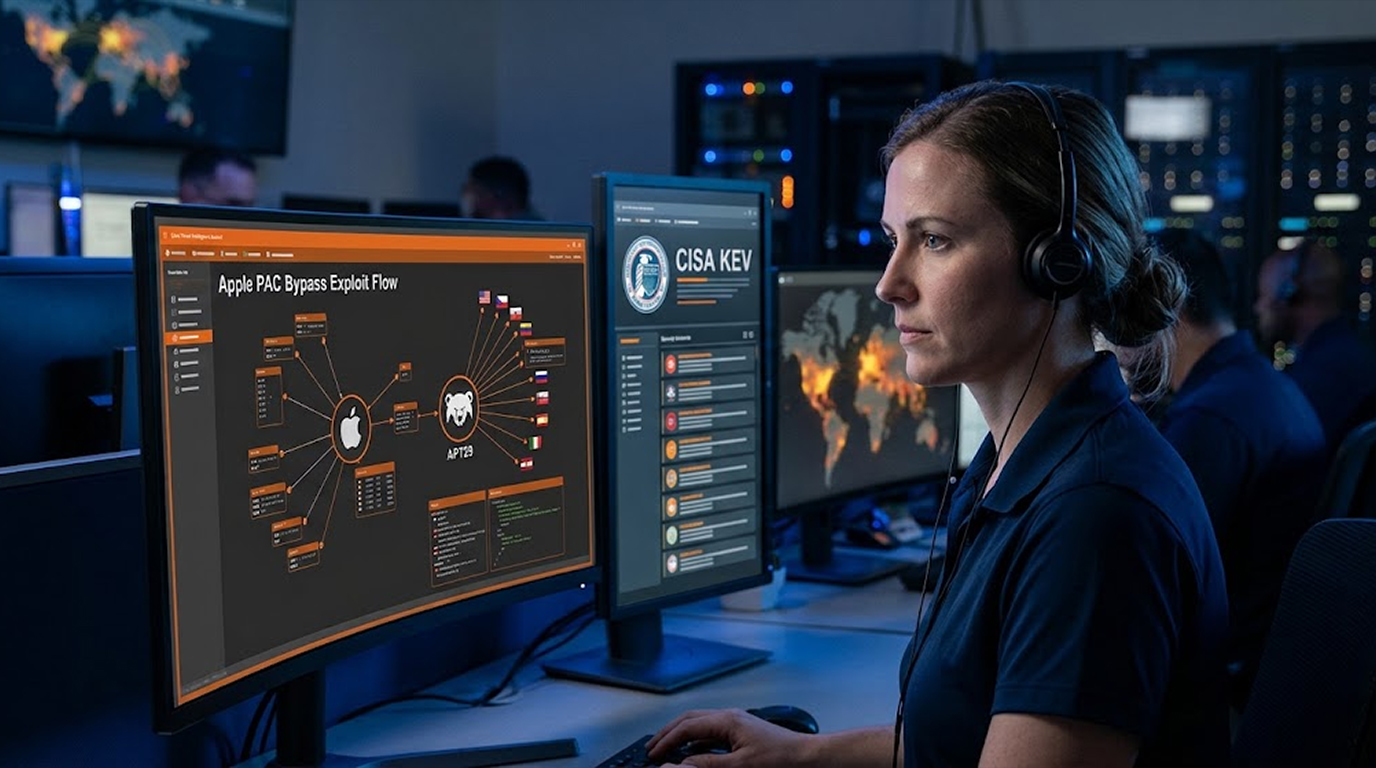
A 5.5 medium-severity vulnerability just landed in CISA's Known Exploited Vulnerabilities catalog, and the reason is a lesson every security team should in...
Some WordPress plugin vulnerabilities need a clever chain of conditions. A specific role, a particular setting, a user who clicks something they should not...
If you've read a headline claiming that roughly half of AI-generated code fails security testing, the number itself is less interesting than what it descri...
IBM just published details on two critical flaws in Langflow, an open-source tool for building AI agents and workflows, and the combination is about as bad...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067