Detecting Data Exfiltration: Practical Indicators
Data exfiltration is the silent killer in most modern attacks. Whether it’s a ransomware group preparing for double extortion, a nation-state actor s...
Found 30 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Data exfiltration is the silent killer in most modern attacks. Whether it’s a ransomware group preparing for double extortion, a nation-state actor s...
Local AI malware represents a major shift in 2026. Instead of sending everything to a remote C2 server, these threats embed small on-device language models...
Most organizations have a WAF and firewall, but a surprising amount of malicious traffic still slips through because the rules are either too generic or fo...
One of the best ways to identify early-stage intruders (i.e., stalking while still being able to gain access to valuable information) is through the use of...
Many security tools, remote-desktop solutions, banking apps, crypto wallets, trading platforms, and even some games now run “user presence” or...
Quiet corporate sabotage seldom presents itself via loud headlines or visible destruction and its movement is one which takes time, remains inconspicuous a...
Event ID 4103 (Module Logging) and 4104 (Script Block Logging) are two of the most valuable Windows security events for detecting malicious PowerShell acti...
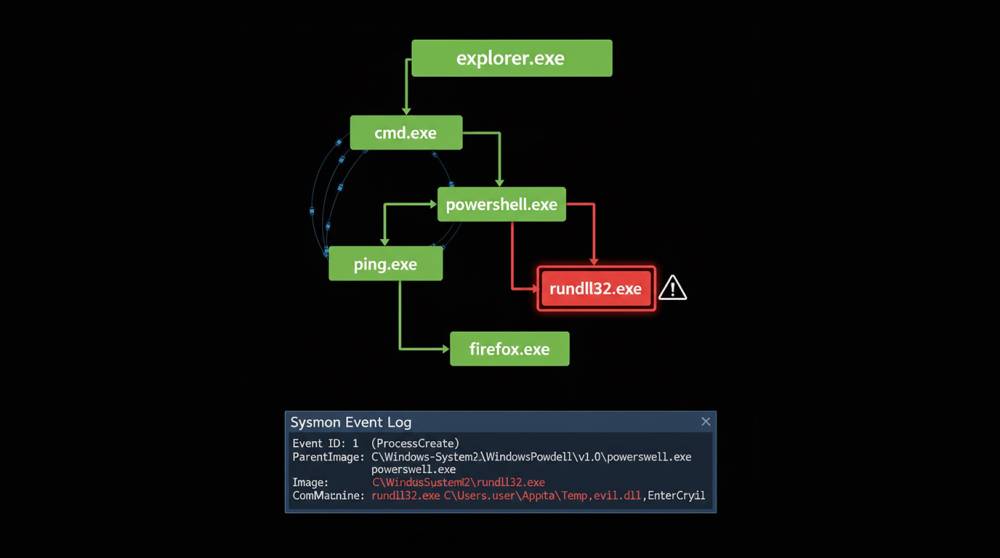
Process ancestry monitoring tracks the parent-child relationships between processes (who spawned what). This is one of the most reliable ways to detect liv...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067