Redis HLL Overflow → RCE in 8.0.0–8.0.2
A serious remote code execution vulnerability (CVE-2025-32023) was identified in Redis HyperLogLog (HLL) for all versions greater than (>=) 8.0.0 but le...
Found 174 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A serious remote code execution vulnerability (CVE-2025-32023) was identified in Redis HyperLogLog (HLL) for all versions greater than (>=) 8.0.0 but le...
SmarterTools has resolved two high-priority security holes found in its SmarterMail program for sending and receiving emails (or just mailing), including o...
Palo Alto Networks has released security updates to fix a critical vulnerability in GlobalProtect Gateway and Portal that could lead to a denial-of-service...
ode.js has created urgent security updates that will help to rectify a high level of security vulnerabilities. One vulnerability allows an attacker to crea...
The Cybersecurity Agency of Singapore (CSA) has issued a high-priority alert concerning a serious cybersecurity flaw in the SmarterTools SmarterMail Email...
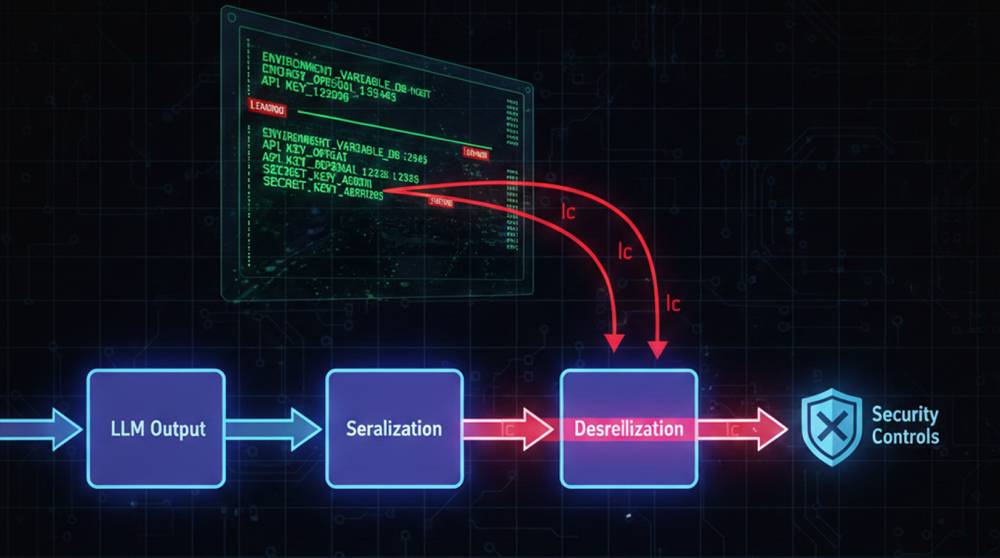
Security researchers have discovered a serious flaw in LangChain Core that could be exploited by malicious users to access confidential secrets by manipula...
Cisco has confirmed active exploitation of a maximum severity zero day vulnerability affecting Cisco AsyncOS, the operating system behind Cisco Secure Emai...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a new warning after confirming that a severe vulnerability in Oracle Identity M...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067