Microsoft and DoJ Seize 107 Domains Used by Russian State-Sponsored Hackers
On Thursday, Microsoft and the U.S. Department of Justice (DoJ) announced the seizure of 107 internet domains linked to Russian state-sponsored cybercrimin...
Found 1023 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
On Thursday, Microsoft and the U.S. Department of Justice (DoJ) announced the seizure of 107 internet domains linked to Russian state-sponsored cybercrimin...
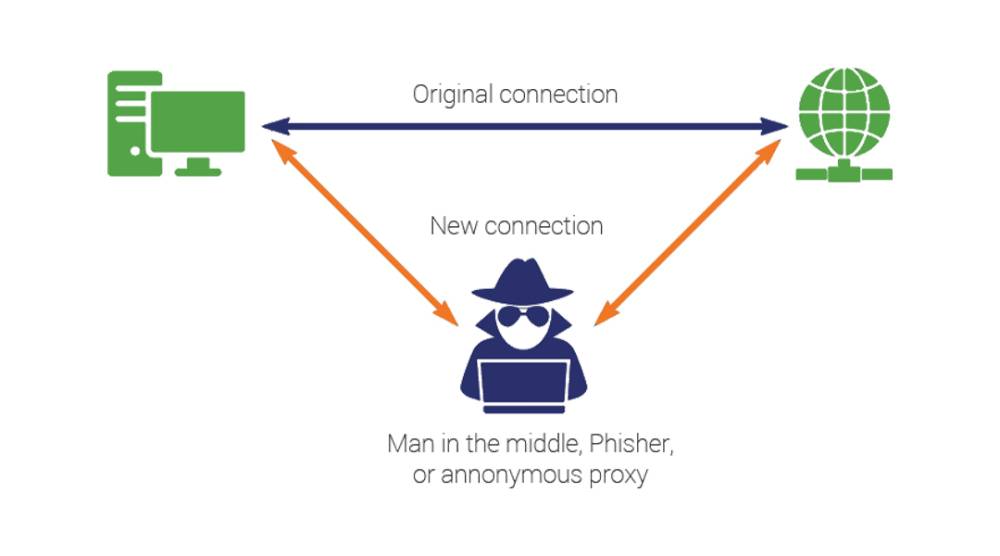
Man-in-the-Middle (MitM) attacks are a dangerous type of cyberattack where an attacker secretly intercepts and possibly alters the communication between tw...
Cross-Site Scripting (XSS) attacks are among the most common and dangerous types of security vulnerabilities found in web applications. XSS attacks occur w...
Misconfigured and vulnerable Linux servers have become the latest target of a stealthy malware campaign delivering a threat dubbed perfctl, primarily aimed...
INTERPOL has announced the arrest of eight individuals in Côte d'Ivoire and Nigeria as part of Operation Contender 2.0, a targeted effort to combat p...
A high-severity security flaw has been disclosed in the LiteSpeed Cache plugin for WordPress, potentially allowing attackers to execute arbitrary JavaScrip...
As technology advances, so does the sophistication of malware, leading to an increasingly complex threat landscape. Malware, short for malicious software,...
A large-scale fraud campaign leveraged fake trading apps published on the Apple App Store and Google Play Store, as well as phishing sites, to defraud vict...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067