LMDeploy SSRF Vulnerability Exploitation Seen Within 13 Hours
A critical security flaw in a popular open-source LLM toolkit was published on GitHub. Within half a day, attackers were already using it in the wild. The...
Found 200 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A critical security flaw in a popular open-source LLM toolkit was published on GitHub. Within half a day, attackers were already using it in the wild. The...
You run a vulnerability scan. You fix the critical findings. You feel safe.Then a real attacker breaks in through a phishing email your security team never...
For nearly two decades, cybersecurity experts believed Stuxnet was the first digital weapon built for physical destruction. That timeline just changed. Re...
A popular open-source workflow automation platform is being turned against its users. Threat actors have discovered how to abuse n8n, a tool designed to co...
As the cybersecurity industry continues to advance at an accelerated pace, new vulnerabilities pose increased potential for both rewards and risk by being...
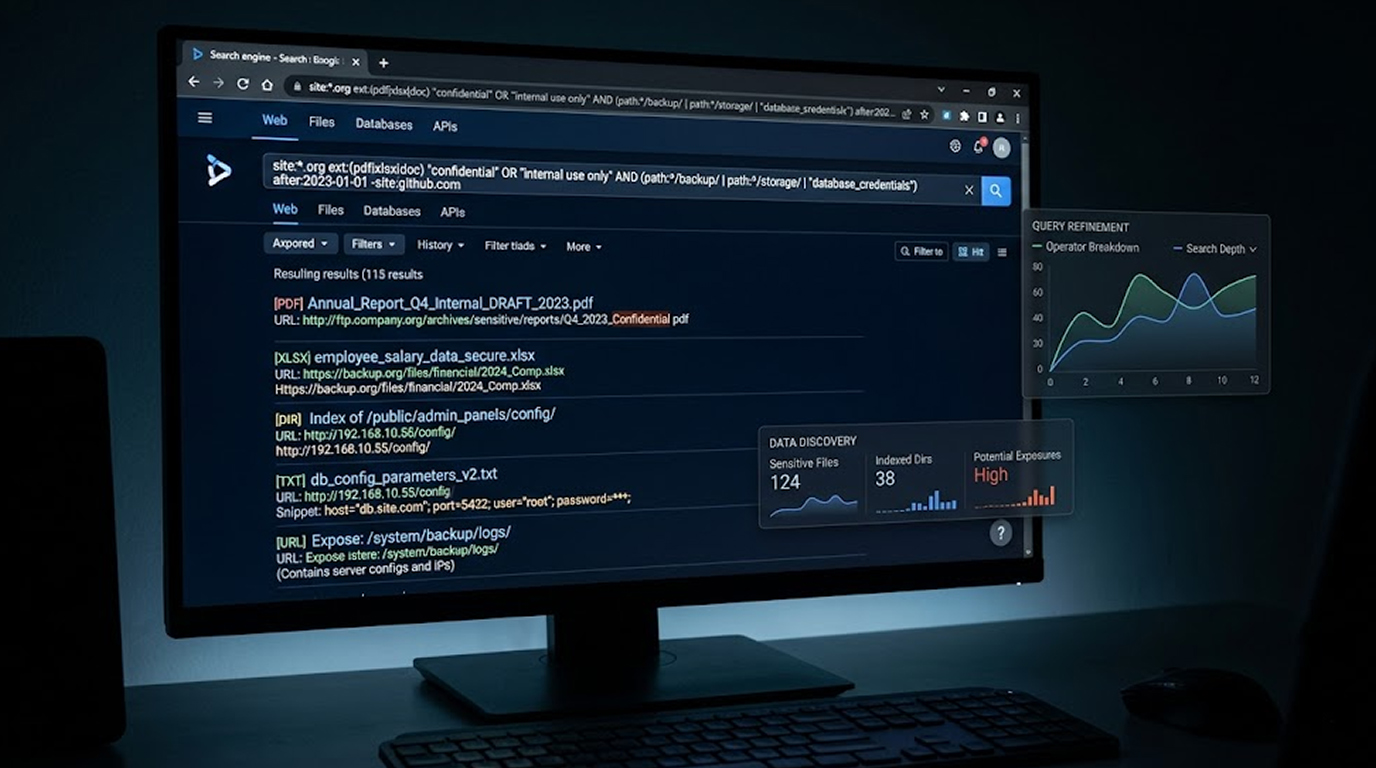
Google dorking has always been one of the most powerful reconnaissance tools in a hacker’s arsenal. But something massive changed in the last two yea...
There is an increase in supply chain attacks against open-source packages in 2026. Hackers or other malicious actors will either publish or compromise pack...
Cybersecurity researchers have warned that cybercriminals are currently leveraging a serious remote code execution vulnerability in Flowise – a widel...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067