Authentication State Attacks: Hidden Flags Bypass
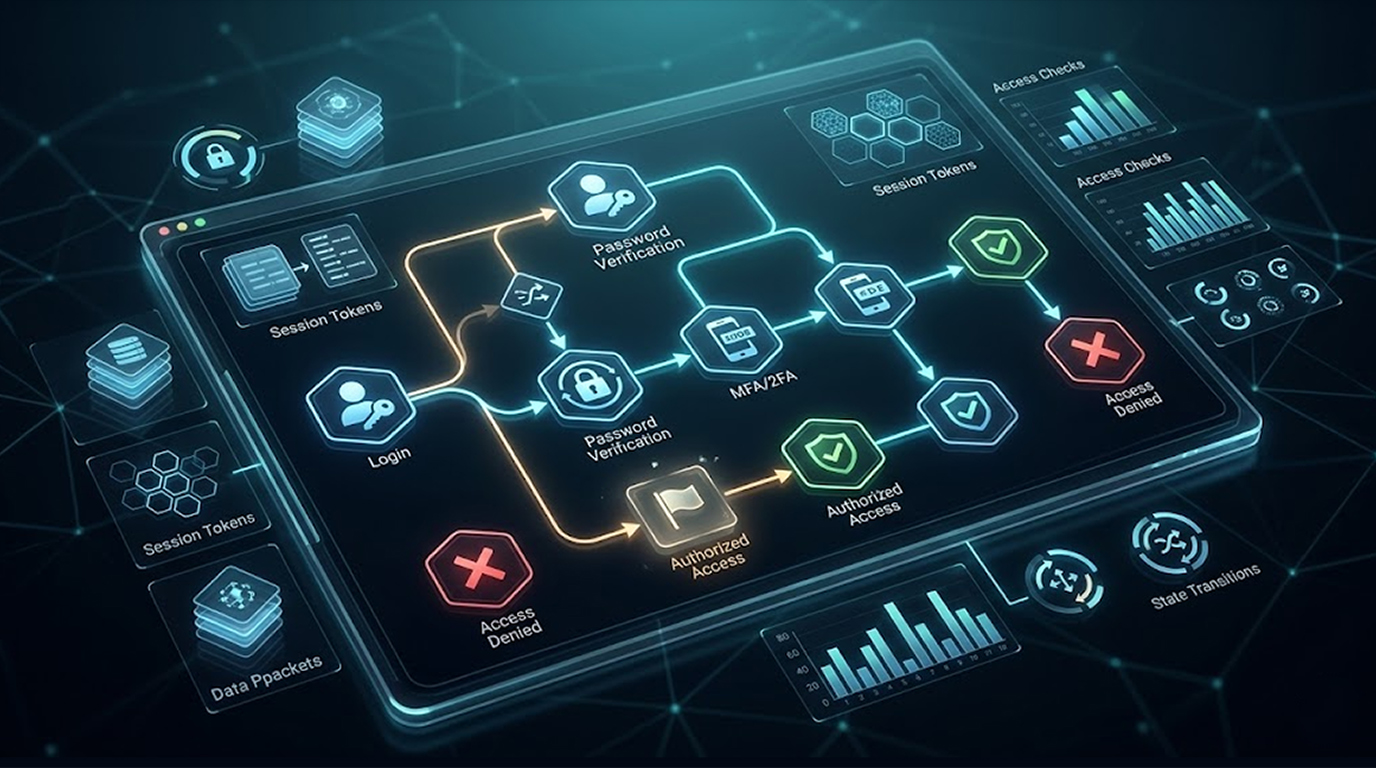
Authentication state attacks take advantage of weakness in how applications manage login sequences and states. Rather than using encryption or guessing a p...
Found 141 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Authentication state attacks take advantage of weakness in how applications manage login sequences and states. Rather than using encryption or guessing a p...
The use of shared credentials like AWS access keys, Azure service principal credentials, GCP service account keys and the reuse of passwords between differ...
A privilege escalation vulnerability has been identified in NetBT e-Fatura, a widely used electronic invoicing solution in Turkey. Tracked as CVE-2025-140...
While the comment box may appear to be a benign feature of a website (i.e., a place for users to submit their feedback), at its core, it can become an entr...
Ethical hacking and penetration testing aren't just careers, they're mindsets. Whether you're reconning targets, chaining exploits, writing reports, or def...
We’ve entered the phase where the most interesting (and dangerous) cyber conflicts are no longer human hacker vs. human defender. They’re incre...
There is an urgent update from Google for their browser due to a zero-day vulnerability that is currently being used by attackers in the wild. CVE-2026-24...
AccessEnum is one of those Sysinternals tools that quietly does a ton of work with almost no effort. It's free, tiny (under 150 KB), doesn't need to be ins...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067