Keyv npm Worm Spreads Credential-Stealing Malware
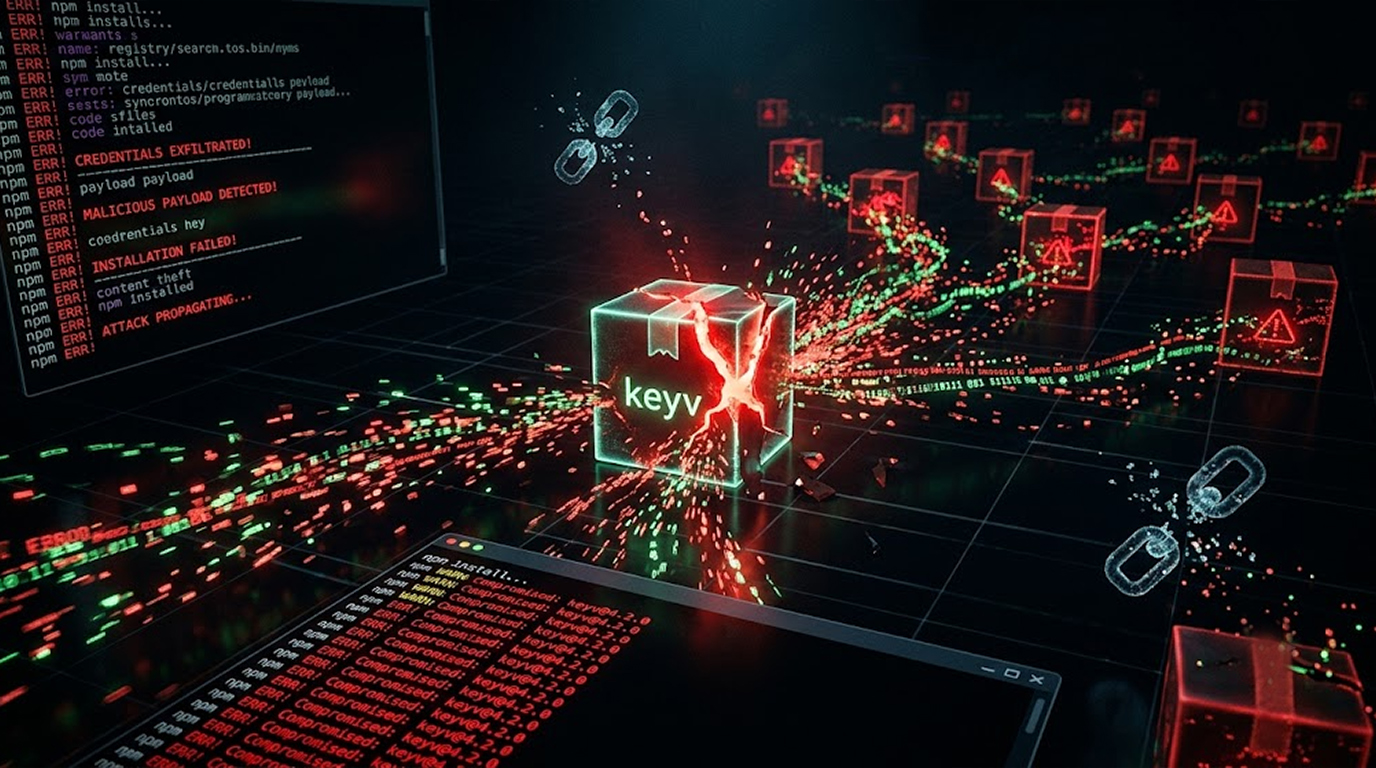
An npm worm targeting credentials was released for the first time in keyv@6.0.0 on August 4, 2026. From there, it spread beyond the Keyv and Cacheable name...
Found 302 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
An npm worm targeting credentials was released for the first time in keyv@6.0.0 on August 4, 2026. From there, it spread beyond the Keyv and Cacheable name...
cPanel has released a targeted security update addressing a vulnerability that could let an authenticated hosting customer execute SQL in the database's ro...
You have an AI chatbot. It is answering customer questions. It is summarizing documents. It is helping your team write code. But what happens when someone...
Imagine this. A teenager in their bedroom, someone who barely knows how to code, just built a piece of spyware that can break into your computer, steal you...
Here’s what happens. You are sitting at your desk, checking your WhatsApp, and there’s a file on WhatsApp sent to you by one of your colleagues...
You have just recovered your hacked Instagram account. You changed the password. You enabled two-factor authentication. You are relieved. Three days later...
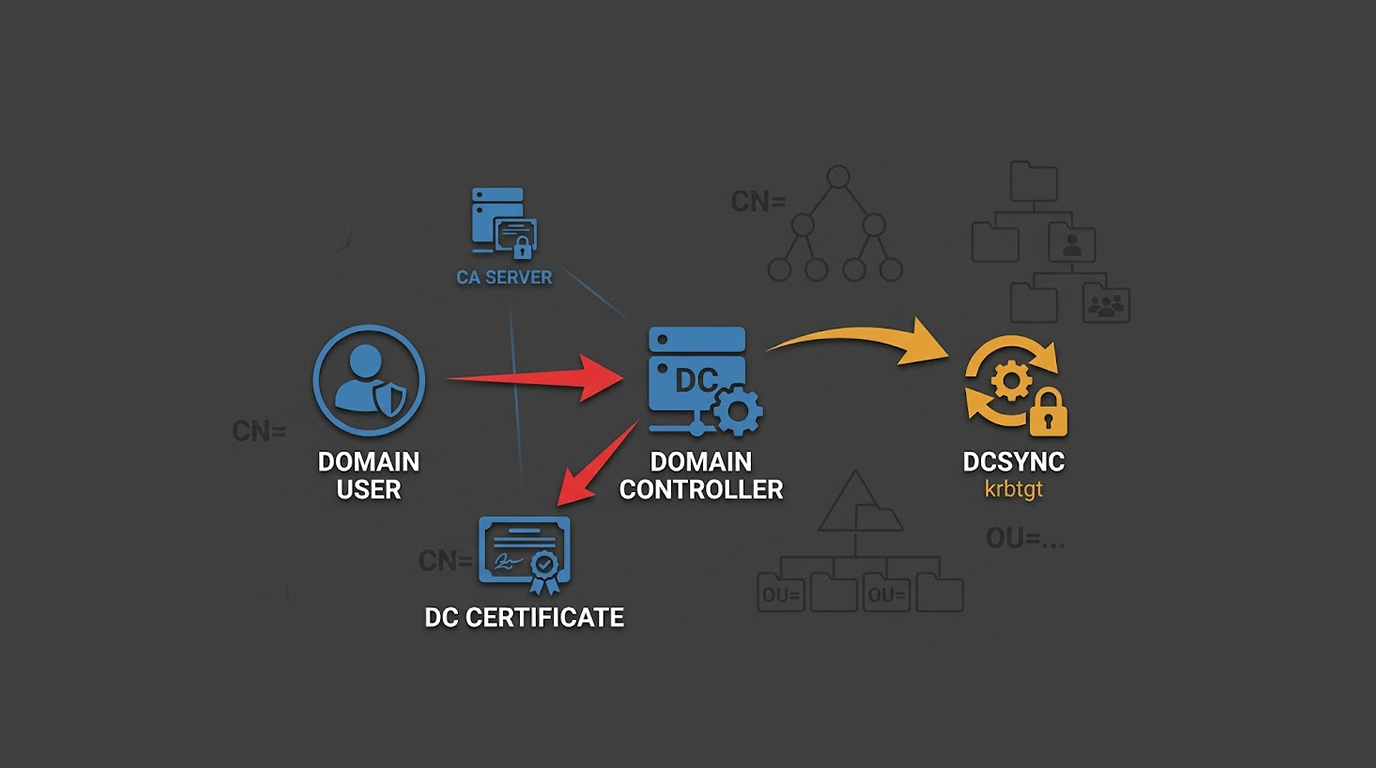
Let me paint you a picture. A regular employee with basic domain user privileges, no admin rights, no special access can walk away with a certificate that...
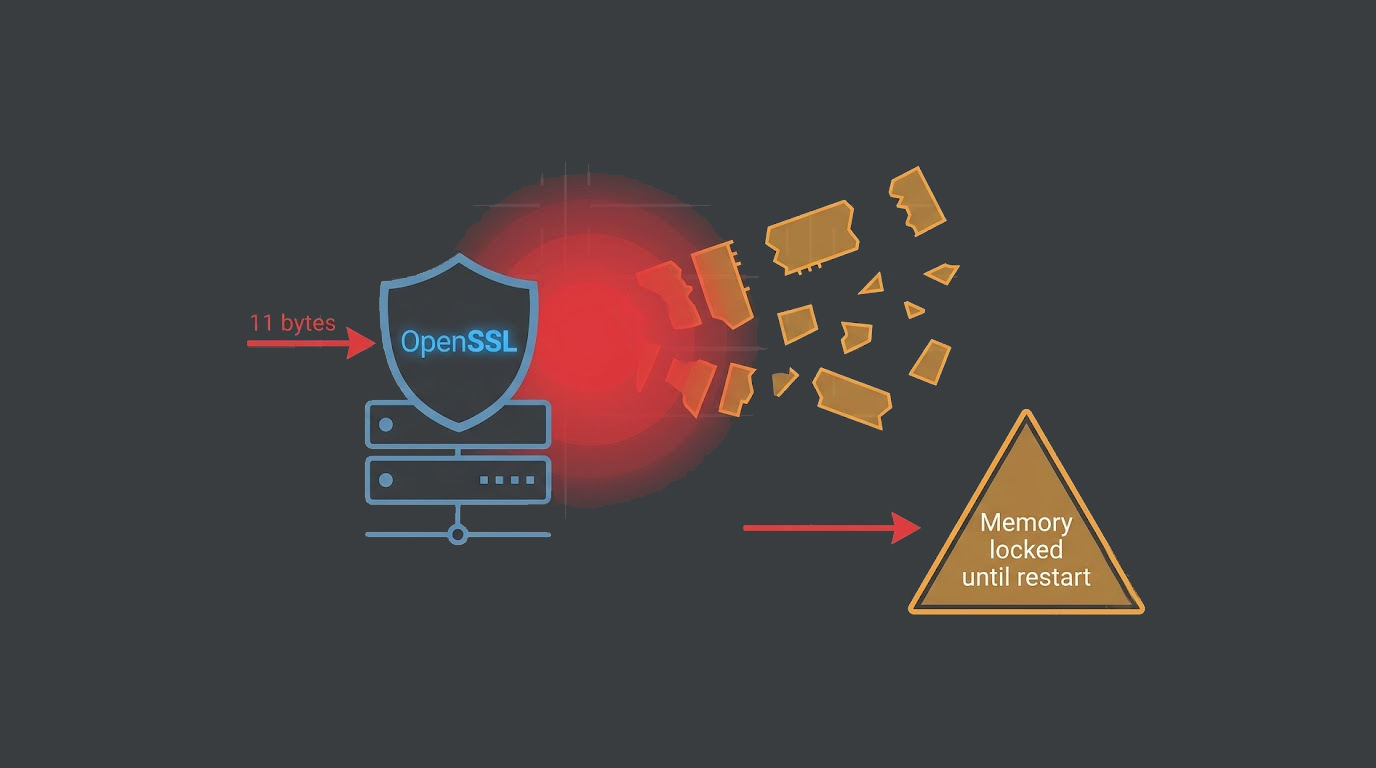
Eleven bytes. That's all it takes to make an unpatched OpenSSL server set aside up to 131 KB of memory for a message that never arrives. On systems running...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067