App Compromise vs Host Compromise: What Changes
Two incidents can look identical in the alert queue and be entirely different animals underneath, because one of them means somebody read data they shouldn...
Found 10 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Two incidents can look identical in the alert queue and be entirely different animals underneath, because one of them means somebody read data they shouldn...
You see the advisory, you see the severity rating, and you think you understand the risk, and then you patch it and move on, and that is where most people...
Your SuiteCRM install might be acting as a proxy for someone else's reconnaissance, because a public proof of concept now shows how an authenticated user c...
You know the drill. Traditional penetration testing takes forever. It costs a fortune. And it happens once or twice a year, if you are lucky. Static scann...
A server-side request forgery vulnerability has been discovered in Apache Gravitino. The flaw affects versions 1.0.0 through 1.2.1 and allows authenticated...
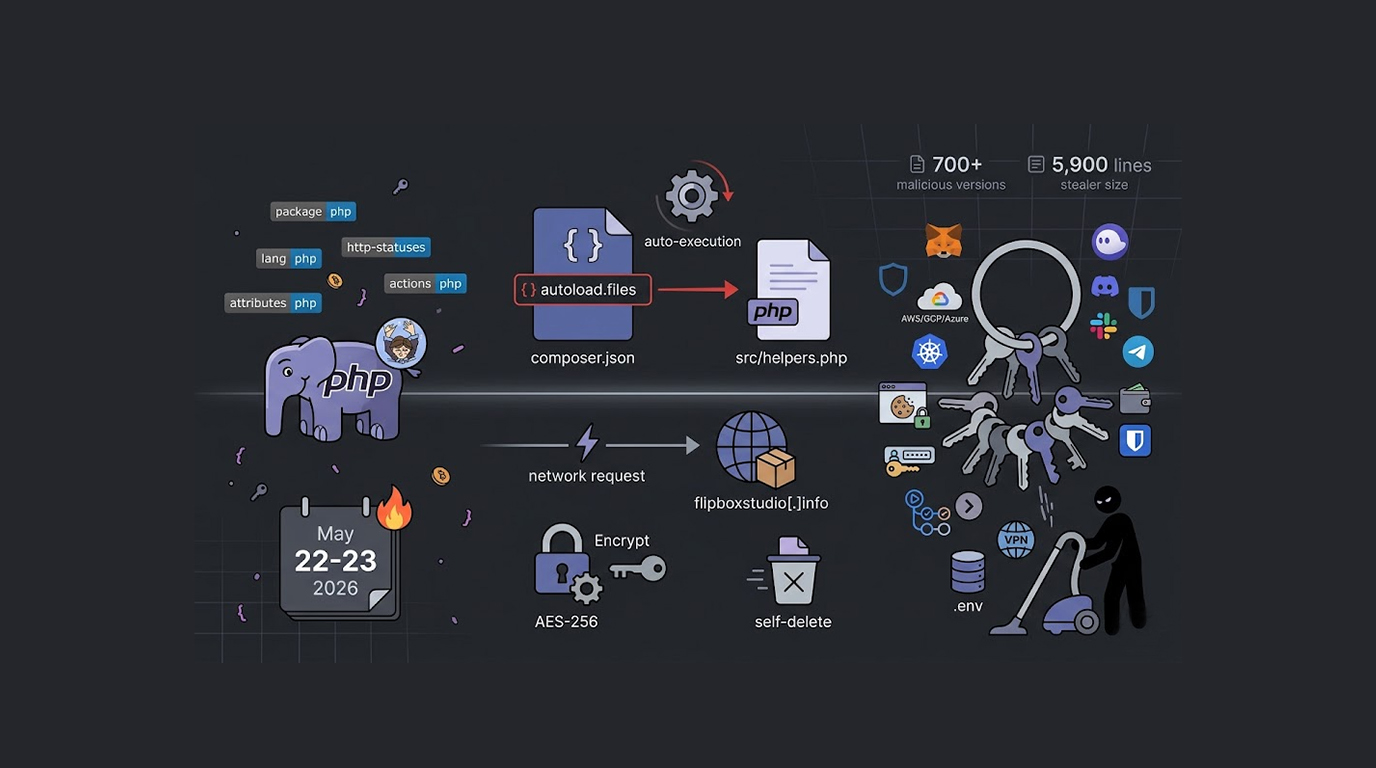
A software supply chain attack has compromised multiple PHP packages belonging to Laravel Lang, and the attackers have embedded a comprehensive credential-...
A critical security flaw in a popular open-source LLM toolkit was published on GitHub. Within half a day, attackers were already using it in the wild. The...
Bug bounty programs in 2026 still pay the highest rewards for vulnerabilities that give an attacker unauthenticated remote code execution (RCE), full serve...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067