Alpine Linux GitLab Attack: CVE-2026-97229 Fallout
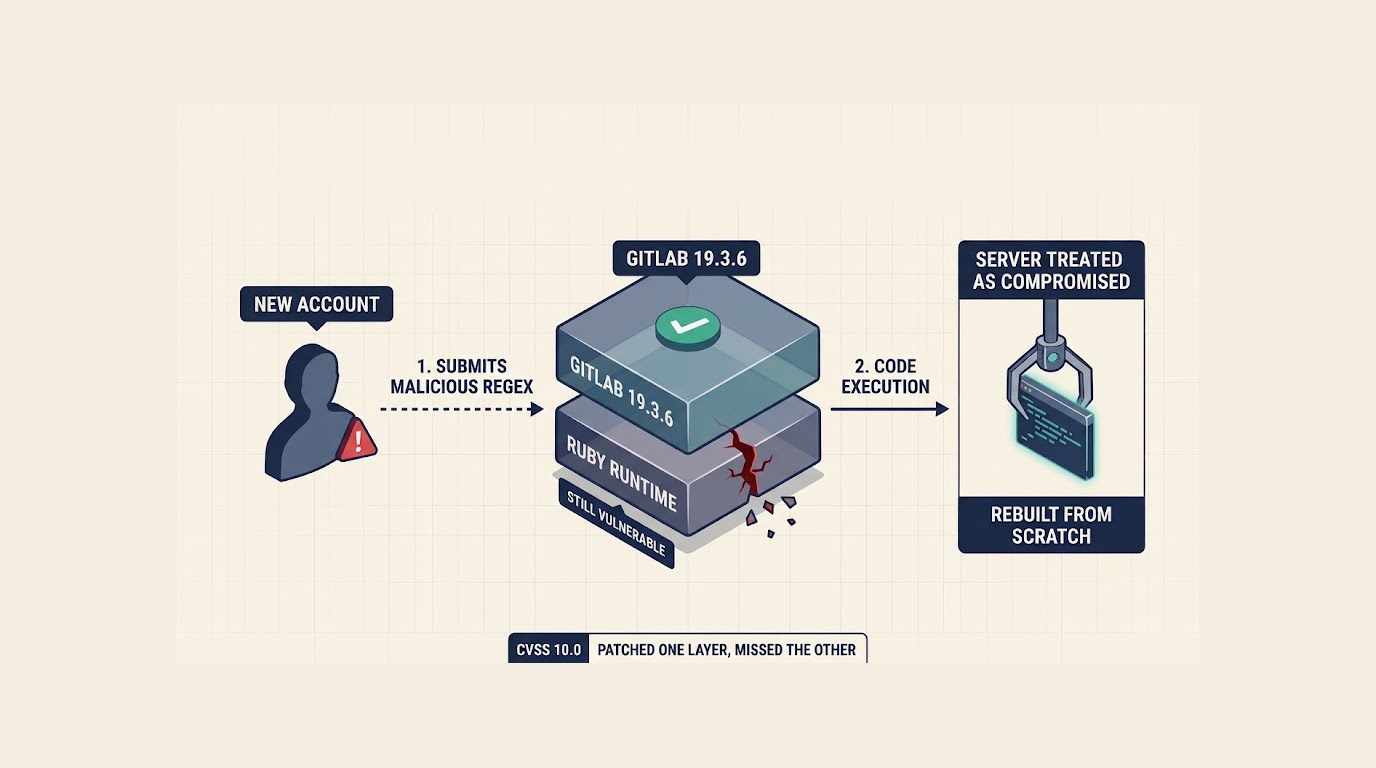
An attacker tried to exploit a critical GitLab vulnerability on the Alpine Linux project's own GitLab server just one week after GitLab released a fix, bec...
Found 97 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
An attacker tried to exploit a critical GitLab vulnerability on the Alpine Linux project's own GitLab server just one week after GitLab released a fix, bec...
Your WordPress site might have a new administrator you never created, because unknown attackers breached TeamUpdraft's website and walked away with custome...
Your repository might look clean and still be compromised, because the actor behind GhostAction has moved past injecting workflows entirely, and the new Gh...
Most people treat their GitLab email address like a convenience, a handy way to file a bug without opening a browser, and almost nobody treats it like a pa...
Gyazo, the image-sharing service run by Helpfeel, just disclosed a serious security breach. The numbers are big. About 23.62 million user records were expo...
Security researchers just uncovered a major update to one of the nastiest Android malware families out there. ToxicPanda, which has been lurking around sin...
You have just recovered your hacked Instagram account. You changed the password. You enabled two-factor authentication. You are relieved. Three days later...
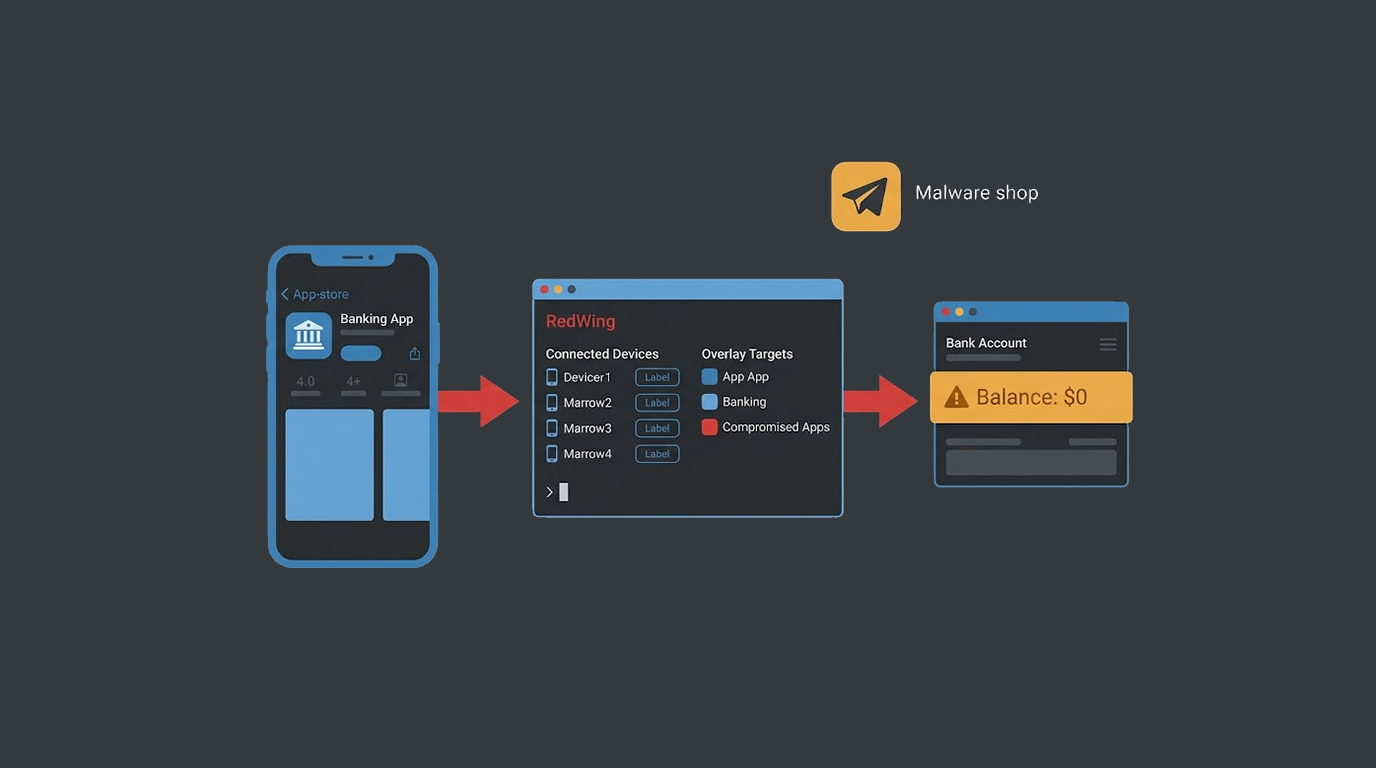
A new bank fraud scheme involving an Android malware-as-a-service operation can be leased via Telegram for carrying out the crime. The malware is named Red...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067