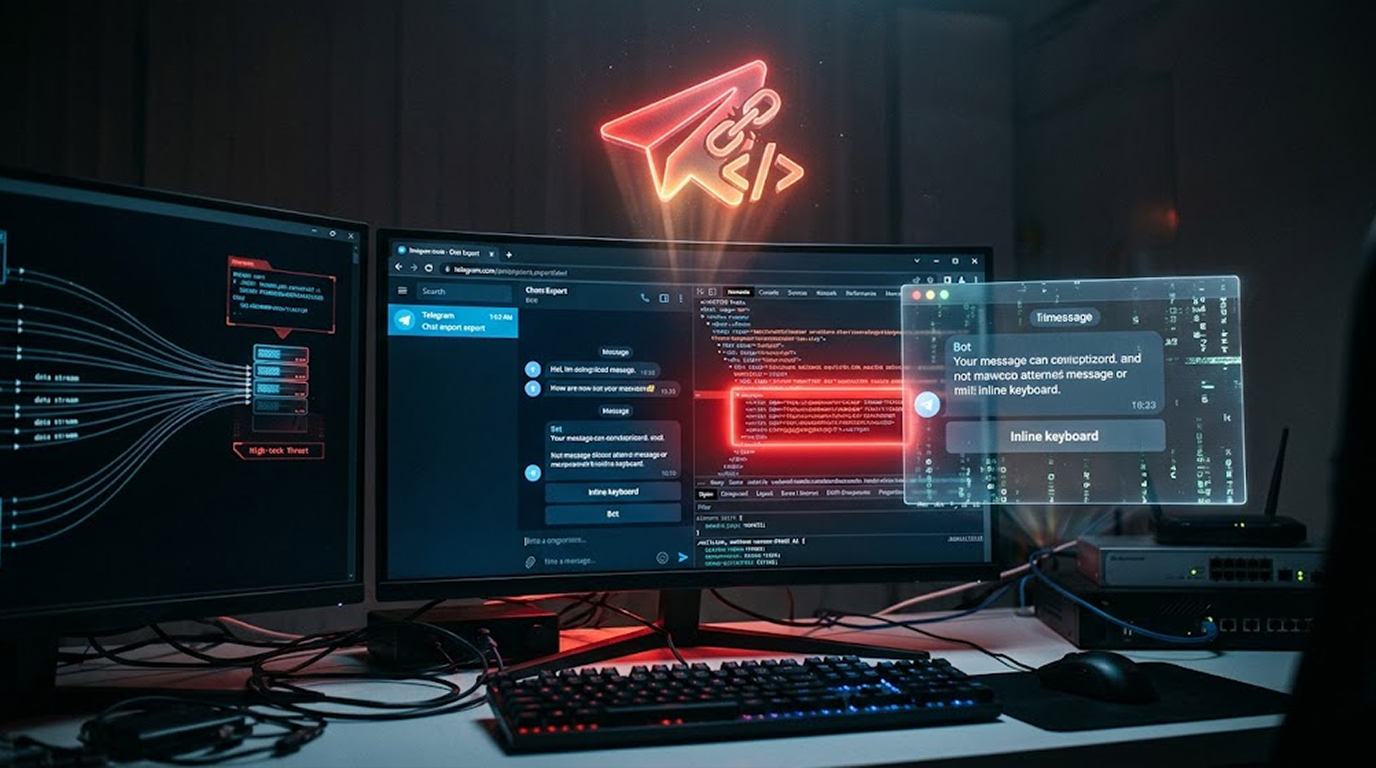
Here's a weird one. A flaw in Telegram Desktop let a bot slip JavaScript into your chat exports. If you saved a chat as an HTML file and opened it in a browser, that script could run. It could steal every message in the file. It could rewrite the page to show a fake login form.
The researchers at ExPatch found it. Denis Rostilov and Aleksander Rostilov. They published their writeup on September 12.
Telegram fixed it back in July. But here's the catch. The fix only applies to new exports. If you made an HTML export before the update, that file can still carry the script.
What You Need to Know
|
What |
Details |
|
Flaw |
Hidden JavaScript in HTML exports |
|
Found by |
ExPatch (Denis and Aleksander Rostilov) |
|
Reported |
June 3, 2026 |
|
Fixed in |
6.9.4 beta (July 3), 7.0.1 (July 14) |
|
Affected |
4.15.1 through 6.9.3 |
|
Risk |
Old exports still dangerous |
What Happened?
Telegram Desktop lets you export chats as HTML files. You can save a single chat or your whole account. The files open in a browser, and they look like a nice readable transcript.
Bots can attach buttons under their messages. Telegram calls them inline keyboards. The bot chooses the text on each button.
The export code took that button text and wrote it straight into the HTML. No escaping. That means if a bot put a script tag in the button text, it would run when you opened the file.
The researchers tested this. They padded the button text with invisible characters so it looked empty in Telegram Desktop. But the script was still there in the export.
And here's the sneaky part. The bot doesn't have to be in the chat. If you forward a message that only has web link buttons, those buttons stay. So any member who forwards that message into a group carries the script with it. The message sits in the history. Months later, someone exports the chat. The script runs.
What Can the Script Do?
When you open the export file in a browser, the script runs automatically. No extra click needed.
It can read every message in that file. Sender names. Timestamps. The chat name and type. Member count. Even the local file path. Then it sends all of that to a server the attacker controls.
It can also rewrite the page. In the researchers' demo, it replaced the whole export with a fake Telegram verification form. That could trick someone into entering their credentials.
It can change dates, senders, or message text. So if you're using an export as a record, it might not be accurate anymore.
One limitation: Telegram splits exports into files of 1,000 messages each. So one file only exposes its own contents. Not the whole chat. Not your whole account.
Who's Affected?
The flaw was in Telegram Desktop versions 4.15.1 (March 2024) through 6.9.3. That's about two years and four months of releases.
The fix landed in 6.9.4 beta on July 3, 2026, and 7.0.1 stable on July 14, 2026. The fix was a single commit by developer John Preston. It added the missing escaping.
So if you're on 7.0.1 or later, you're safe for new exports. But old exports? They still have the problem.
What Should You Do?
1. Update Telegram Desktop.
Get to 7.0.1 or later. If you're on the beta channel, 6.9.4 or later works.
2. Re-export any old HTML exports.
If you made an HTML export before the fix, export it again with the updated app. Or open the old file only with JavaScript disabled.
3. Treat old exports as untrusted.
Especially if they came from a big group where you can't check every message. Don't open them in a browser with JavaScript on. Don't trust what they show.
4. Don't make new HTML exports until you update.
There's no reason to. Only exports from the old code have the flaw.
5. Check your version.
If you're not sure, open Telegram Desktop and check the About screen.
The Missing Advisory
Telegram fixed the bug. But they didn't tell anyone.
The release notes for 6.9.4 and 7.0.1 don't mention it. The changelog doesn't mention it. Telegram's July 14 announcement doesn't mention it. The GitHub repo has no security advisories.
There's also no CVE. No entry in the National Vulnerability Database. No score from Telegram. The researchers rated it 8.2 on the CVSS 3.1 scale. But that's their own number.
The researchers reported the flaw on June 3. Telegram confirmed it on July 1 and offered a $500 bug bounty. The researchers declined and asked for it to go to charity. They asked for a coordinated publication date. They offered to stay quiet until the patch shipped.
Telegram's response, in an email they published, said: "We also have considered the possibility of a public disclosure, but we cannot approve it as disclosing even the already addressed issues could put more Telegram users at risk in the future."
The researchers read that as a refusal to allow publication even after a fix. They say no NDA covered their report. They published on September 12, after the fix was out.
Telegram's bug bounty rules say vulnerabilities "disclosed to the public or to third parties before they are addressed" aren't eligible for a bounty. The page says nothing about publication after a fix.
The Bottom Line
A Telegram Desktop flaw let bots plant hidden JavaScript in HTML exports. The script could steal messages or rewrite the page. Telegram fixed it in July. But old exports are still dangerous. Update to 7.0.1. Re-export old chats. Treat old HTML files as untrusted.
Quick Reference:
|
Key Point |
Detail |
|
Flaw |
Hidden JavaScript in HTML exports |
|
Affected |
4.15.1 through 6.9.3 |
|
Fixed |
6.9.4 beta, 7.0.1 stable |
|
Risk |
Old exports still carry script |
|
Fix |
Update, re-export, treat old files as untrusted |
What to Do:
- Update to 7.0.1 or later
- Re-export old HTML exports
- Open old files with JavaScript disabled
- Treat old exports as untrusted
- Don't make new HTML exports until updated
FAQ Section
What is the Telegram Desktop HTML export flaw?
A bug that let bots put hidden JavaScript into chat exports. The script ran when the HTML file was opened in a browser.
How does the script get into the export?
Bots can set the text on inline keyboard buttons. The export code didn't escape that text, so a script tag could be written directly into the HTML.
Do I need to be in the same chat as the bot?
No. If a message with web link buttons is forwarded, the buttons stay. So forwarding a bot's message into a group carries the script.
What can the script do?
It can read every message in the export file and send it to an attacker. It can also rewrite the page to show a fake login form.
Is there a fix?
Yes. Telegram fixed it in 6.9.4 beta and 7.0.1 stable. But old exports made before the fix still carry the script.
What should I do?
Update to 7.0.1. Re-export old HTML exports. Open old files with JavaScript disabled. Treat old exports as untrusted.