A new flaw in the Linux kernel's KVM virtualization code for ARM64 processors can leave a freed piece of host memory exposed to a guest virtual machine, but only on hosts with nested virtualization enabled, and the bug is tracked as CVE-2026-89775.
The flaw allows a guest to read and write host kernel memory, and the researcher who found it says it can be used to escape the guest and run code on the host machine, which is about as serious as a virtualization bug gets.
The affected code is part of the mainline Linux kernel for ARM64, and it is fixed in Linux 6.18.51, 7.2.5, and 7.3-rc1, so if you run ARM64 KVM hosts, you need to check your version and patch, though the good news is that nested virtualization is off by default, and turning it on requires specific hardware and an experimental boot-time mode.
Let me break down what happened.
Quick Summary
|
What |
Details |
|
Flaw |
CVE-2026-89775 |
|
Component |
KVM virtualization for ARM64 |
|
Impact |
Guest can read/write host kernel memory, escape to host |
|
Requirement |
Nested virtualization enabled |
|
Fixed In |
Linux 6.18.51, 7.2.5, 7.3-rc1 |
|
Reporter |
Hyunwoo Kim |
|
Disclosure |
September 16, 2026 |
What Is Nested Virtualization?
Nested virtualization allows a guest to run its own hypervisor, which enables it to host virtual machines, so on ARM64, it is off by default, and it is an experimental boot-time mode that needs Armv8.4 hardware with a feature called FEAT_NV2, which means a plain ARM64 KVM host that never turns it on is outside the reported attack path.
So the scope is limited, but for those who do enable it, the flaw is serious.
How the Flaw Works
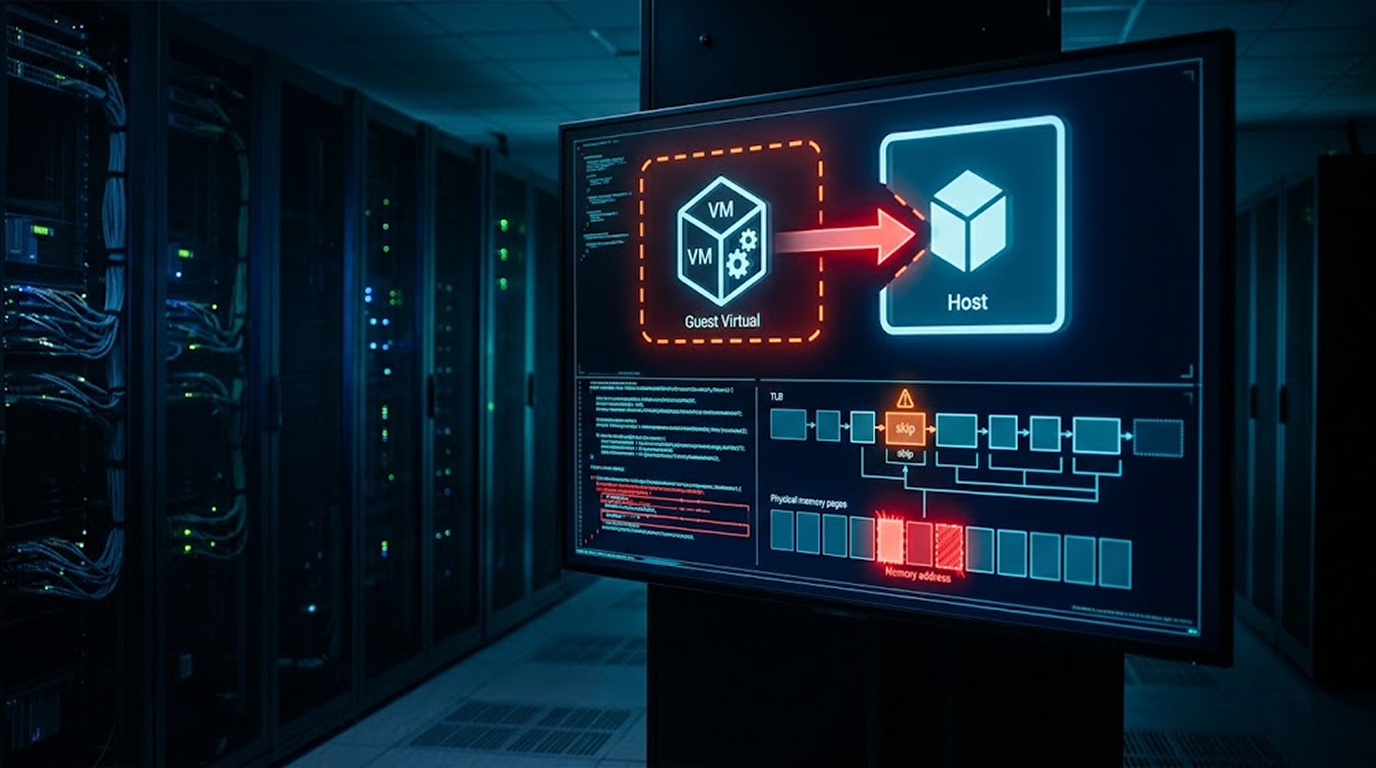
The flaw sits in the part of KVM that handles nested virtualization on ARM64, and when a guest arranges its memory in a certain way, a size calculation comes out as zero, and a step that should clear stale entries from the processor's address cache, a TLB invalidation, is skipped, which leaves a page of host memory that has been freed still mapped and writable.
The guest can then read and write it 64 bits at a time, with no hardware trap to hand control back to the host, and Hyunwoo Kim, the security researcher who reported the flaw and disclosed it on September 16, says a guest can use this to escape to the host, breaking out of its own virtual machine to run code on the underlying machine.
No exploit code has been published, and there is no sign the flaw has been used in an attack.
A Second Path: Local Privilege Escalation
There is a second way to abuse the flaw, because on systems where any user can open /dev/kvm, which is the device a program uses to create a virtual machine, a local user could build a guest and use the same bug to gain root, Kim says.
He points to Red Hat Enterprise Linux, where that device is open to all users by default, and Red Hat lists its version 10 kernel as affected and versions 6 through 9 as not affected, though this path still needs the host to have nested virtualization enabled, so it is not a universal privilege escalation.
Which Kernels Are Fixed
Upstream, the flaw is fixed in Linux 6.18.51, 7.2.5, and 7.3-rc1, and distributions are shipping the fix on their own schedules, and status differs by release.
|
Kernel or Distribution |
Status as of September 22 |
|
Mainline Linux |
Fixed in 6.18.51, 7.2.5, and 7.3-rc1 |
|
Red Hat Enterprise Linux |
Version 10 kernel affected; versions 6 through 9 not affected |
|
Ubuntu |
26.04, including its AWS, Azure, and GCP kernels, vulnerable; 24.04 LTS general kernel not affected, though its newer hardware-enablement kernels (6.17, 7.0) are vulnerable |
|
Amazon Linux |
AL2023 kernel6.18 package: fix pending; other Amazon Linux kernels not affected |
|
Debian |
bookworm and trixie not affected (code not present); sid fixed in 7.2.6-1; forky vulnerable |
For hosts that cannot yet be patched, Red Hat says no mitigation meets its criteria for a workaround, so patching is the only real fix, and the one certain thing is scope, because the attack only targets hosts with nested virtualization enabled, which is not the default on ARM64.
How Serious Is It?
Vendors score the flaw from 7.8 to 9.3 out of 10, and they agree the impact is high and the attack is local, meaning it cannot be launched over a network, and the spread reflects how difficult each vendor thinks the flaw is to exploit, and Ubuntu, which shows the 9.3 figure, sets its own priority to medium.
As of September 22, the flaw was not in the U.S. CISA catalog of exploited vulnerabilities, and its predicted exploitation score was below 1%, so while it is serious, it is not yet being used in the wild.
The disclosure raises the question of whether cloud tenants could use the flaw to break into a provider's machines, but on the largest providers, the configuration it needs is not on offer, because Amazon Web Services lists only Intel-based instances for nested virtualization, and Google Cloud excludes its ARM virtual machines from it, which is not a clean bill of health for those platforms, but the specific path this flaw takes is not exposed in their standard ARM offerings.
The Researcher's Track Record
CVE-2026-89775 is the fourth KVM guest-to-host escape Kim has disclosed this year, and two were in the x86 version of KVM, Januscape in July and Zapscape in August, but the one it most resembles is ITScape, an ARM64 KVM escape he published in June, which he called the first such escape shown publicly on ARM64.
So this is a researcher who has been systematically finding and reporting these bugs, which is good for defenders, because it means the flaws are getting fixed, but it also means there may be more out there.
What You Should Do
- Check your ARM64 KVM hosts for nested virtualization, and if you don't need it, leave it off, because that alone removes the attack path.
- If you do need it, patch to Linux 6.18.51, 7.2.5, or 7.3-rc1, or apply your distribution's fix.
- On Red Hat Enterprise Linux 10, check whether /dev/kvm is open to all users, and restrict it if possible.
- For Ubuntu 26.04, including its cloud kernels, apply the fix as soon as it is available.
- For Amazon Linux AL2023, watch for the kernel6.18 package update.
- For Debian, bookworm and trixie are not affected, but forky is vulnerable, so patch if you run forky.
The Bottom Line
CVE-2026-89775 is a serious ARM64 KVM flaw that lets a guest escape to the host, but it only works if nested virtualization is enabled, which is not the default, so the practical risk is limited to those who turn it on, and the fix is available in Linux 6.18.51, 7.2.5, and 7.3-rc1, so if you run ARM64 KVM hosts with nested virtualization, patch now, and if you don't need nested virtualization, leave it off, because that is the simplest mitigation.
Quick Reference
|
Key Point |
Detail |
|
Flaw |
CVE-2026-89775 |
|
Impact |
Guest-to-host escape |
|
Requirement |
Nested virtualization enabled |
|
Fixed In |
Linux 6.18.51, 7.2.5, 7.3-rc1 |
|
Reporter |
Hyunwoo Kim |
|
CISA KEV |
Not listed as of September 22 |
|
Exploitation |
No known attacks |
What to Do
- Leave nested virtualization off if you don't need it
- Patch to the fixed versions
- Restrict /dev/kvm on Red Hat Enterprise Linux 10
- Apply fixes on Ubuntu 26.04 and cloud kernels
- Watch for Amazon Linux AL2023 kernel6.18 update
- Patch Debian forky
FAQ Section
What is CVE-2026-89775?
It is a flaw in the Linux kernel's KVM virtualization code for ARM64 processors, where a guest can read and write host kernel memory and potentially escape to the host.
Does this affect all ARM64 KVM hosts?
No, it only affects hosts with nested virtualization enabled, which is off by default on ARM64 and requires Armv8.4 hardware with FEAT_NV2.
How does the flaw work?
When a guest arranges its memory in a certain way, a size calculation becomes zero, a TLB invalidation is skipped, and a freed host memory page stays mapped and writable, so the guest can read and write it.
Can a local user gain root with this?
On systems where any user can open /dev/kvm, a local user could build a guest and use the bug to gain root, and Red Hat Enterprise Linux 10 is noted as having that device open by default.
Which kernels are fixed?
Upstream, the flaw is fixed in Linux 6.18.51, 7.2.5, and 7.3-rc1, and distributions are shipping fixes on their own schedules.
Is there a workaround?
Red Hat says no mitigation meets its criteria for a workaround, so the only certain fix is patching, but leaving nested virtualization off removes the attack path.