cPanel EmailTrack
Here's a nightmare scenario for any web hosting provider. cPanel just patched a vulnerability that lets a single hosting account take over an entire server. One customer account, full root access to the machine.
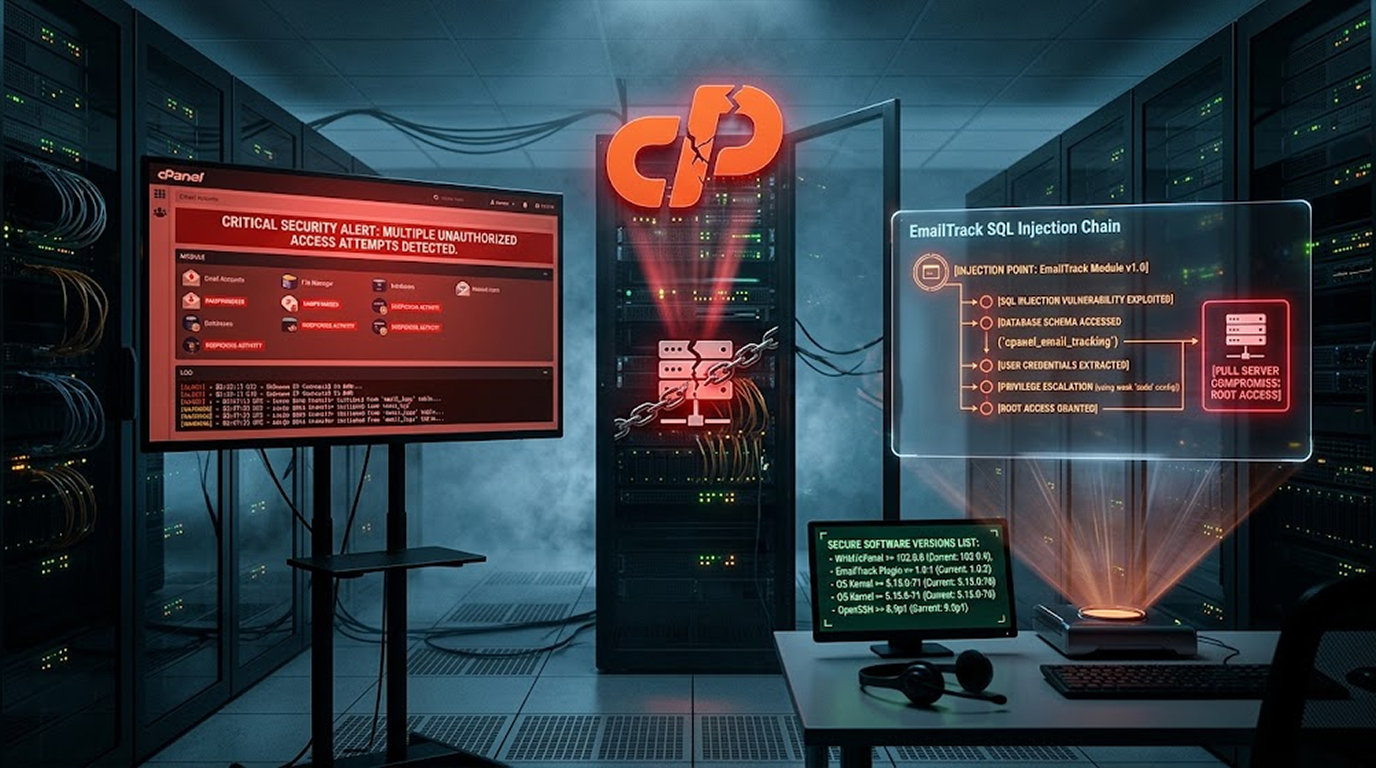
The flaw is tracked as CVE-2026-67401. It's an SQL injection issue in cPanel's EmailTrack module. An authenticated account holder with mail-related privileges can create files anywhere on the server. From there, they can run code as the root user.
If you run a cPanel server, you need to update right now.
Quick Summary
|
What |
Details |
|
Vulnerability |
CVE-2026-67401 |
|
Component |
EmailTrack (SQL injection) |
|
Impact |
Arbitrary file creation → root code execution |
|
Requirement |
Authenticated account with mail privileges |
|
Fixed Versions |
11.110.0.143, 11.134.0.55, 11.136.0.39, 11.138.0.4 |
|
Status |
Patch available, no known exploitation |
The Problem
cPanel is web hosting control panel software. A customer manages one hosting account via cPanel. The provider manages the entire machine via WHM as the root user.
Normally, one customer account shouldn't be able to touch anything outside their own slice of the server. This flaw breaks that boundary.
Attack Chain:
- Attacker logs in to their cPanel account
- Requires privilege for mails (most of the hosting accounts have it)
- Takes advantage of SQL injection in EmailTrack
- Allows creating files on the server arbitrarily
- Then they run root-level code
The Missing Details:
cPanel's advisory is surprisingly light on technical specifics. It doesn't say:
- Which specific cPanel feature or privilege is required
- How the SQL injection turns into file creation
- How file creation turns into root access
- How to check if you've been compromised
The advisory also carries no severity score. That's unusual for a vulnerability that lets an authenticated user escalate to root.
The Fixed Versions
cPanel has patched the flaw in these builds:
|
Release Line |
Fixed Build |
|
11.110 |
11.110.0.143 |
|
11.134 |
11.134.0.55 |
|
11.136 |
11.136.0.39 |
|
11.138 |
11.138.0.4 |
|
WP Squared |
11.138.1.9 |
How to Update:
- Via WHM: Home → cPanel → Upgrade to Latest Version
- Via Command Line: /usr/local/cpanel/scripts/upcp --force
What About 11.118 and 11.126?
cPanel patched these lines in July and hasn't mentioned them since. The advisory doesn't say whether they're still supported or if they're affected.
The Bigger Picture
This isn't an isolated incident. cPanel has been dealing with a series of critical flaws lately.
Recent cPanel Vulnerabilities:
- July 2024: A database flaw let accounts with database access run commands with full administrative privileges
- August 2024: A domain parking flaw ended the same way, code execution as root
- September 2024: This EmailTrack flaw
The Pattern:
Multiple vulnerabilities start from an ordinary hosting account and end with root access. That's a serious problem for hosting providers.
Public Exploits Exist:
Repositories that present themselves as working exploits for the July and August flaws were online when The Hacker News checked. That means attackers are actively weaponizing these vulnerabilities.
Why This Matters
What an Attacker Can Do with Root Access:
- Read every hosting account on the machine
- Change files and databases
- Create hidden accounts
- Install malware
- Steal credentials
- Move into customer networks
Who's Affected:
Every supported version of cPanel and WHM is vulnerable to this flaw.
April 2024 Comparison:
In April, attackers exploited a different cPanel flaw. Taking over the panel isn't the same as breaking into one customer's website. WHM gives an attacker root administrative access to the entire server.
What You Should Do
- Update Immediately. There's no workaround. Update to the fixed builds listed above.
- Check for Compromise Indicators. Information could not be found about how to detect compromise indicators in cPanel.
- Unauthorized Access Signs. It was possible to detect unauthorized access through any changes in files, any new accounts created, or any activities conducted by the cPanel user.
- Check Permissions of Users. Check whether you have too many cPanel users who have permissions related to mail.
- Stay Informed. cPanel's recent CVEs are assigned through HackerOne. Severity scores appear in the CVE record rather than the advisory.
The Bottom Line
cPanel's EmailTrack flaw lets a single hosting account execute code as root. The vulnerability affects every supported version. No workarounds are available, you need to patch.
What You Need to Know:
|
Key Point |
Detail |
|
Vulnerability |
CVE-2026-67401 |
|
Component |
EmailTrack (SQL injection) |
|
Impact |
Root code execution |
|
Requirement |
Authenticated account with mail privileges |
|
Fixed Versions |
11.110.0.143, 11.134.0.55, 11.136.0.39, 11.138.0.4 |
What You Need to Do:
- Update to the fixed builds immediately
- Review logs for suspicious activity
- Monitor for unauthorized access
- Review user privileges
FAQ Section
What is the cPanel EmailTrack flaw?
A vulnerability that lets an authenticated hosting account with mail-related privileges create arbitrary files on the server and execute code as root. The flaw is an SQL injection in cPanel's EmailTrack module.
Which versions are affected?
Every supported version of cPanel and WHM is affected. The fixed builds are 11.110.0.143, 11.134.0.55, 11.136.0.39, and 11.138.0.4.
Is there a workaround?
No. cPanel didn't provide a workaround. You need to update immediately.
Has the vulnerability been exploited?
cPanel's advisory doesn't mention exploitation. No public exploit code was found as of September 9. But previous cPanel flaws have been actively exploited.
What should I do?
Update immediately. Review your server logs for suspicious activity. Monitor for unauthorized access.