3BB
An attacker got inside 3BB, one of Thailand's biggest broadband providers. They didn't just visit. They set up shop, moved around, and went after customer login data. And they did it using a tool that IT teams trust every day.
Hunt.io found the intrusion. They caught it by looking at a server the attacker had left open on the internet. That server held the attacker's own tools. It also held a list of machines already under their control.
The researchers captured it on June 3, 2026. The operation was still live.
Here's what we know.
Quick Summary
|
What |
Details |
|
Target |
3BB (Thailand broadband provider) |
|
Tool abused |
MeshCentral (remote management) |
|
Goal |
RADIUS subscriber databases |
|
Found by |
|
|
Captured |
June 3, 2026 |
|
Initial access |
Not confirmed |
What Happened?
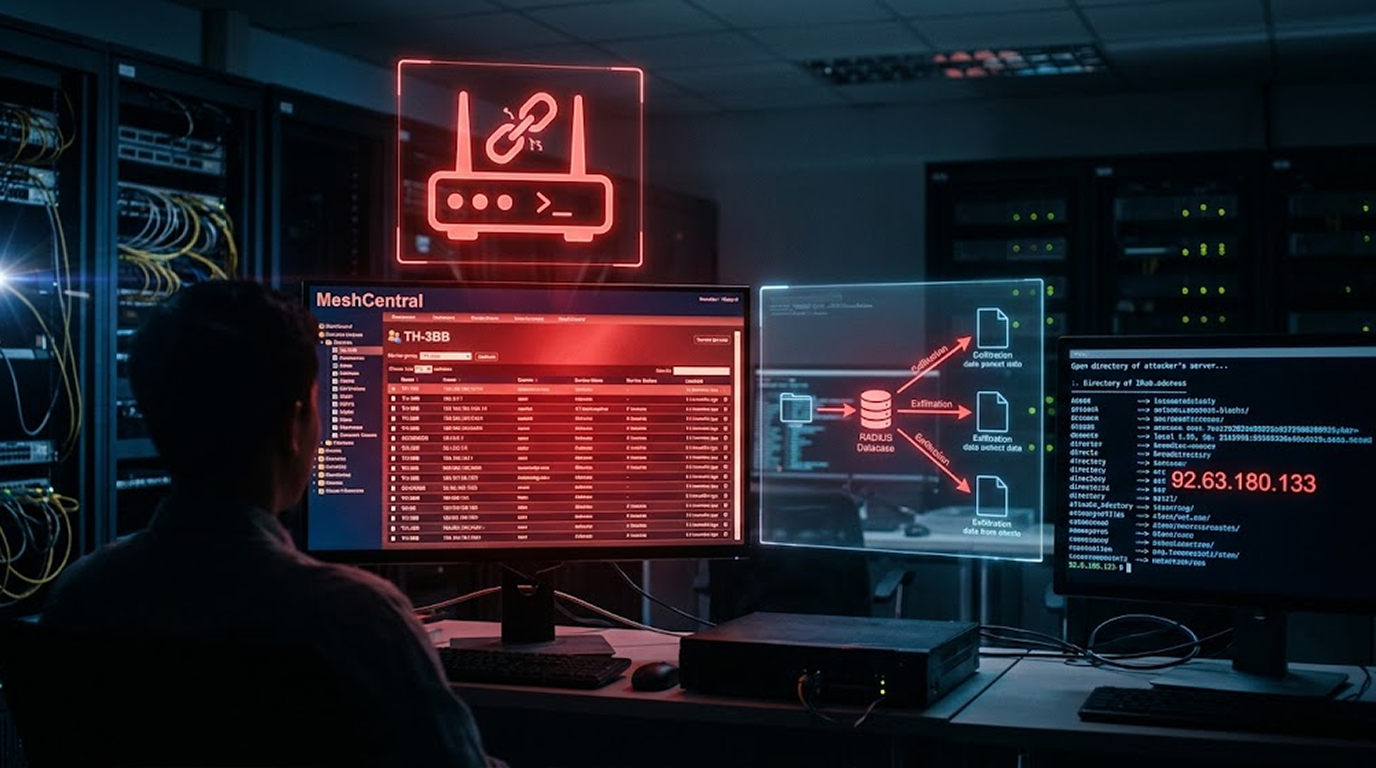
The attacker was operating inside 3BB's network. They had remote control of internal machines. To keep that access, they installed MeshCentral.
MeshCentral is a free tool. IT teams use it to manage computers remotely. That's what makes it useful for attackers. It's trusted. Its traffic looks like normal admin work.
The recovered settings show it was set up as a hidden backdoor. The agents reported to a control server at www.ayuthayatech[.]com. The device group was named TH-3BB.
The Exposed Server
Hunt.io found the attacker's server open on the internet. That's how they got the details.
The server held the attacker's toolkit. It held a list of machines under their control. One file showed the attacker getting root on an internal server. Several machines on the list were connected with root privileges when the list was made.
There was also a cleanup script. It was written to erase logs and delete the attacker's other tools. But it deliberately left the MeshCentral agent in place. That way, the access would survive.
What the Attacker Did Inside
Once inside, the attacker tried to widen their reach.
They sprayed passwords against more than 55 internal computers over SSH. They probed 3BB's internal sales portal at agent.3bb.co[.]th. They searched compromised machines for stored passwords, database logins, and SSH keys.
Other scripts could plant web shells. Those are hidden pages that run an attacker's commands. They could also add SSH keys as backup ways back in.
The Real Goal: RADIUS Databases
Hunt.io said the attacker's main goal was 3BB's subscriber data.
Scripts on the server were built to copy out the company's RADIUS databases. Those are the systems that store broadband customers' login credentials. The evidence shows the databases were targeted. It does not show that any data was actually taken.
The FortiGate Question
How did the attacker get in? That's not established.
The server held a full toolkit aimed at a 3BB FortiGate SSL-VPN gateway. The target was mail.3bb.co[.]th. The toolkit included a complete exploit for CVE-2024-21762.
That's a serious Fortinet flaw from 2024. It lets an attacker run code on the device without logging in. The targeted gateway was running a firmware version affected by the flaw.
But here's the catch. Nothing Hunt.io recovered shows the exploit actually worked. It doesn't show that's how the attacker got in.
The FortiGate tooling was the most developed part of the kit. But it points to capability and intent. Not a confirmed break-in through that device.
The Jasmine Connection
The same server pointed to a second target. It held a valid VPN certificate from 3BB's own systems. It also had active login sessions for services on the Jasmine network.
Jasmine is a company 3BB was once part of. They still share infrastructure.
Hunt.io said this suggests the attacker was working against both. But it did not confirm that Jasmine itself was breached.
What Defenders Should Do
The recovered toolkit gives a clear list of steps for anyone running similar edge devices and authentication systems.
1. Patch FortiGate SSL-VPN.
Check your appliances against CVE-2024-21762. If you can't patch right away, turn off SSL-VPN. Fortinet says turning off web mode alone is not enough.
2. Check for MeshCentral agents.
Look for agents you didn't install. Look for connections to management servers you don't recognize.
3. Rotate credentials.
SSH key, database password, RADIUS password, certificate on VPN, and application secret should all be rotated. Patching does not remove an agent that's already installed. It does not reset a password that's already been copied.
4. Hunt for hidden ways back in.
Look for unexpected SUID files. Look for web shells. Check for changed SSH keys. Check for newly added remote-management software.
5. Preserve logs and evidence.
Do this prior to cleaning. The attacker’s own script will do just that for them.
Indicators of Compromise
- IP address: 92.63.180[.]133 - attacker's server. Port 8888 held the open directory. Port 9443 received exploit callbacks.
- Domain: www.ayuthayatech[.]com - MeshCentral control server.
- MeshCentral group: TH-3BB
- Persistence paths: /usr/local/bin/.rc (hidden backdoor) and /usr/local/mesh_services/meshagent/
- Targets: mail.3bb.co[.]th (FortiGate SSL-VPN) and agent.3bb.co[.]th (internal portal)
The full list is in Hunt.io's report.
The Bottom Line
An attacker was inside 3BB's network. They used MeshCentral as a hidden backdoor. They went after RADIUS subscriber databases. They may have tried to get in through a FortiGate SSL-VPN flaw, but that's not confirmed. The attacker has since closed the exposed server. Whether they still have access inside 3BB is not known.
Quick Reference:
|
Key Point |
Detail |
|
Target |
3BB |
|
Tool abused |
MeshCentral |
|
Goal |
RADIUS databases |
|
Found by |
|
|
Initial access |
Not confirmed |
|
FortiGate flaw |
CVE-2024-21762 toolkit found |
What to Do:
- Patch FortiGate SSL-VPN
- Check for rogue MeshCentral agents
- Rotate credentials
- Hunt for hidden persistence
- Preserve logs before cleanup
FAQ Section
What is the 3BB MeshCentral breach?
An attacker was operating inside 3BB's network. They used MeshCentral, a legitimate remote-management tool, as a hidden backdoor.
How was the attacker found?
Hunt.io found an exposed server the attacker left on the internet. It held their tools and a list of controlled machines.
What did the attacker go after?
Their primary target was the 3BB RADIUS databases, where the broadband customers' login details are stored. The proof lies in their intention to attack the data, not necessarily stealing it.
Did the attacker get in through FortiGate?
Not confirmed. The server held a full exploit toolkit for CVE-2024-21762, a Fortinet flaw. The targeted gateway was vulnerable. But nothing shows the exploit worked.
What should defenders do?
Patch FortiGate SSL-VPN. Check for MeshCentral agents. Rotate credentials. Hunt for hidden persistence. Preserve logs before cleanup.