Node.js HTTP/2 Flaws: Crash and Memory Leak
Node.js released fixes this week for a cluster of server-side vulnerabilities, and the worst one is not a crash. It is a memory disclosure that can hand an...
Found 9 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Node.js released fixes this week for a cluster of server-side vulnerabilities, and the worst one is not a crash. It is a memory disclosure that can hand an...
Apache released version 2.4.71 yesterday, and the reason is CVE-2026-119618, a critical flaw in the HTTP/2 module that allows a remote attacker to run code...
Anthropic released two models on Monday, and the benchmark that matters most is not the one about coding. Claude Fable 5.2 and Claude Mythos 5.2 both ship...
Anthropic just dropped a 154-page report that should make anyone in security sit up straight. Between December 2025 and August 2026, cybercriminals and sta...
A suspected Russian-speaking cyber actor has been using AI to develop exploits for a pair of PaperCut vulnerabilities. The result? Hundreds of compromised...
A newly discovered vulnerability in the Linux kernel allows any unprivileged user to obtain full root access. The flaw, known as Bad Epoll and tracked as C...
A newly discovered denial-of-service exploit affects major web servers including NGINX, Apache HTTPD, Microsoft IIS, Envoy, and Cloudflare Pingora, and the...
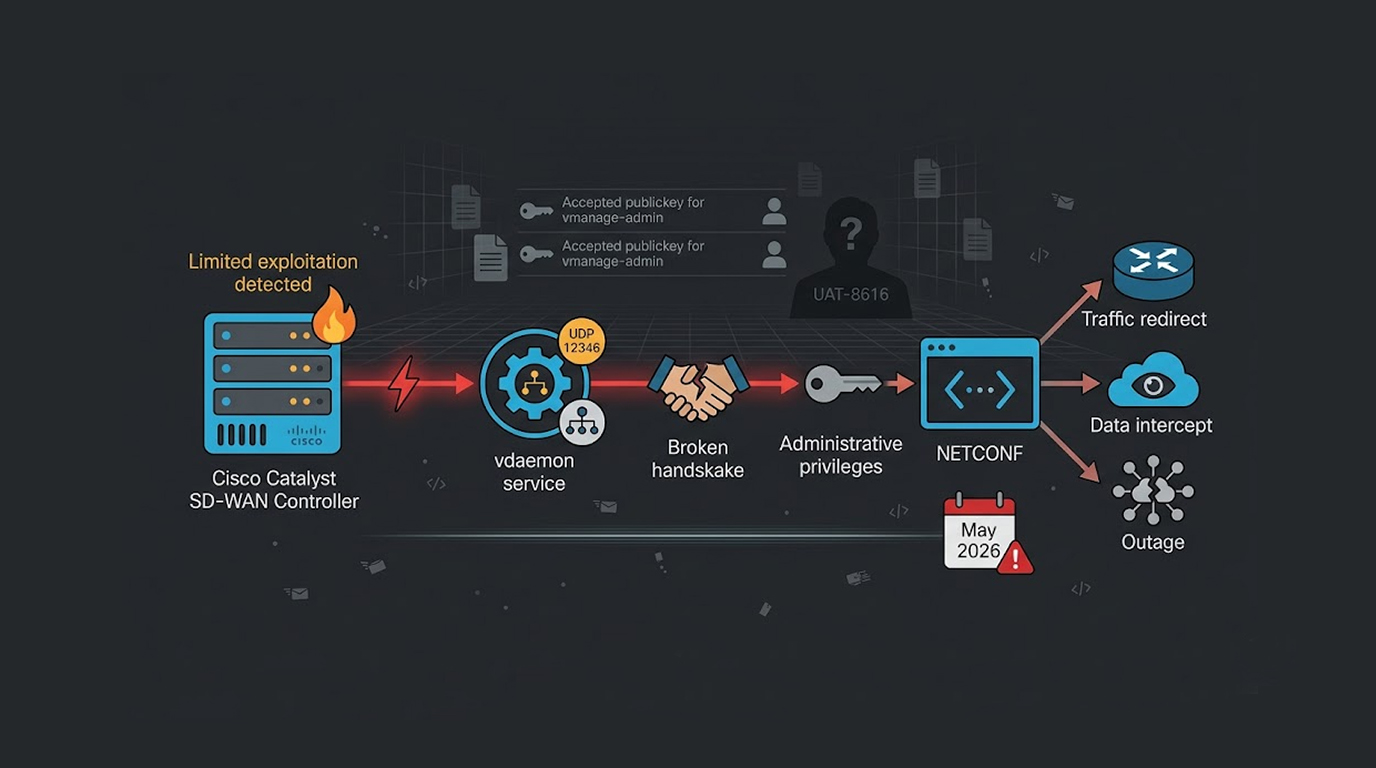
Cisco has released emergency updates for a critical vulnerability in its Catalyst SD-WAN Controller, and the flaw carries a CVSS score of 10.0 which is the...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067