Malware in Coding Tests: The Recruitment Attack
There's a moment in every hiring process where a candidate is asked to prove they can code, and the standard way to do that is to send them a repository, a...
Found 26 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There's a moment in every hiring process where a candidate is asked to prove they can code, and the standard way to do that is to send them a repository, a...
Your npm install might have handed a stranger your browser cookies, your wallet files, and a persistent backdoor, because researchers just documented a fak...
Somewhere right now, a domain is registered that looks almost like yours, an app is sitting in a store using your logo, and a social account is pretending...
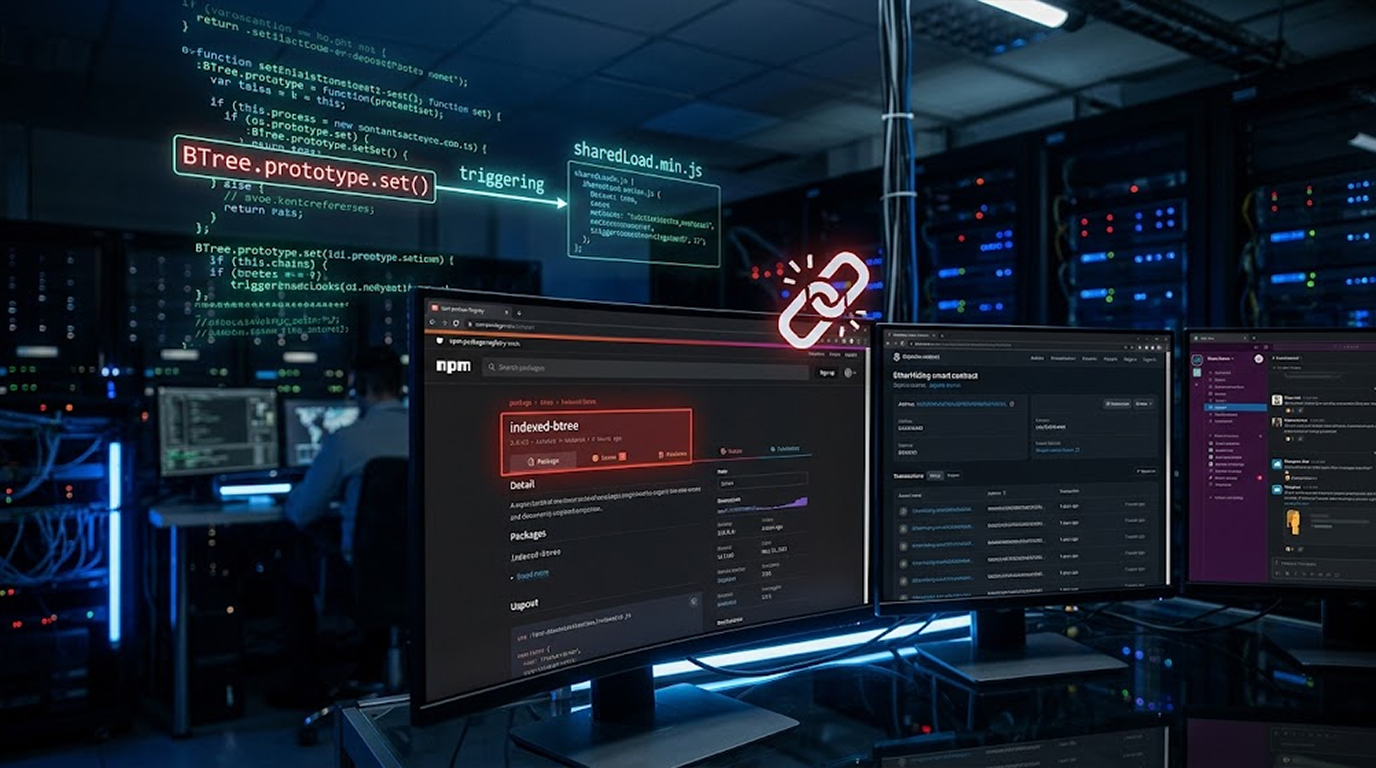
A malicious npm package called indexed-btree has been caught hiding its payload inside application code, rather than using lifecycle scripts, which is a si...
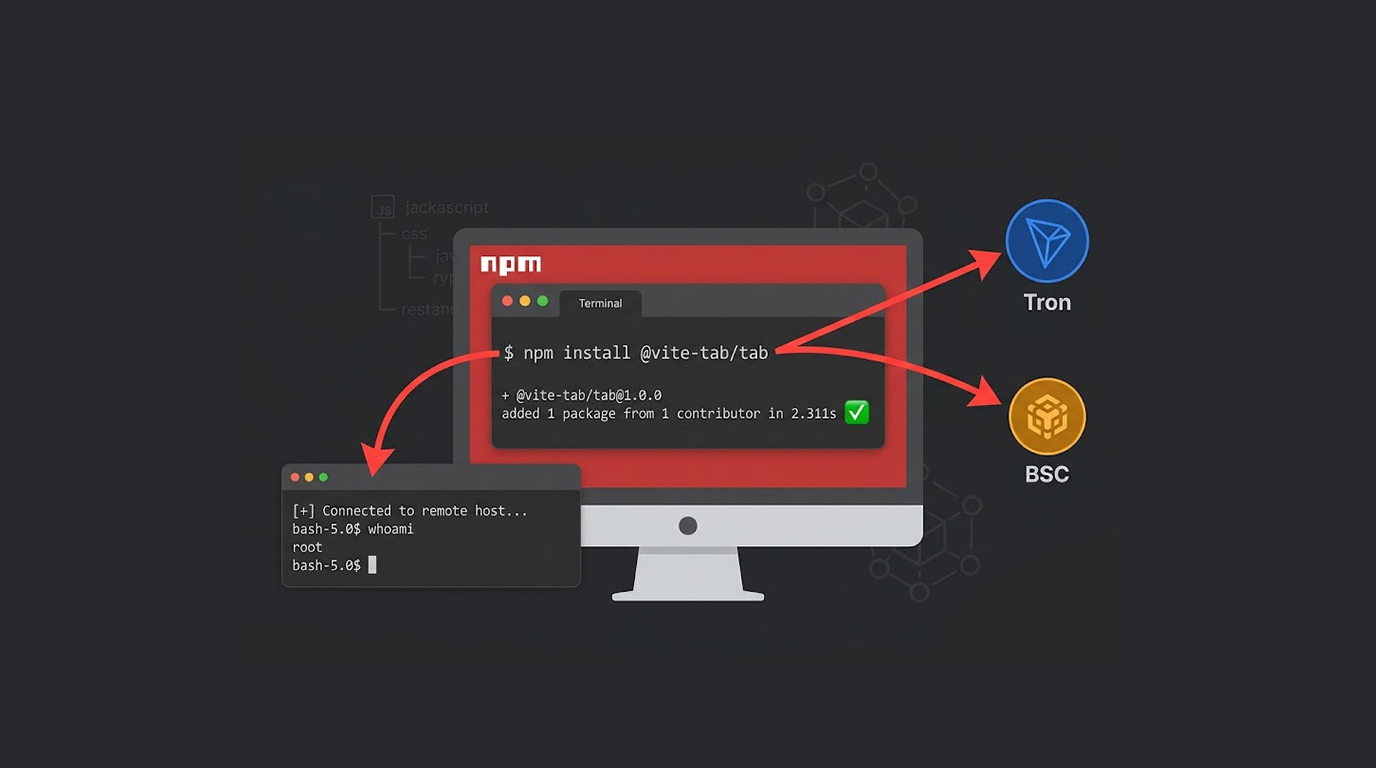
A cluster of seven malicious npm packages is targeting the Vite frontend tooling ecosystem. The campaign, codenamed ViteVenom, marks an expansion of ChainV...
You have heard about AI being used for good. It helps doctors diagnose diseases. It writes code. It answers customer support questions. Now AI is being us...
You have worked for many years developing your personal brand on social media. However, now there is a network of fake accounts that are exploiting your im...
Here's a nightmare scenario for Arch Linux users. You install or update a package from the Arch User Repository, the community-driven collection that makes...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067