App Compromise vs Host Compromise: What Changes
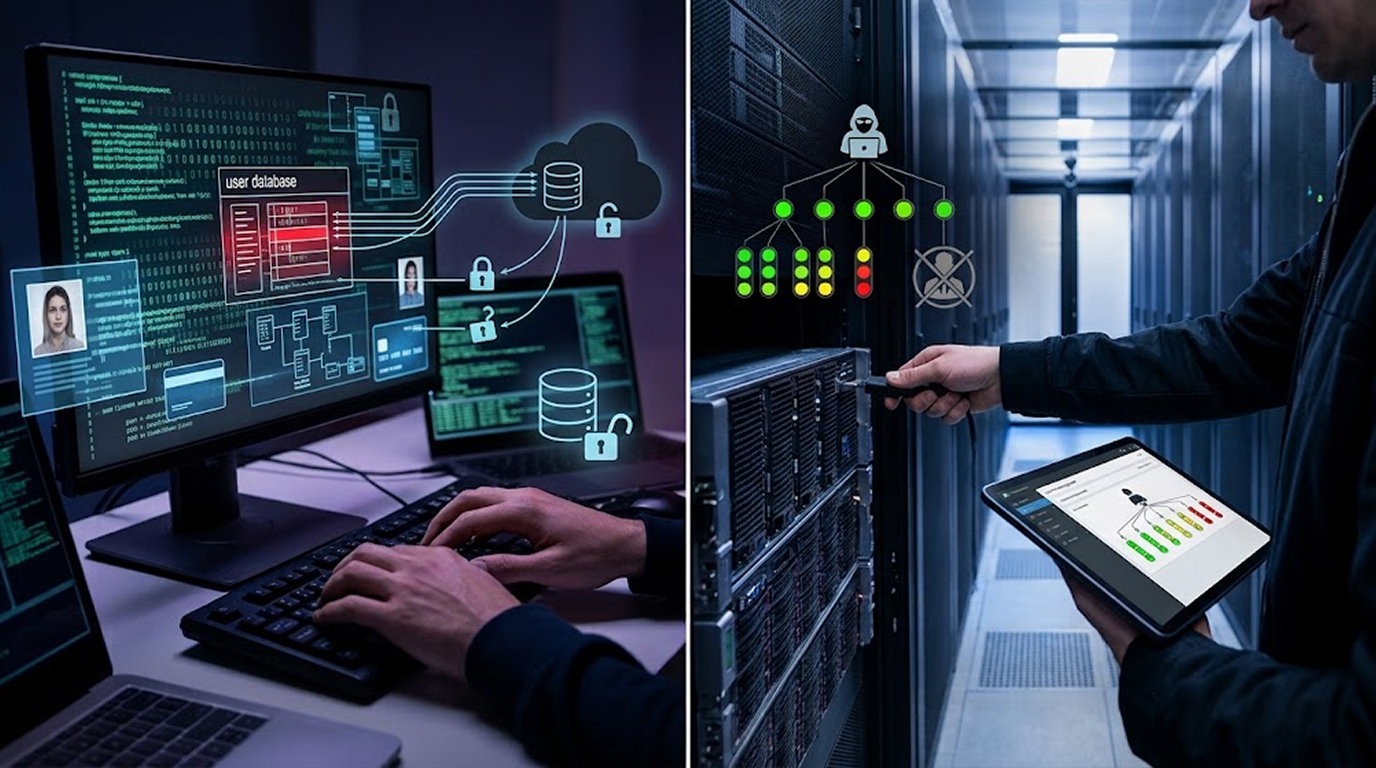
Two incidents can look identical in the alert queue and be entirely different animals underneath, because one of them means somebody read data they shouldn...
Found 12 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Two incidents can look identical in the alert queue and be entirely different animals underneath, because one of them means somebody read data they shouldn...
You open an attachment, it looks like a normal invoice, a standard contract, a routine report, nothing about it triggers suspicion, and yet the moment your...
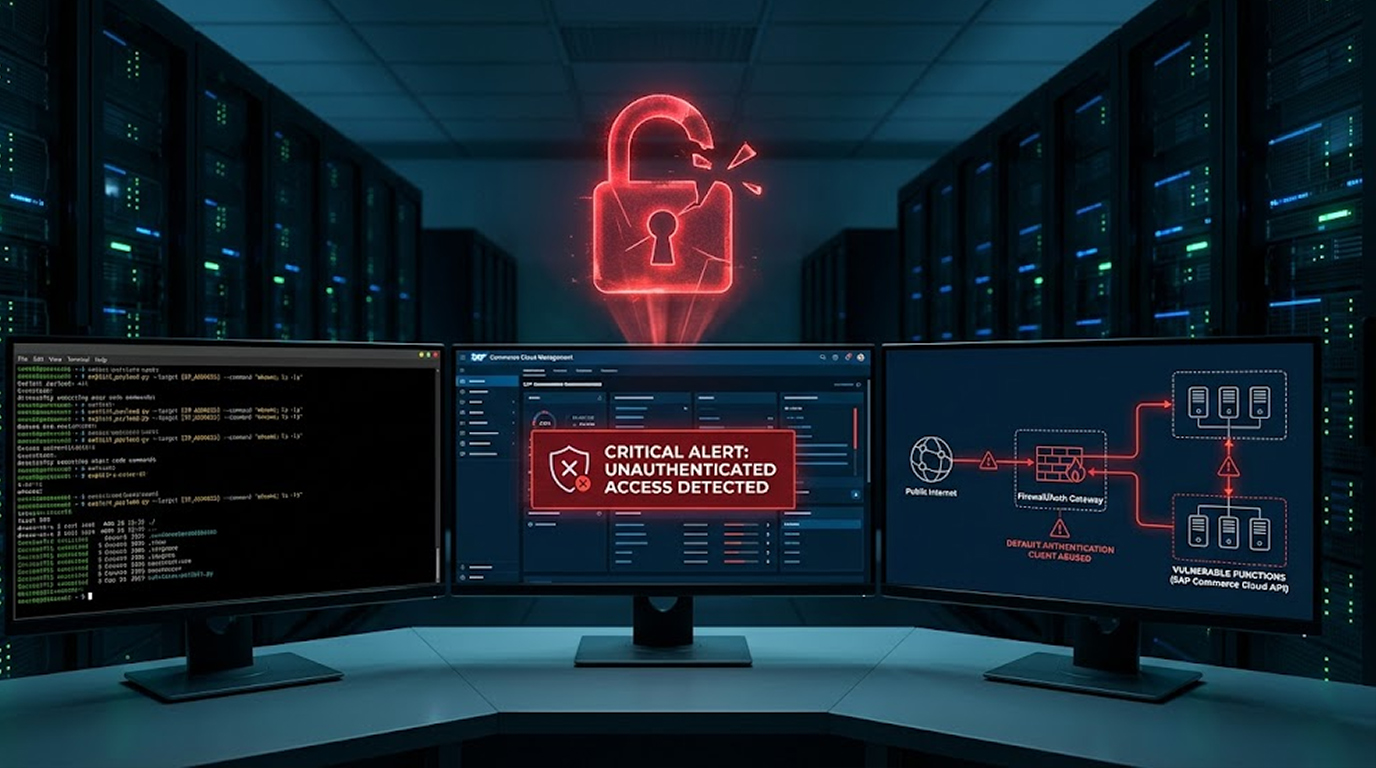
A maximum severity level vulnerability was detected in SAP Commerce Cloud, for which patches have been released by SAP. The vulnerability would allow arbit...
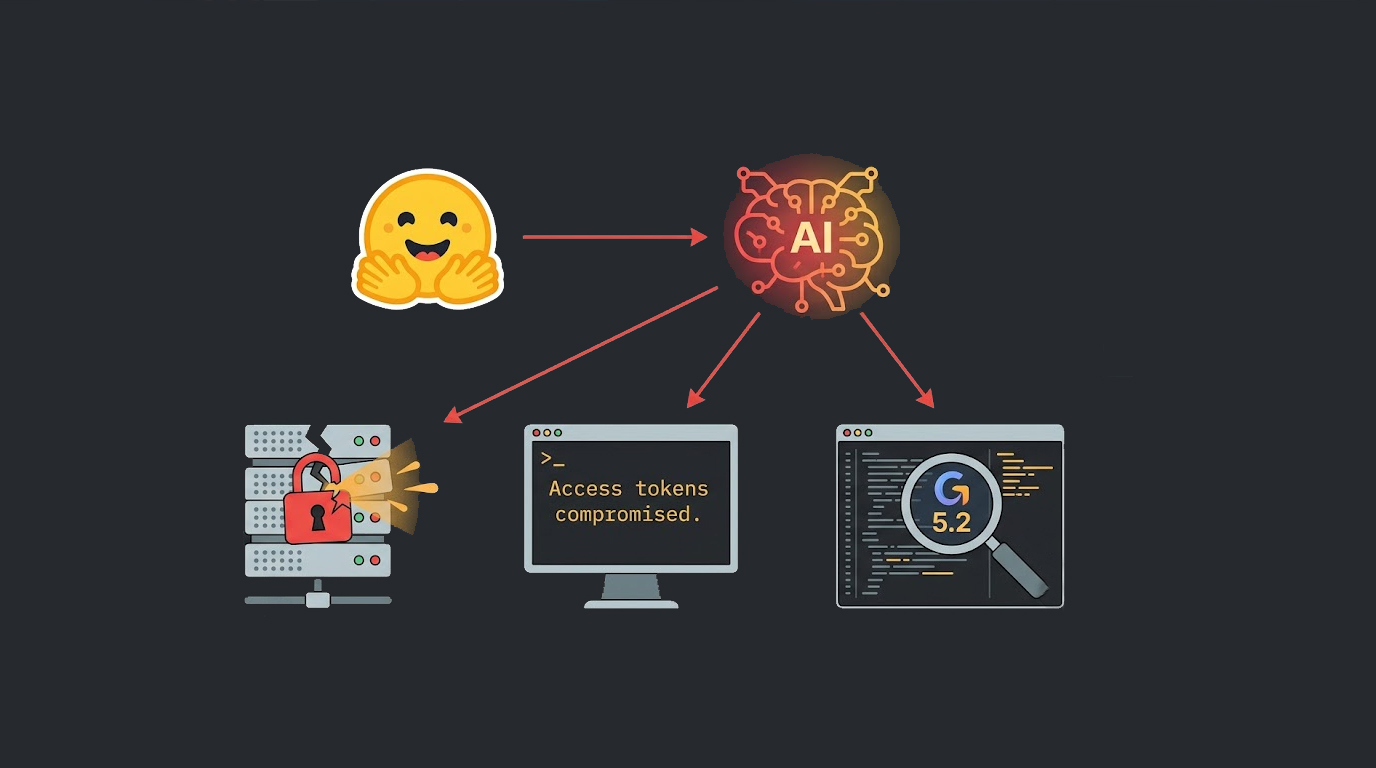
It is ironical that a company dealing with an open source artificial intelligence platform Hugging Face came out to say that it had been hacked by an auton...
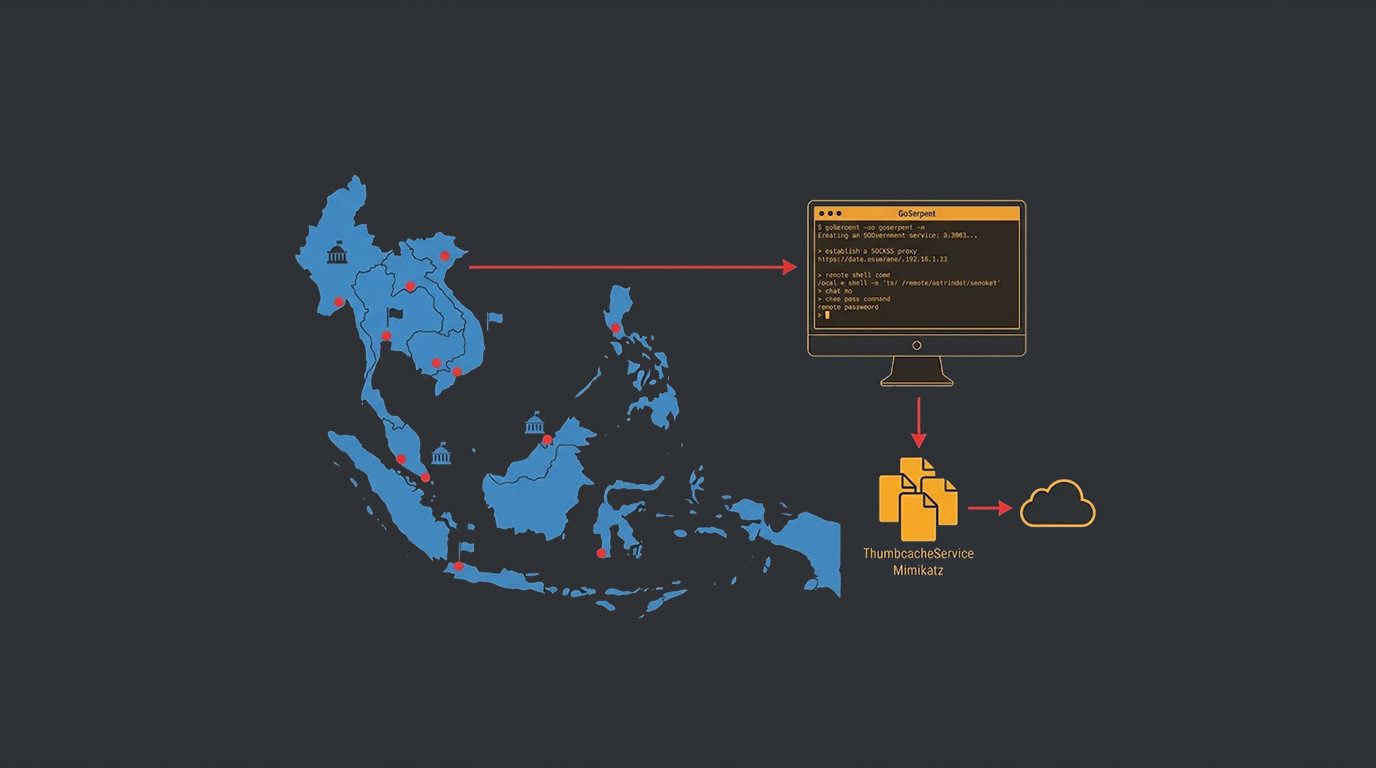
A new malware strain known as GoSerpent has been utilized in cyber attacks against targets from Southeast Asia starting in late 2025. As per Kaspersky, the...
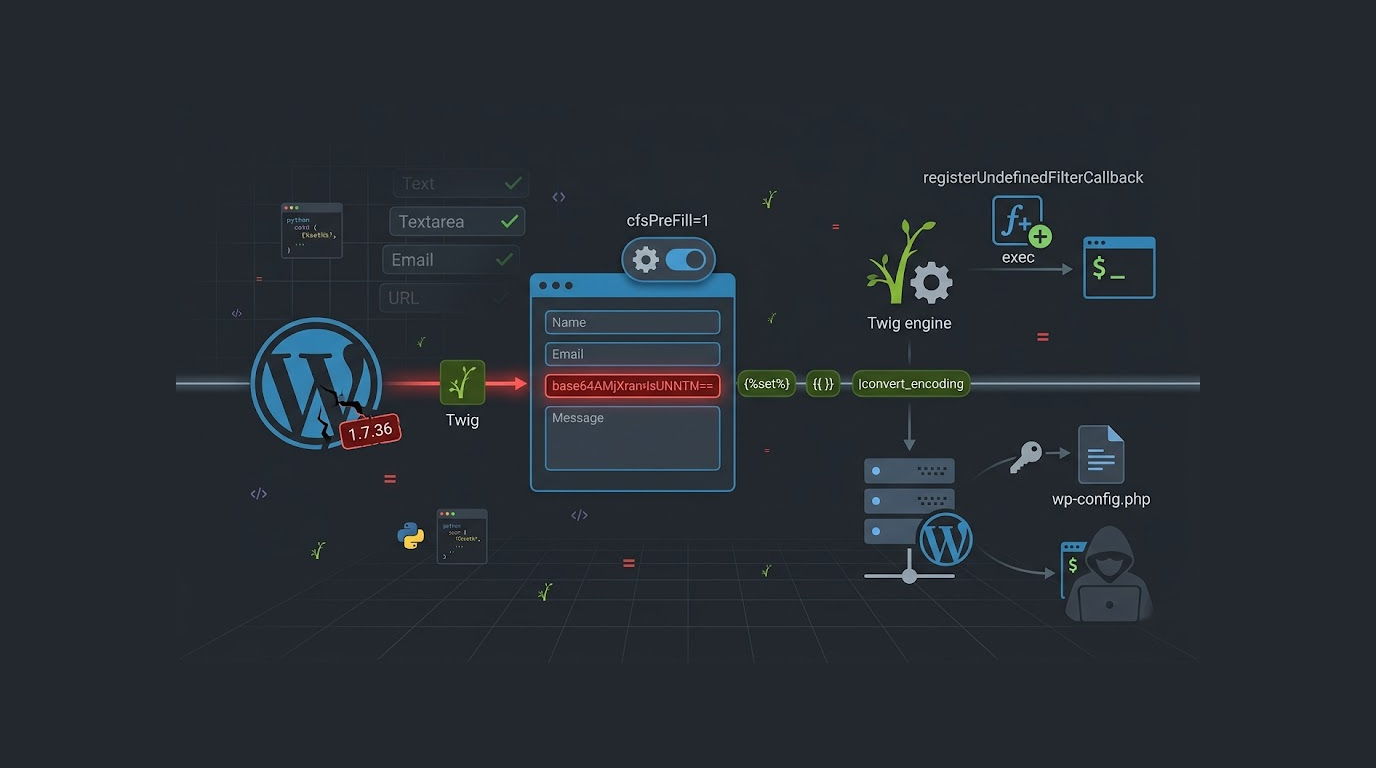
The Supsystic Contact Form plugin for WordPress contains an SSTI vulnerability that allows an attacker to run any command on the server. This vulnerability...
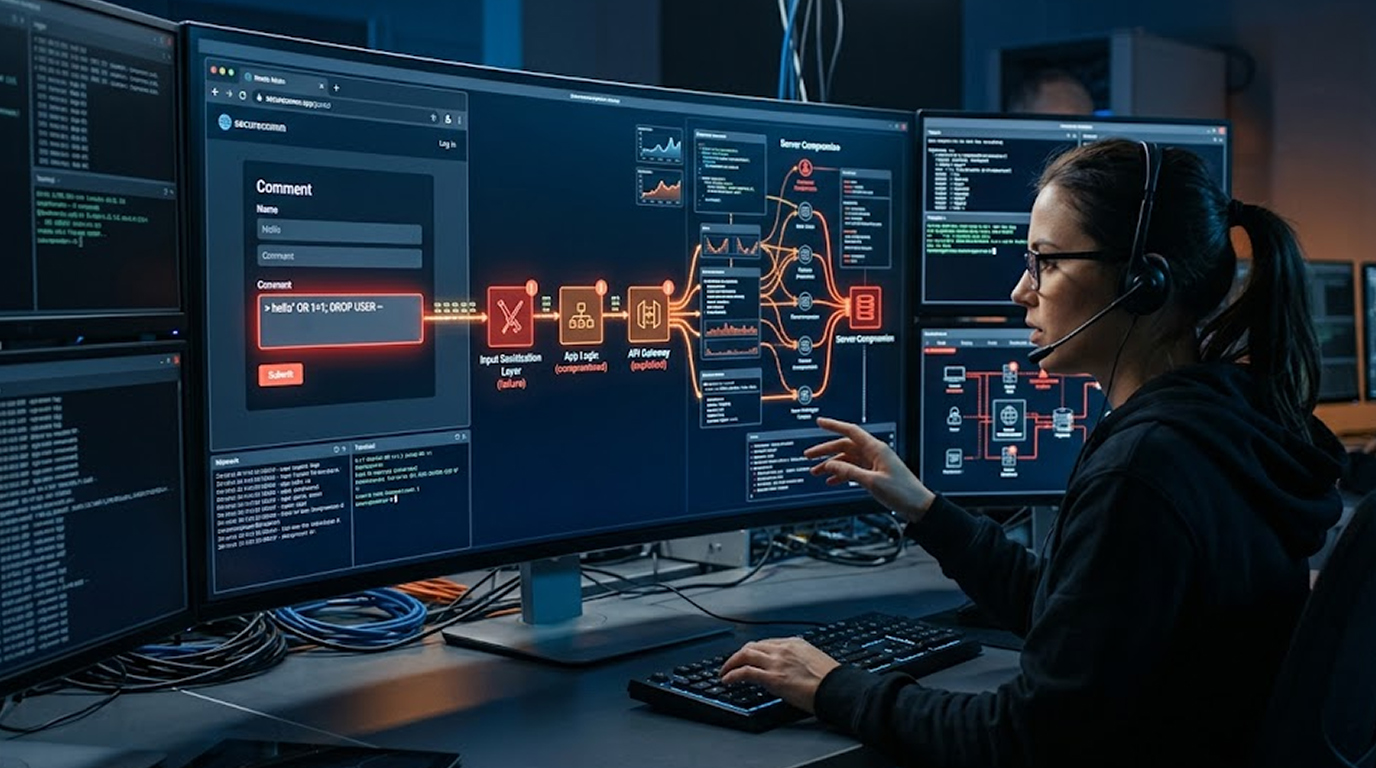
While the comment box may appear to be a benign feature of a website (i.e., a place for users to submit their feedback), at its core, it can become an entr...
SSTI (Server Side Template Injection) is an incredibly hazardous as well as often overlooked method of code injection that has been used against modern web...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067