SignDrop: CLFS Exploit Claims SYSTEM Access
A researcher published exploit code on Tuesday that claims a standard local Windows user can reach SYSTEM privileges through the Common Log File System dri...
Found 82 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A researcher published exploit code on Tuesday that claims a standard local Windows user can reach SYSTEM privileges through the Common Log File System dri...
You type the name of an AI tool. You miss one letter. You land on a page that asks you to verify you are human, or to install a security check, or to run a...
Apple released updates yesterday for two iMessage flaws, and the more serious one is a simple proposition. An attacker could join a group chat they were ne...
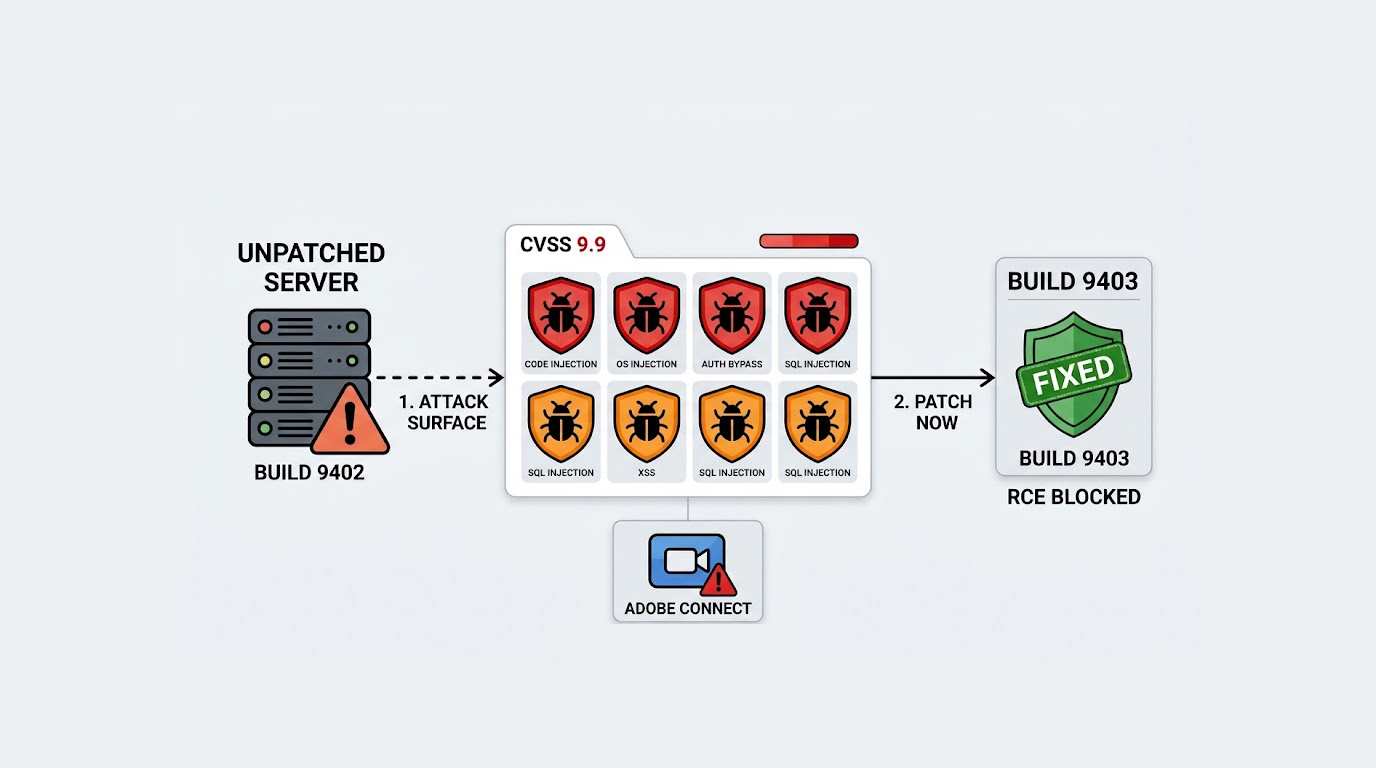
Adobe just dropped a massive security update, and if you are running Adobe Campaign Classic on Windows or Linux, you need to patch your servers right now,...
Security researchers often find themselves waiting for a vendor to release a patch, but when the vendor is a decade-old abandoned piracy app, waiting is no...
Your Node.js server might be running code that can be crashed or compromised by a malformed request, because the project just released security updates fix...
Most site owners think they know their PHP version, because they ran php -v once, saw a number, and assumed that was the answer. It usually is not the ans...
Your self-managed GitLab server might be accepting remote code execution from anyone who sends the right request, because GitLab just released emergency fi...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067