VMware vCenter CVE-2026-59310 Tied to China-Nexus APT
Cybersecurity researchers have linked the exploitation of a recently patched VMware vCenter vulnerability to a suspected Chinese state-sponsored hacking gr...
Found 18 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Cybersecurity researchers have linked the exploitation of a recently patched VMware vCenter vulnerability to a suspected Chinese state-sponsored hacking gr...
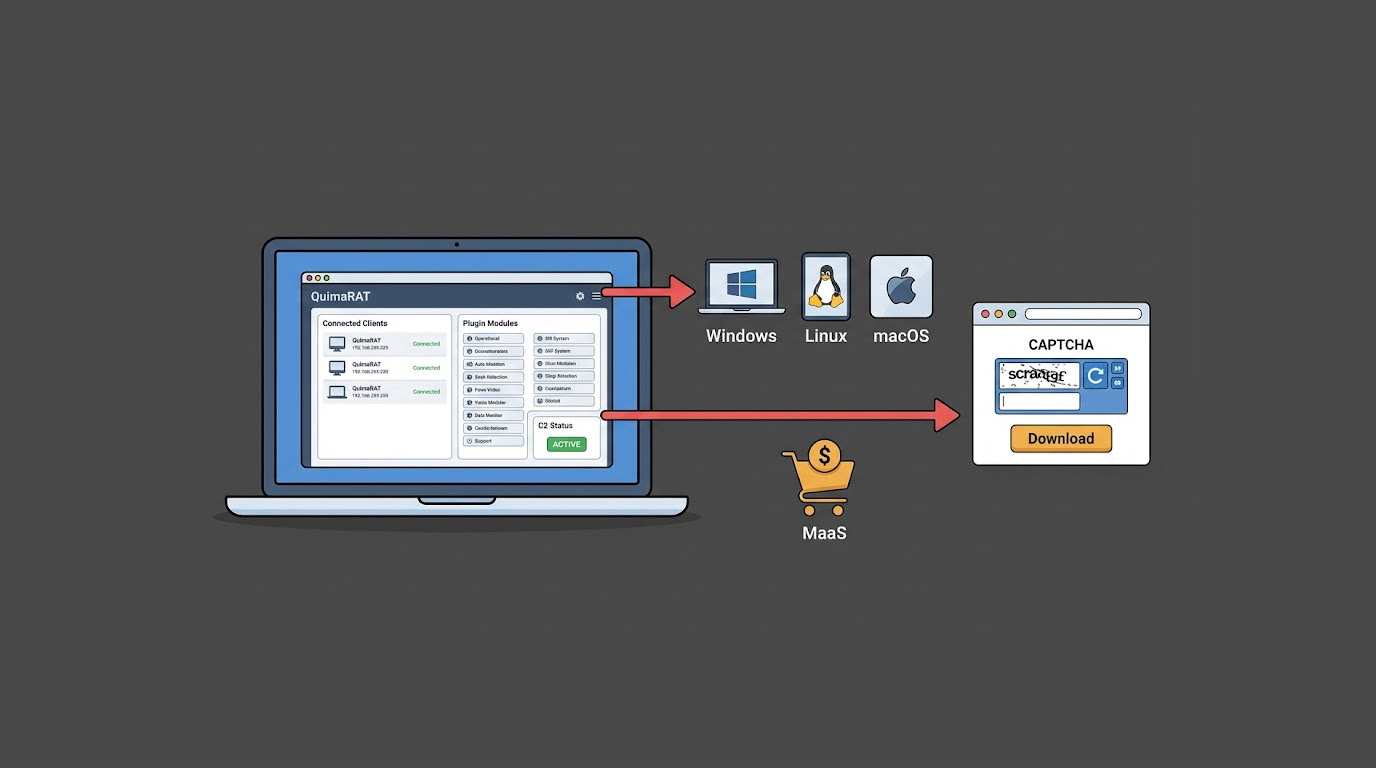
QuimaRAT, which is a new form of Java-based Remote Access Trojan, can attack systems running on Windows, Linux, and macOS platforms. The malware is offered...
You have Kali Linux installed. You know the basics. But when you are in the middle of a penetration test, you need the right command at the right time. You...
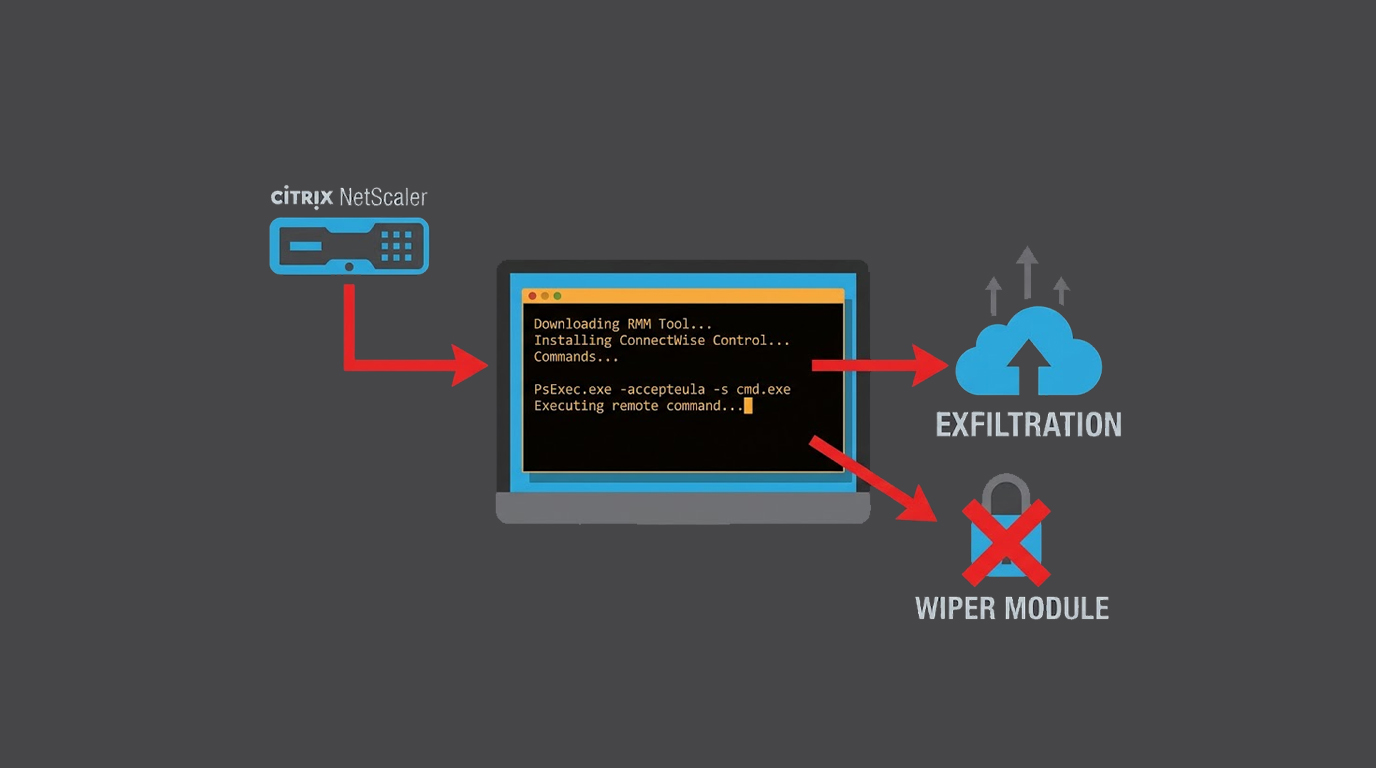
The Anubis Ransomware Campaigns are known to exploit the Citrix Bleed 2 Vulnerability as an initial access vector. The Citrix Bleed 2 Vulnerability i...
Officials and citizens in the Czech Republic and Taiwan have become victims of a new cyber espionage operation called Operation Dragon Weave. Attackers are...
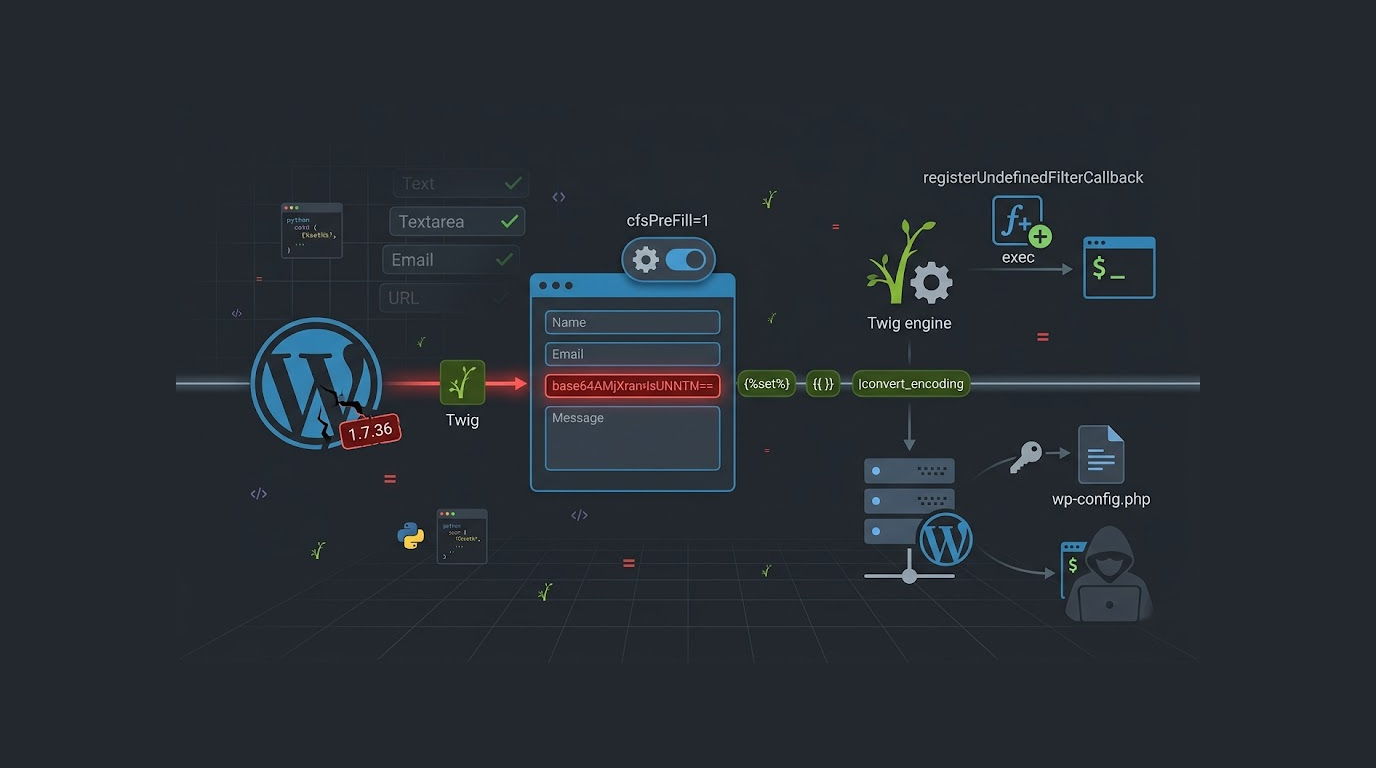
The Supsystic Contact Form plugin for WordPress contains an SSTI vulnerability that allows an attacker to run any command on the server. This vulnerability...
File upload vulnerabilities (CWE-434) let attackers drop webshells, small scripts that provide remote command execution, file management, and persistence o...
A security vulnerability has been recently discovered in Siklu EtherHaul EH-8010 and EH-1200 wireless backhaul devices. The vulnerability allows unauthenti...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067