Check Point Gateway: PHP2Shell to Root to Wiper
Check Point published an incident report this week that reads like a chain-of-custody document, and the chain has five links. Initial access through PHP2Sh...
Found 154 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Check Point published an incident report this week that reads like a chain-of-custody document, and the chain has five links. Initial access through PHP2Sh...
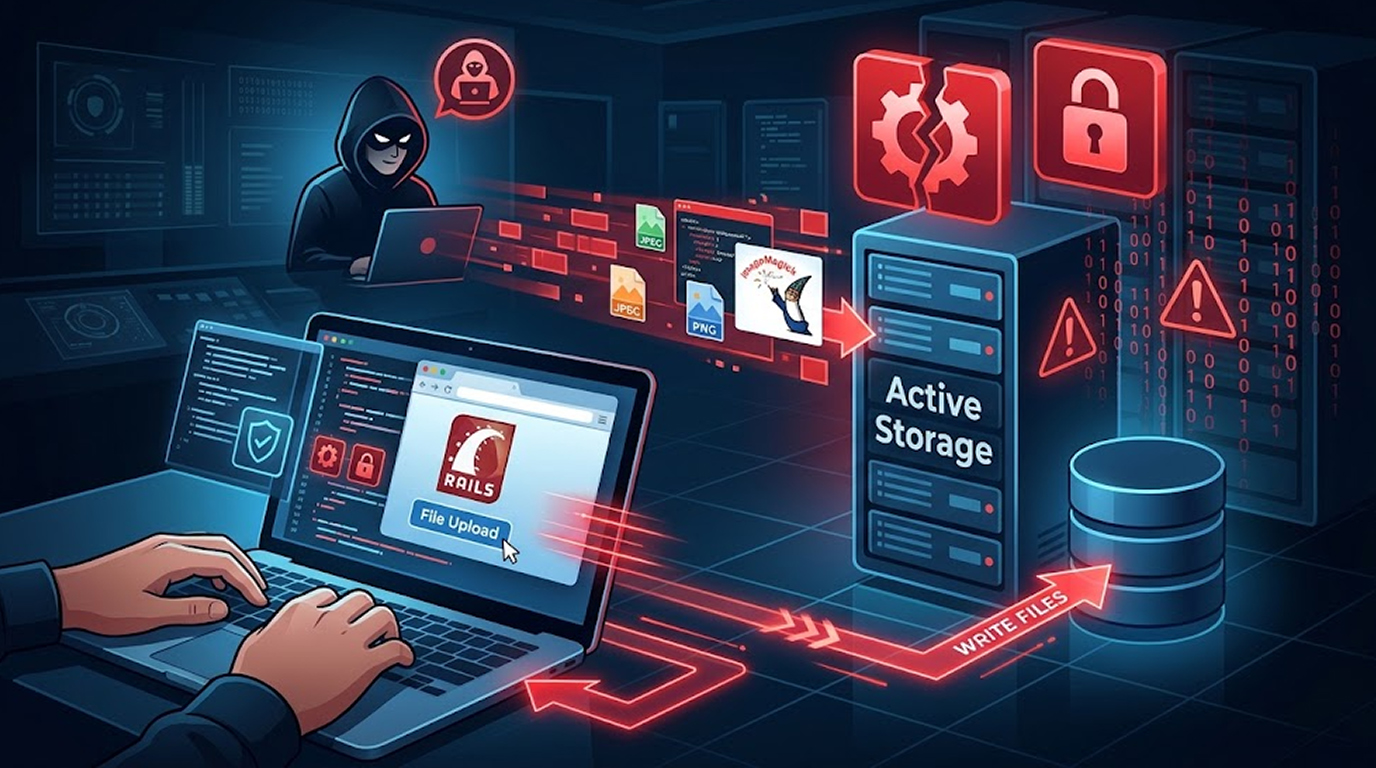
Nine hours. That is how long it took from CVE publication to the first exploitation attempt. The vulnerability is CVE-2026-123158, and it now has a name:...
A single file upload is enough. No authentication, no variant generation, no preview call, no explicit analyze invocation. Just attach the file and the fla...
The mental image most people carry of state-sponsored espionage is a team of elite operators, custom zero-days, and infrastructure that costs more than a s...
There's a moment that separates a stolen credential from a compromised network, and it lasts about five minutes, because that's roughly how long an attacke...
When a vendor gets breached, the first thing most organizations discover is that they have almost no visibility into what happened, because the compromised...
Most ransomware crews rely on human operators to manually pivot through a network and hunt for sensitive files, but a Russian-speaking group tied to the IN...
You see the advisory, you see the severity rating, and you think you understand the risk, and then you patch it and move on, and that is where most people...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067