How to Check for a Web Shell Uploader on Your Site
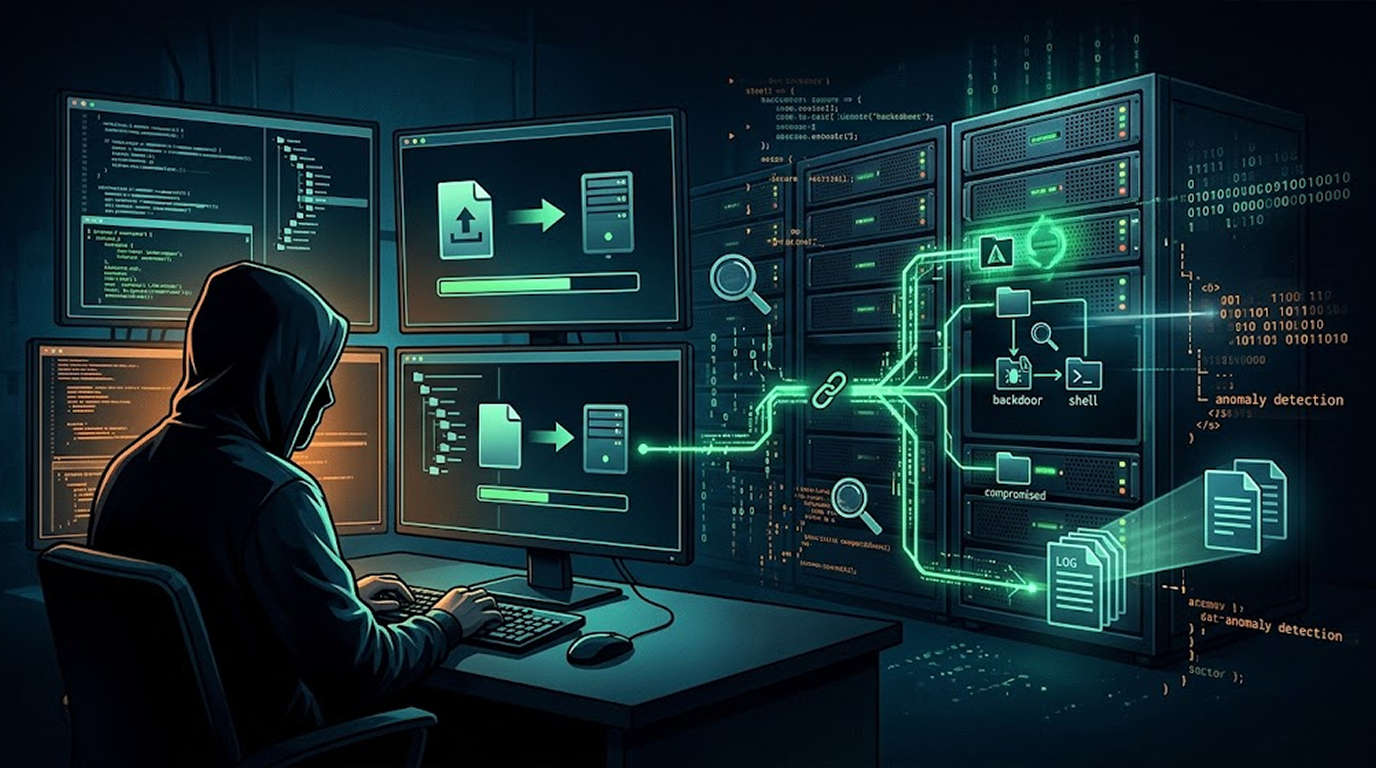
You patched the vulnerability, you removed the suspicious file, and you thought the incident was over, then two weeks later the same thing happens again, b...
Found 10 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You patched the vulnerability, you removed the suspicious file, and you thought the incident was over, then two weeks later the same thing happens again, b...
Two critical WordPress plugin vulnerabilities are making the rounds. One is being actively exploited right now. The other is a pair of flaws that could let...
Mozilla has released updates to address two critical flaws in Firefox for which exploit code has been published. Google has shipped fixes for 15 security f...
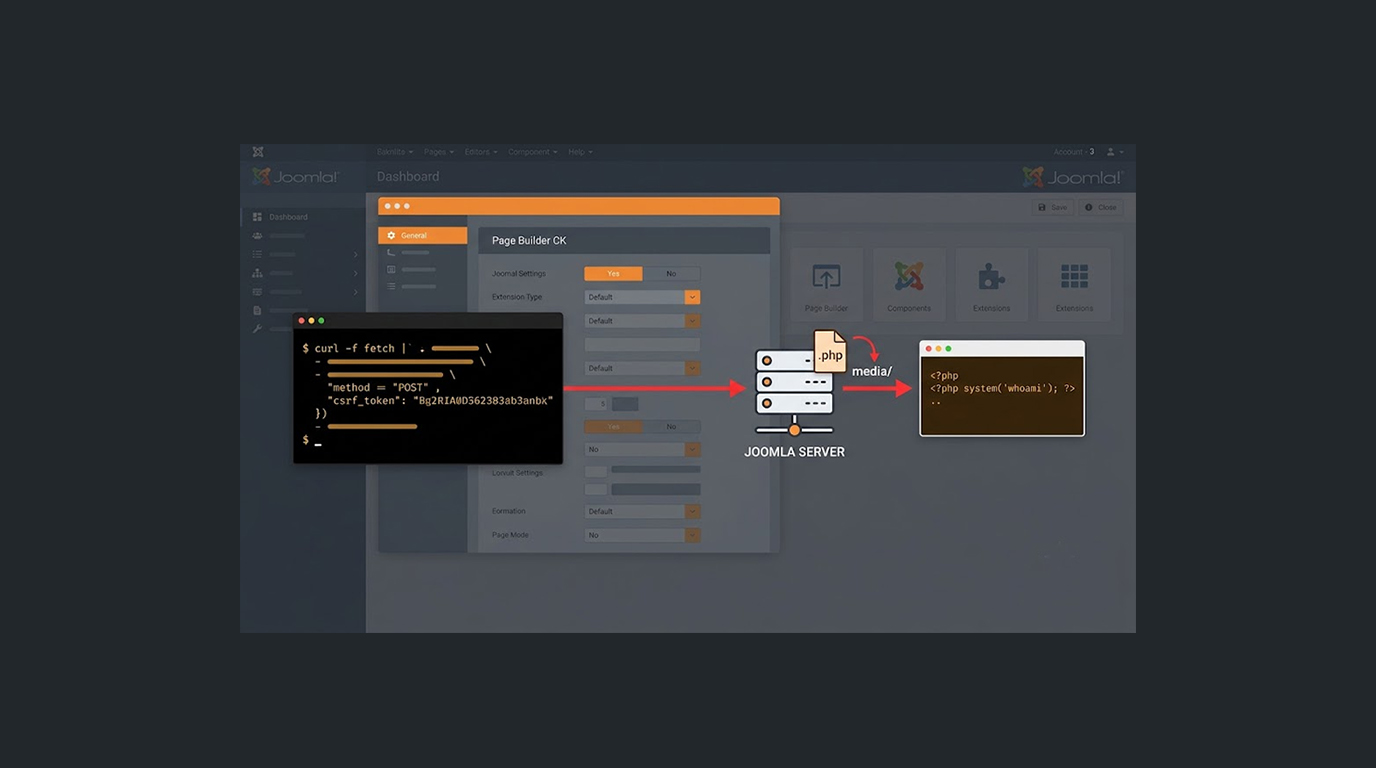
There is a serious vulnerability in Joomla Page Builder CK which enables an attacker without authentication to upload PHP files and run arbitrary code on t...
File upload vulnerabilities (CWE-434) let attackers drop webshells, small scripts that provide remote command execution, file management, and persistence o...
Vulnerability exists in Pluck CMS's facility for uploading files to execute PHP on its server. The primary source of the vulnerability results from the pro...
File upload features look harmless. Let users attach a document, upload an image, move on. In practice, these features are one of the most abused parts of...
Two security vulnerabilities have been disclosed in the open-source Traccar GPS tracking system, which could be exploited by unauthenticated attackers to a...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067