SSHole: OpenSSH Flaw Exploited Within 9 Hours
Nine hours. That is how long it took from CVE publication to the first exploitation attempt. The vulnerability is CVE-2026-123158, and it now has a name:...
Found 47 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Nine hours. That is how long it took from CVE publication to the first exploitation attempt. The vulnerability is CVE-2026-123158, and it now has a name:...
The mental image most people carry of state-sponsored espionage is a team of elite operators, custom zero-days, and infrastructure that costs more than a s...
IBM just published details on two critical flaws in Langflow, an open-source tool for building AI agents and workflows, and the combination is about as bad...
There's a moment that separates a stolen credential from a compromised network, and it lasts about five minutes, because that's roughly how long an attacke...
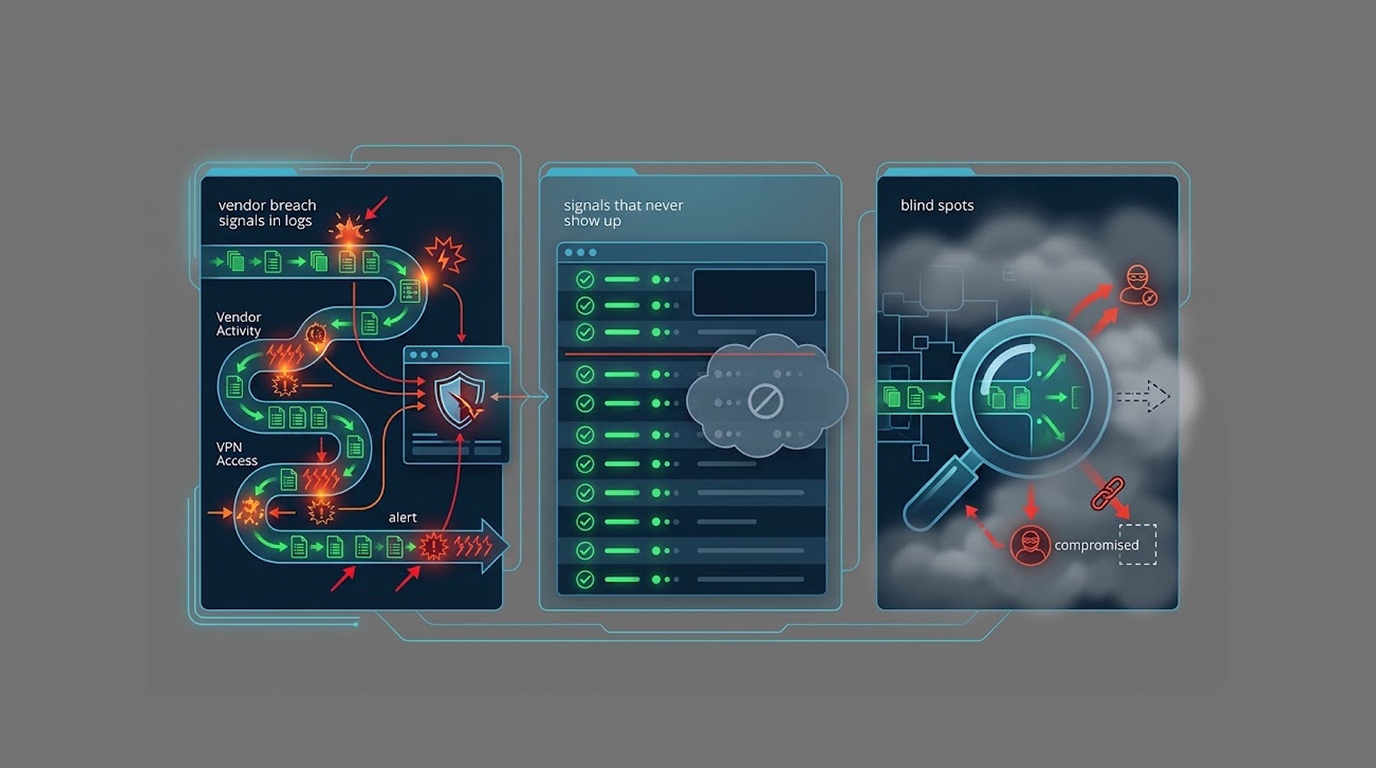
When a vendor gets breached, the first thing most organizations discover is that they have almost no visibility into what happened, because the compromised...
Your repository might look clean and still be compromised, because the actor behind GhostAction has moved past injecting workflows entirely, and the new Gh...
A threat actor called JADEPUFFER, which Microsoft tracks as Storm-3168, ran a destructive campaign inside a Microsoft Azure environment over about 18 hours...
Anthropic just dropped a 154-page report that should make anyone in security sit up straight. Between December 2025 and August 2026, cybercriminals and sta...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067