Measuring Security Culture: What Predicts Fewer Incidents
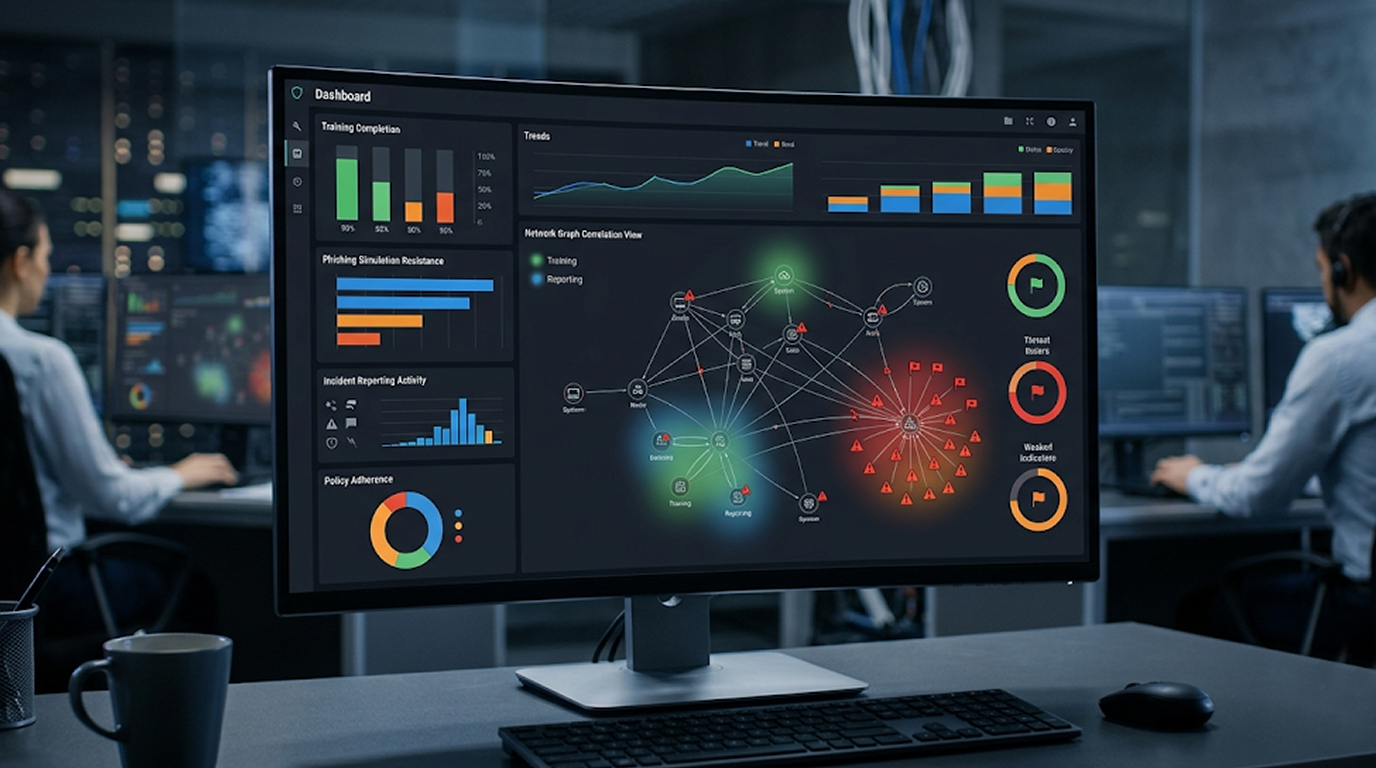
Many organizations invest heavily in security tools, training completion rates, and compliance checklists, yet these often do not lead to a reduction of ac...
Found 7 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Many organizations invest heavily in security tools, training completion rates, and compliance checklists, yet these often do not lead to a reduction of ac...
Cisco Talos just pulled back the curtain on DKnife, one of the most sophisticated adversary-in-the-middle (AitM) frameworks we've seen from China-nexus act...
cert-ua has disclosed that there is a cyberespionage campaign against the Ukrainian military that ran from October to December 2025, with a distinct malwar...
Researchers in cybersecurity have discovered a new campaign involving malware that uses WhatsApp as an avenue for spreading the Astaroth banking trojan (a...
In a recent campaign dubbed "Hidden Risk," the North Korean-linked threat actor BlueNoroff has been targeting cryptocurrency businesses with a sophisticate...
Over the past year, more than 140,000 phishing websites have been discovered connected to the Sniper Dz Phishing-as-a-Service (PhaaS) platform, highlightin...
Email phishing is one of the most common and dangerous types of cyberattacks, where attackers pose as legitimate sources to trick victims into sharing pers...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067