CryptoPayment Gateway Flaw: CVSS 10.0 Exploited
Some WordPress plugin vulnerabilities need a clever chain of conditions. A specific role, a particular setting, a user who clicks something they should not...
Found 15 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Some WordPress plugin vulnerabilities need a clever chain of conditions. A specific role, a particular setting, a user who clicks something they should not...
You see the advisory, you see the severity rating, and you think you understand the risk, and then you patch it and move on, and that is where most people...
Website Malware Removal: The Complete Guide Website malware removal is the process of identifying malicious code on a compromised website, removing infect...
There's a bug in FreePBX that lets someone walk in without a login, drop a cron job, and get a shell on your server. No username. No password. Just a web r...
Cybersecurity researchers have linked the exploitation of a recently patched VMware vCenter vulnerability to a suspected Chinese state-sponsored hacking gr...
Threat actors have started to target a critical security vulnerability that has been recently patched by Broadcom VMware vCenter. The vulnerability gives a...
You have heard the terms. Red team attacks. Blue team defends. But when you look at the actual commands, what is the difference? The answer is not the too...
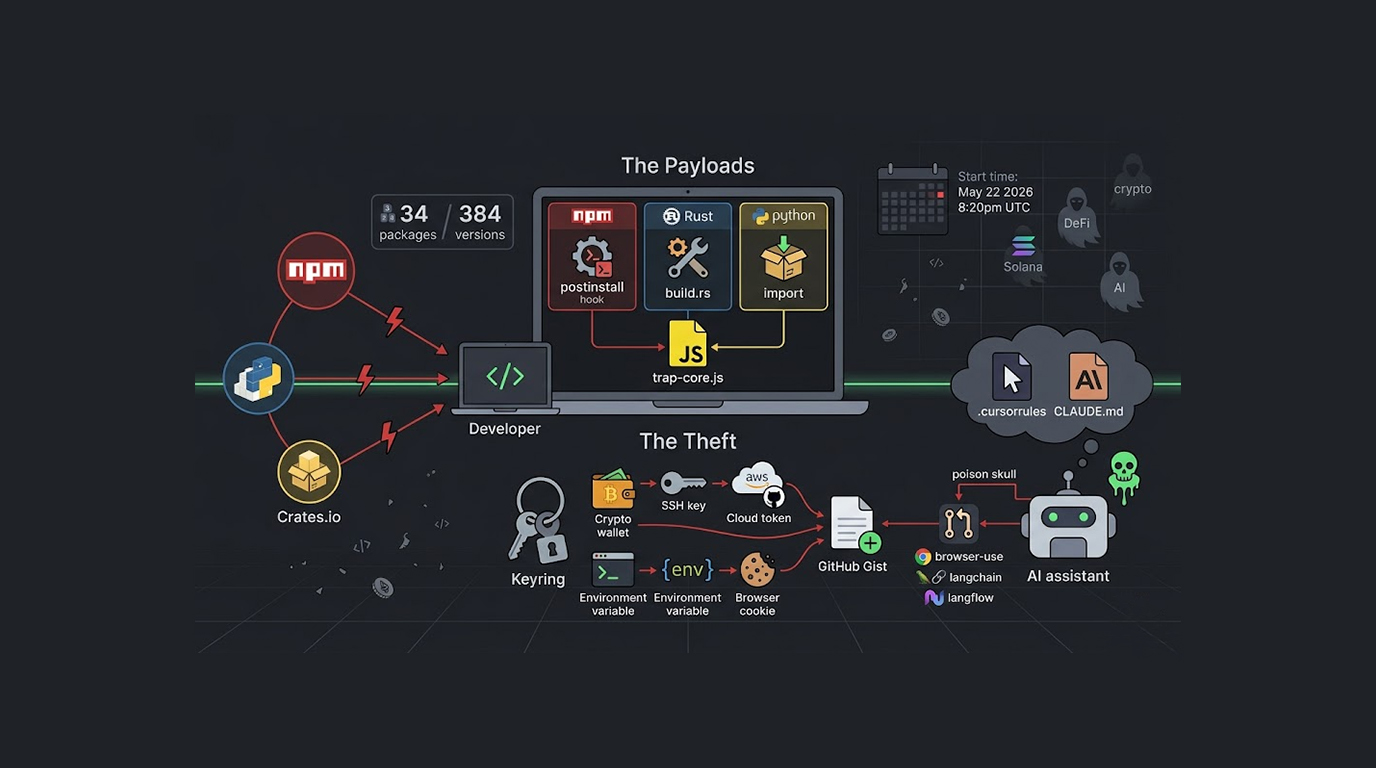
A new coordinated supply chain attack campaign has targeted three major package registries simultaneously, and the attackers are stealing developer credent...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067