MFT Zero-Day Exploits: Why One Bug Hits Thousands
There is a category of software that has been exploited more reliably than any other over the past five years, and most organizations do not think of it as...
Found 72 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There is a category of software that has been exploited more reliably than any other over the past five years, and most organizations do not think of it as...
Every week brings a headline about a new malware family, a new name, a new logo, a new dashboard on some leak site, and it is easy to get pulled into chasi...
Qilin is not just another ransomware group. It is the most operationally active ransomware operation on the planet. And it has figured out how to use artif...
Cisco just dropped patches for a critical security flaw affecting 10 of its Nexus 9000 switches. The vulnerability, tracked as CVE-2026-20212, allows attac...
The U.S. government just issued a warning that should make anyone in critical infrastructure sit up and take notice. An active threat is targeting industri...
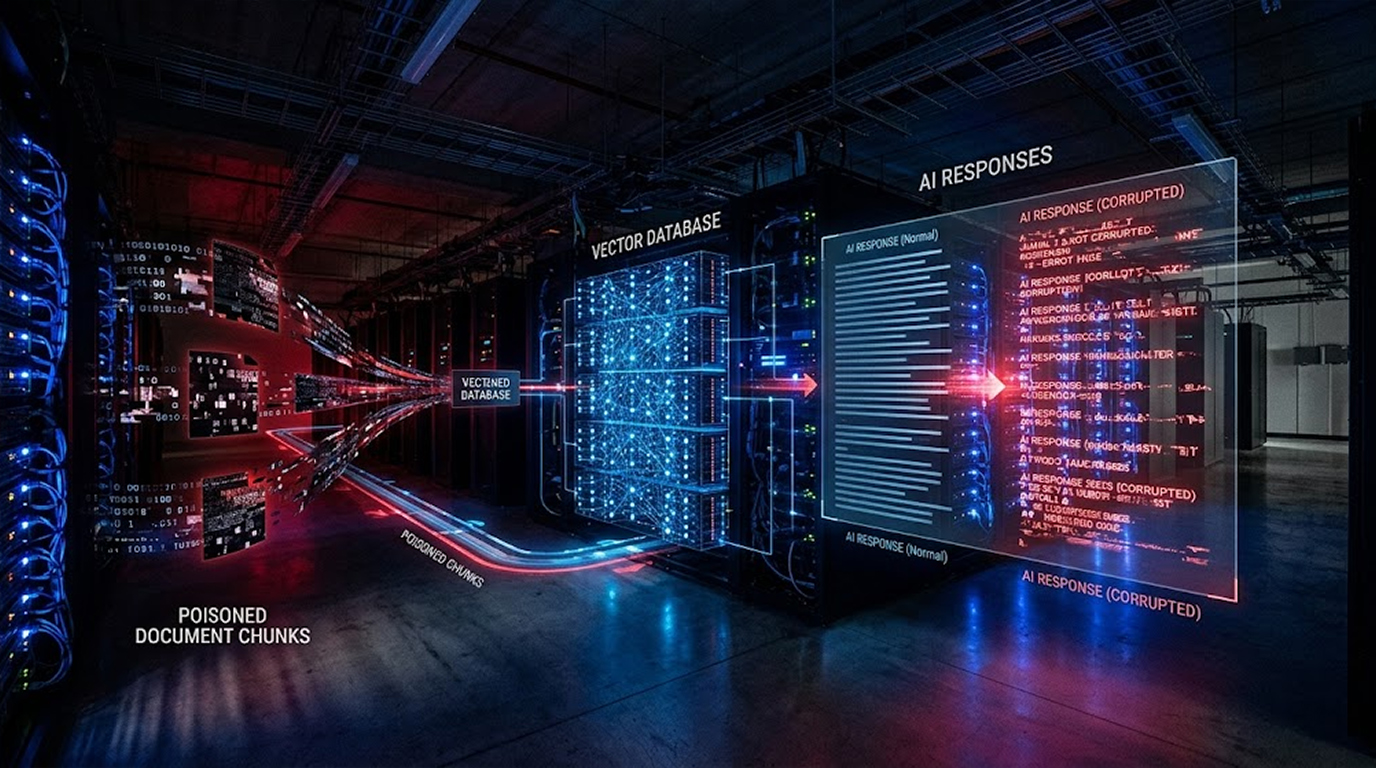
Your AI assistant just told a developer to install a malicious package. It cited a "trusted" internal document as the source. The document looked legitimat...
A Warning about Gunra Ransomware Threats on Critical Infrastructure Sectors across the worldwide Issued by South Korean and US Cyber Security and Intellige...
PortSwigger's James Kettle has built an AI-assisted research system called HTTP Terminator that generated and proved new HTTP desynchronization techniques...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067