GitLab AI Gateway Flaw: CVE-2026-90970 Patch Guide
Your self-hosted GitLab AI Gateway might be carrying a flaw that hands command execution to any logged-in user with Duo Agent Platform access, because GitL...
Found 9 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your self-hosted GitLab AI Gateway might be carrying a flaw that hands command execution to any logged-in user with Duo Agent Platform access, because GitL...
Cybersecurity researchers have found that the Cavern command and control framework set continues to evolve. The toolkit is used by Iranian nation-sta...
A maximum severity level vulnerability was detected in SAP Commerce Cloud, for which patches have been released by SAP. The vulnerability would allow arbit...
A critical severity vulnerability in the Progress Kemp LoadMaster load balancer has been added to CISA’s Known Exploited Vulnerabilities list. The ad...
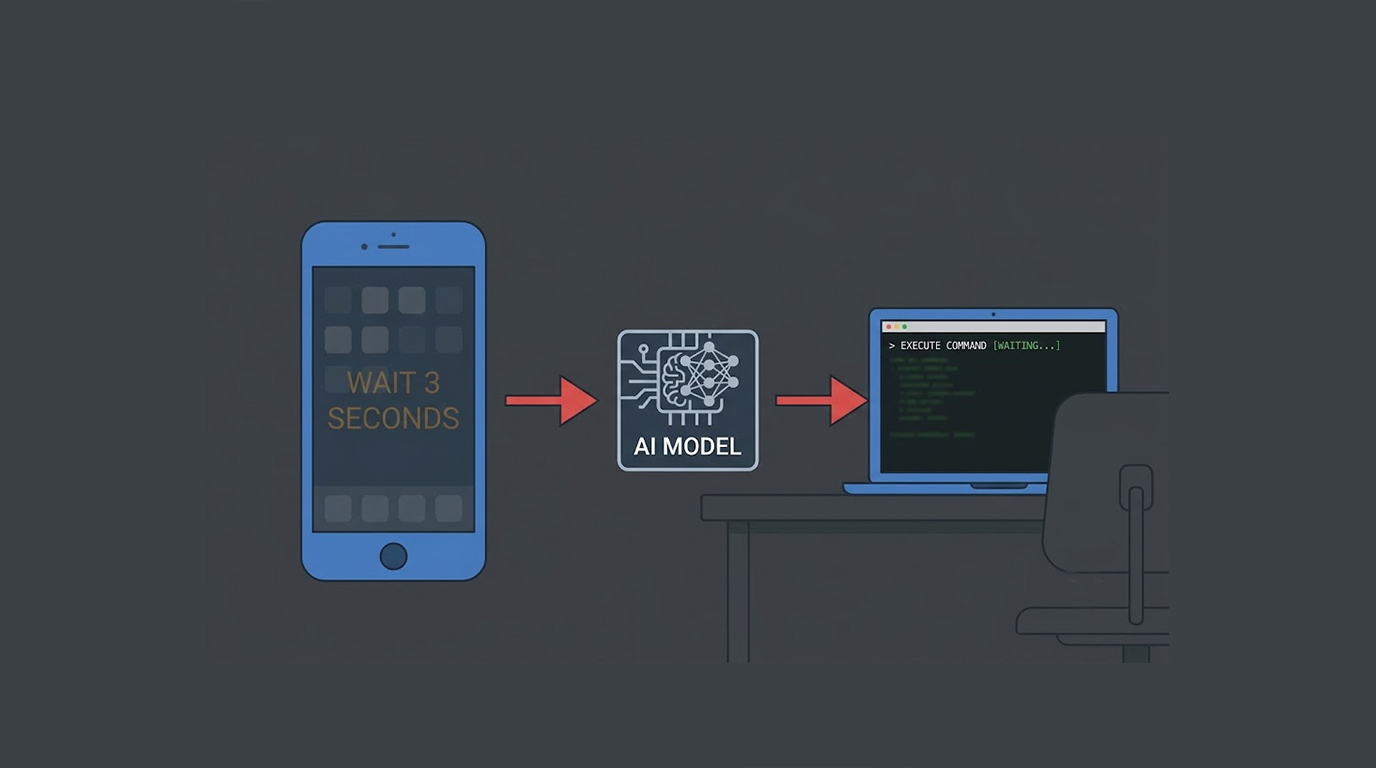
An Android app that can overlay other windows and write to shared storage can feed instructions into the artificial intelligence agent running the phone th...
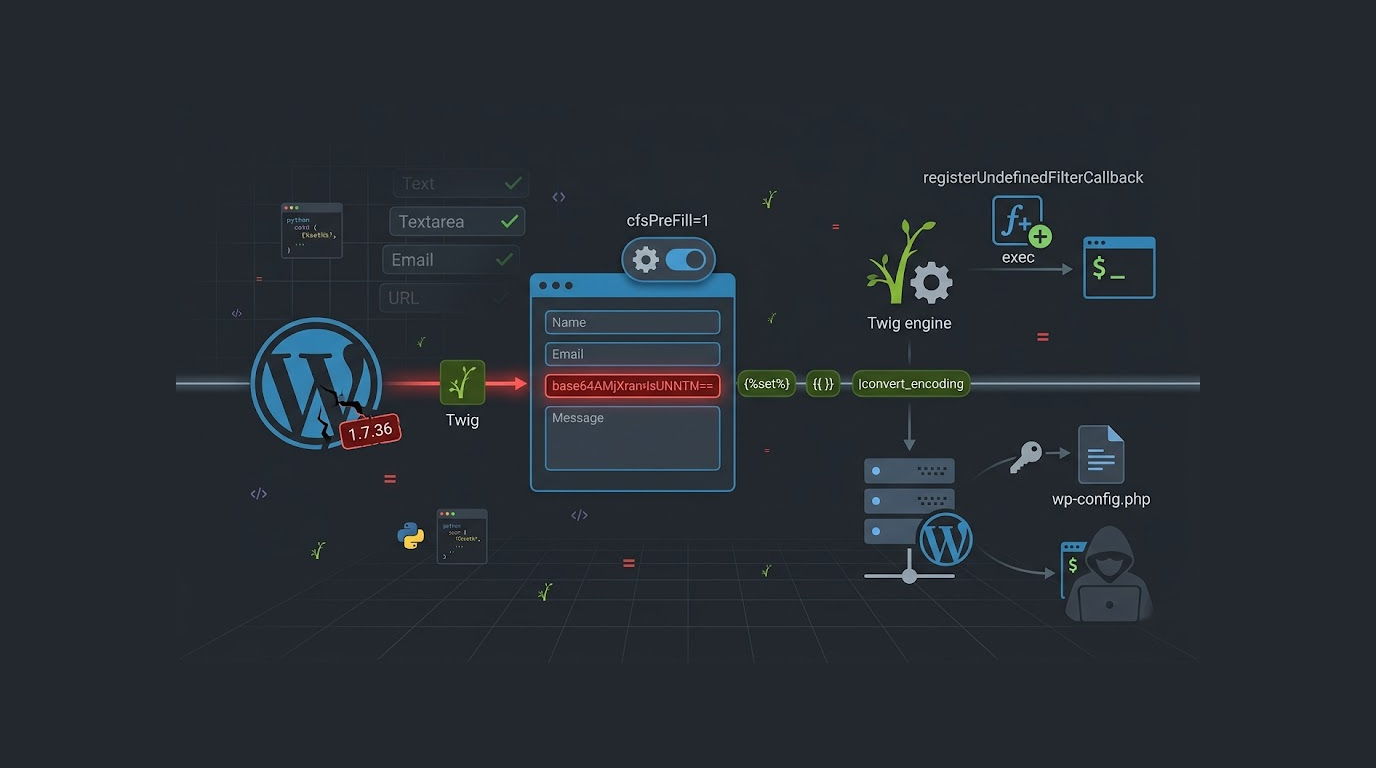
The Supsystic Contact Form plugin for WordPress contains an SSTI vulnerability that allows an attacker to run any command on the server. This vulnerability...
A critical vulnerability in a popular enterprise office automation platform is being actively exploited. Attackers need no password. No username. No specia...
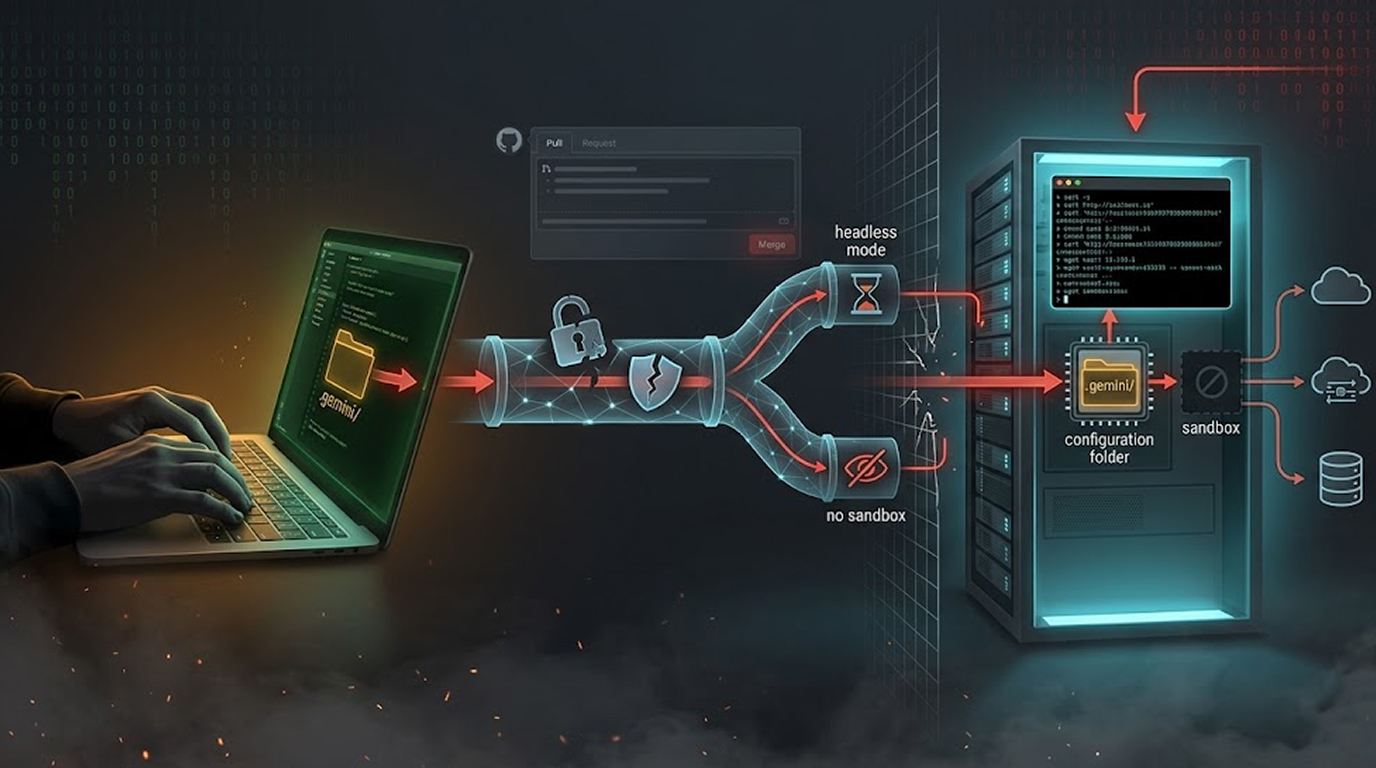
A perfect 10. That is the CVSS score Google assigned to a security flaw in its Gemini CLI tool. And for good reason. The Gemini CLI remote code execution...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067