AIT-GUI NASA Flaw Allows Unauthenticated Spacecraft Commands
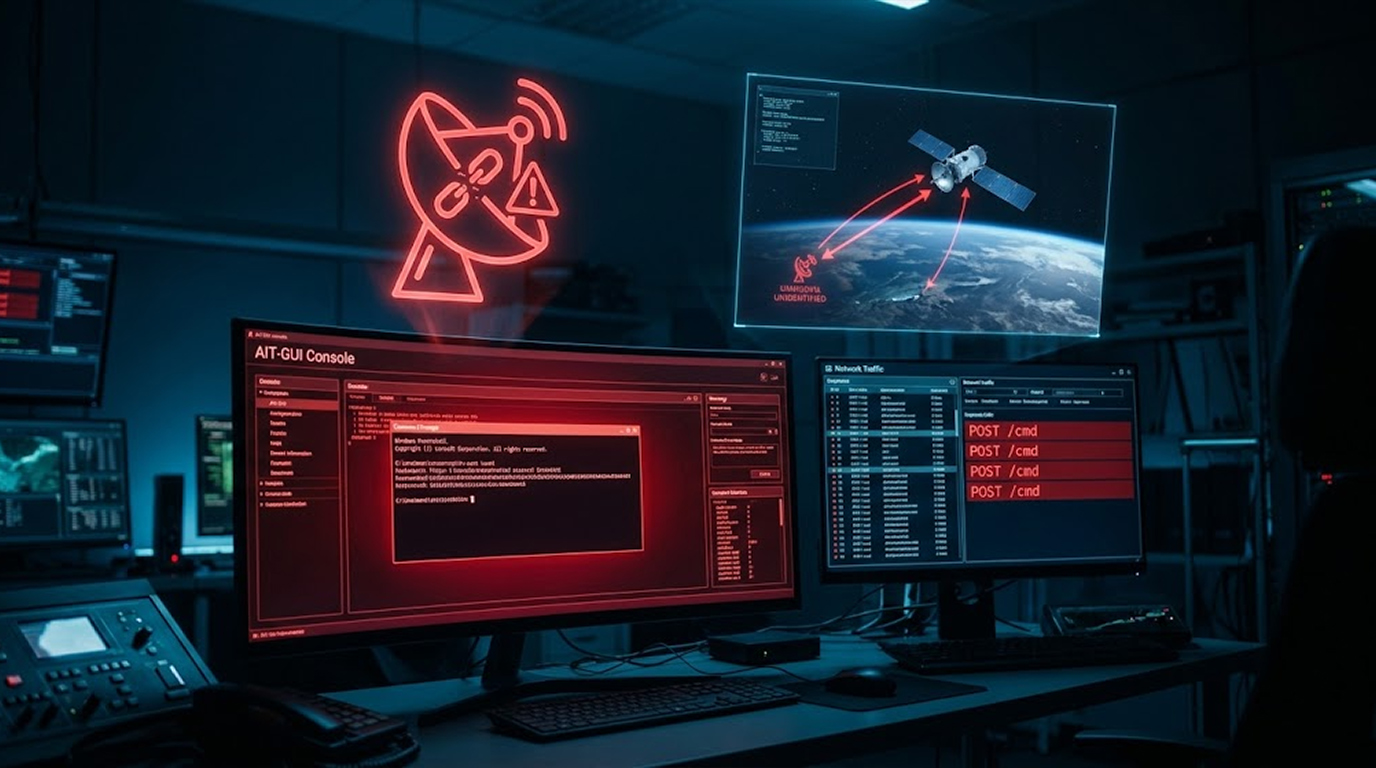
Security researchers just found a vulnerability in software used by NASA's Jet Propulsion Laboratory. The flaw is in AIT-GUI, the browser-based console tha...
Found 8 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Security researchers just found a vulnerability in software used by NASA's Jet Propulsion Laboratory. The flaw is in AIT-GUI, the browser-based console tha...
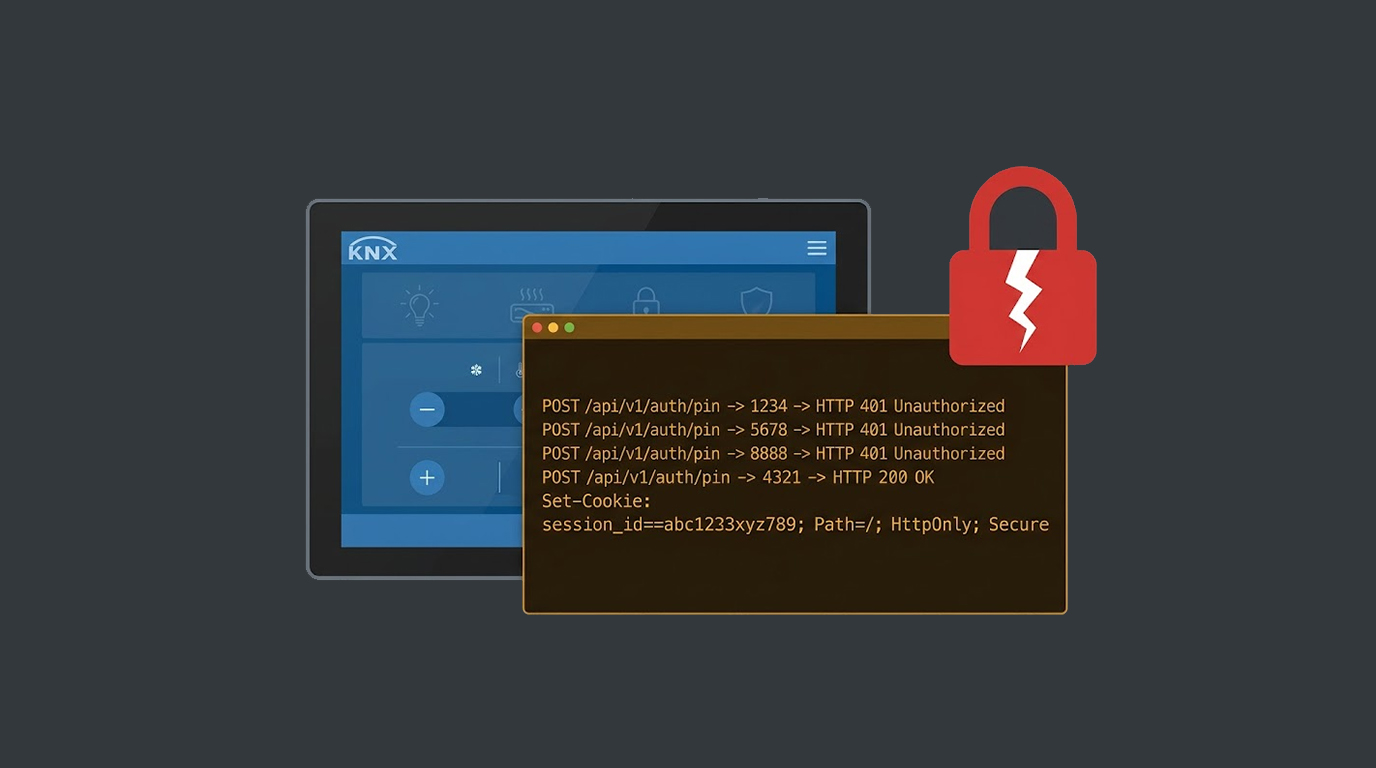
Vulnerability in KNX visualisering panels can compromise the smart building control system due to an unauthorized access attack. The vulnerability is broug...
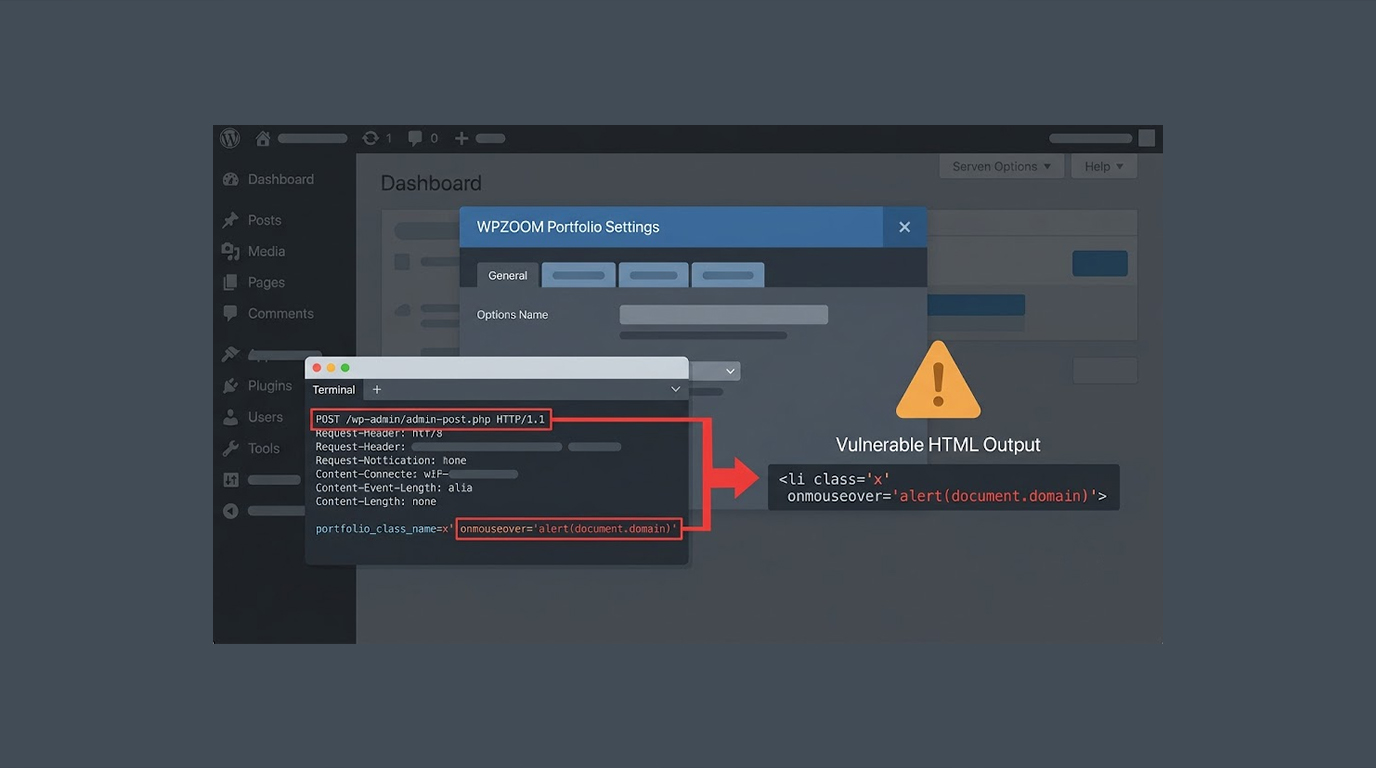
A cross-site scripting (XSS) vulnerability exists within the WPZOOM Portfolio plug-in versions 1.4.21 or earlier. This vulnerability enables the att...
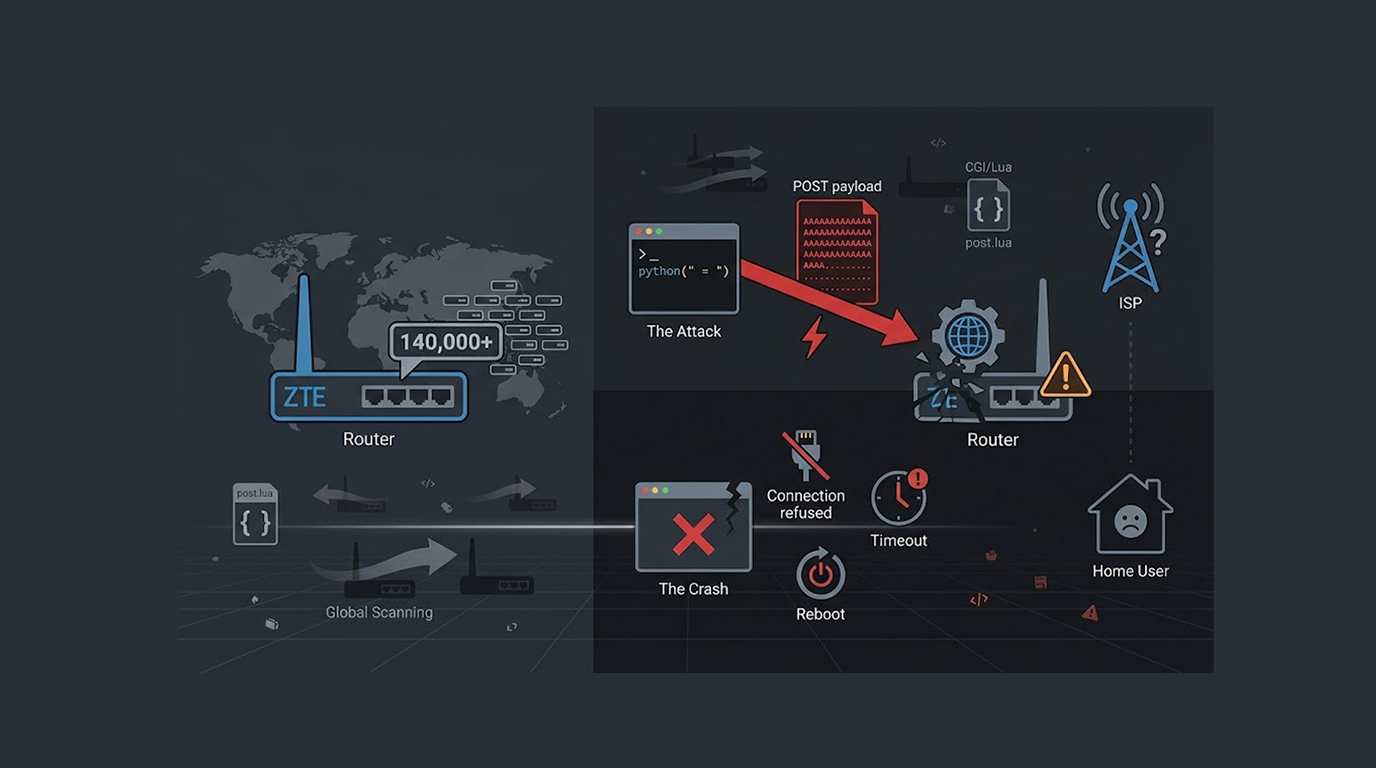
A flaw in ZTE router devices creates a vulnerability that permits unauthenticated users an ability to crash their management interface with a single, large...
Local File Inclusion (LFI) is flagged as a high-severity vulnerability within the Madara Theme for Wordpress that permits unauthenticated attackers to read...
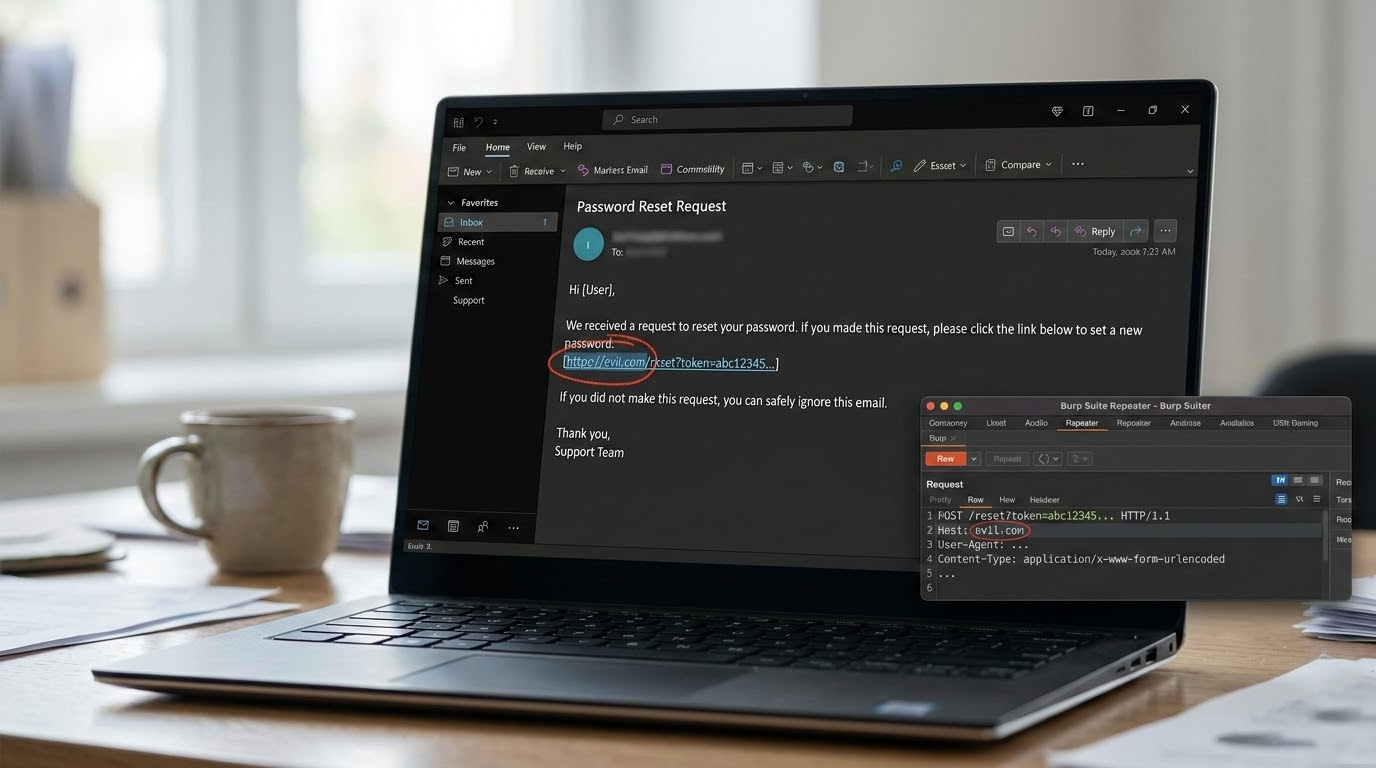
Password reset poisoning (also called Host header poisoning in reset flows) is one of those “old but gold” vulnerabilities that refuses to die....
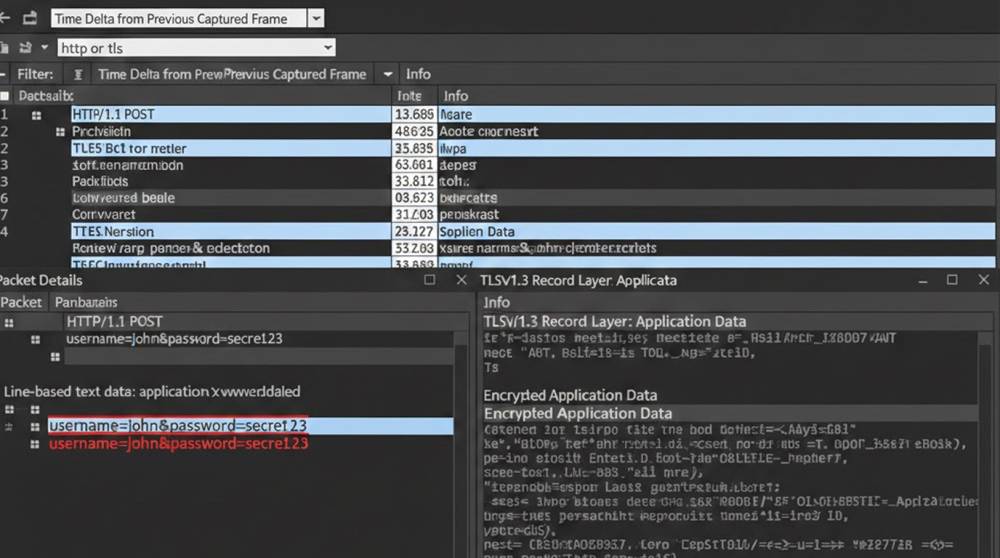
When you capture network traffic with Wireshark, the difference between plaintext (HTTP) and encrypted (HTTPS/TLS) becomes very obvious and very usef...
These three vulnerabilities are among the most common ways attackers break into web applications. They all happen through normal-looking HTTP GET or POST r...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067