APT Flaw: A Malicious Mirror Can Swap Your Packages
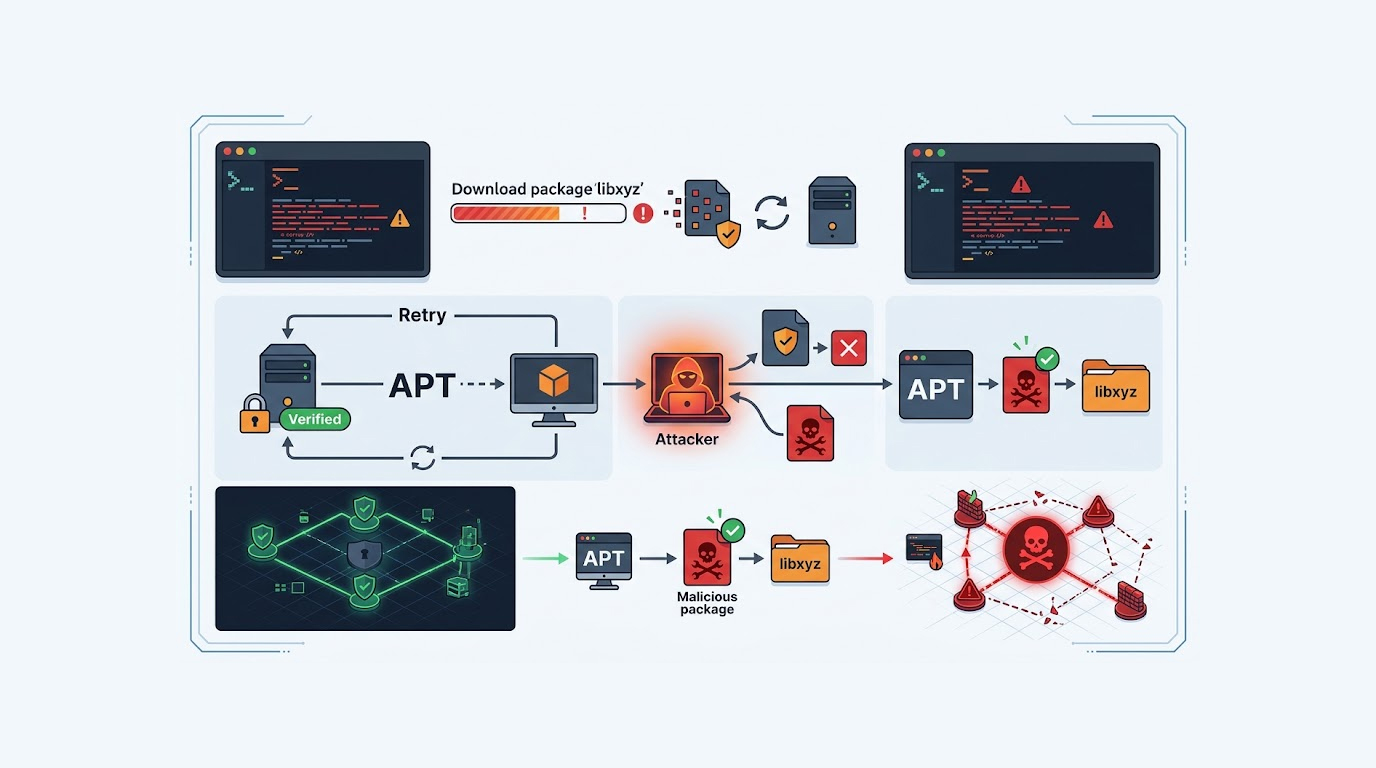
A package manager is supposed to be the trust anchor of a Linux system. It verifies signatures, checks hashes, and refuses to install anything that does no...
Found 21 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A package manager is supposed to be the trust anchor of a Linux system. It verifies signatures, checks hashes, and refuses to install anything that does no...
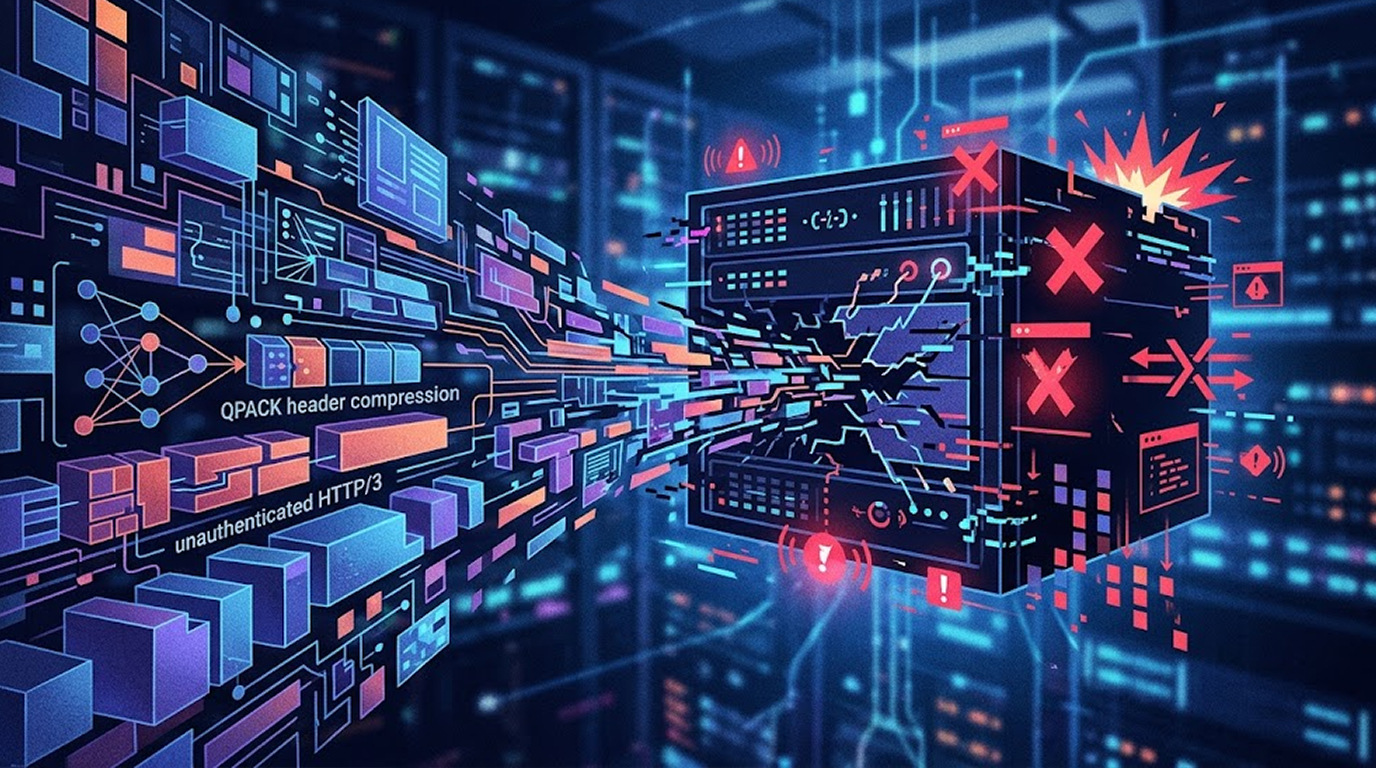
Your HTTP/3 web server might be one small packet away from a total crash, because security researchers at FoxIO just published a working proof-of-concept f...
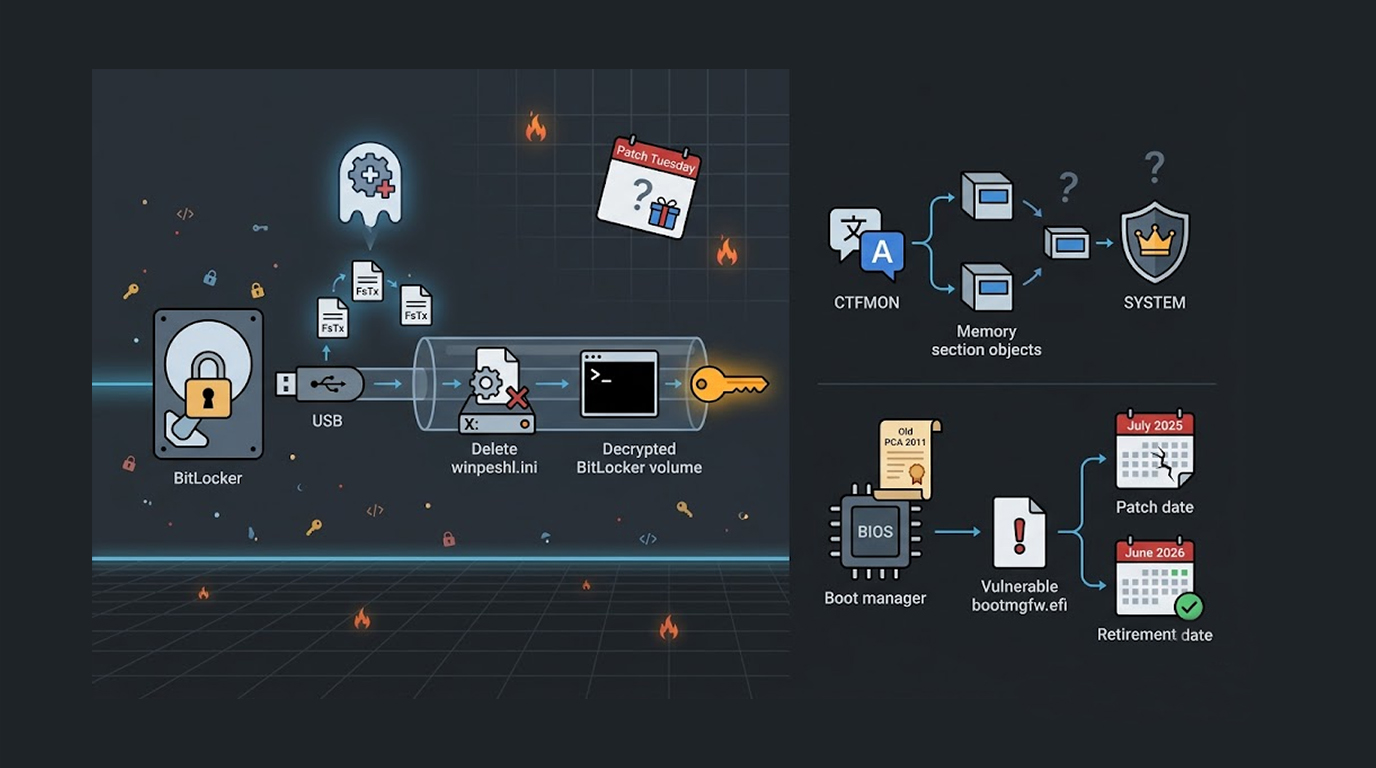
An anonymous security researcher who previously disclosed three Microsoft Defender zero-days is back with two more, and these new flaws affect BitLocker an...
Automated vulnerability scanners (OpenVAS, Nessus, Qualys, Nuclei, Nikto, sqlmap, etc.) are incredibly powerful, they scan fast, find thousands of potentia...
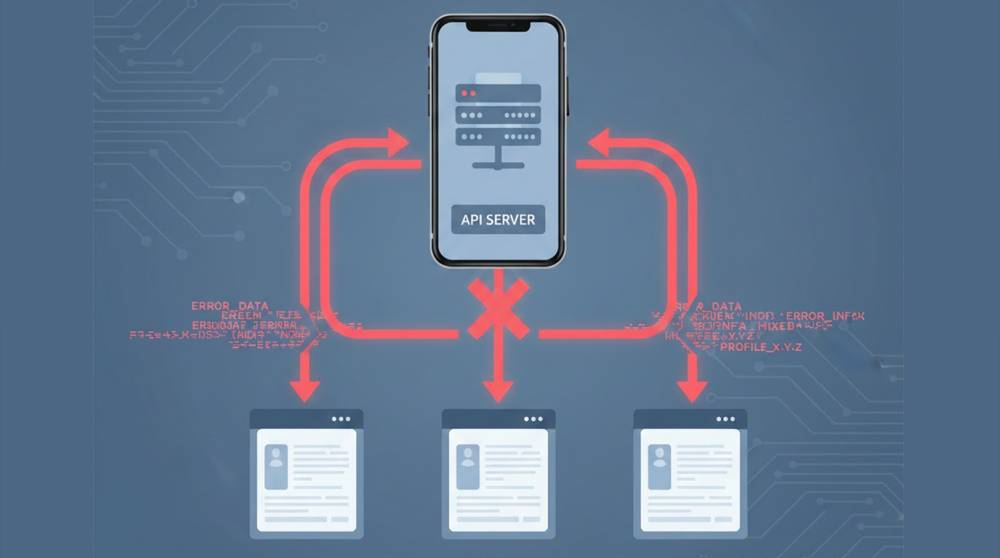
The mobile app wasn’t hacked.The API was trusted too much.That trust exposed user data—quietly, consistently, and at scale.This is one of the m...
Modern mobile apps are mostly UI.The real logic lives in:1. APIs2. Backend services3. Third party integrationsAttackers rarely attack the app itself.They a...
High severity vulnerabilities in 2026 are rarely exotic.Most incidents still come from:1. Simple trust assumptions2. Unsafe defaults3. Overexposed internal...
Network segmentation limits lateral movement, so if one system is compromised, attackers cannot freely roam.Weak or inconsistent segmentation is common. Ev...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067