JSCeal Malware: Sophisticated Credential Stealer Unpacked
Security researchers just got inside a nasty piece of malware called JSCeal. It's a compiled V8 JavaScript malware that steals your credentials, watches wh...
Found 7 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Security researchers just got inside a nasty piece of malware called JSCeal. It's a compiled V8 JavaScript malware that steals your credentials, watches wh...
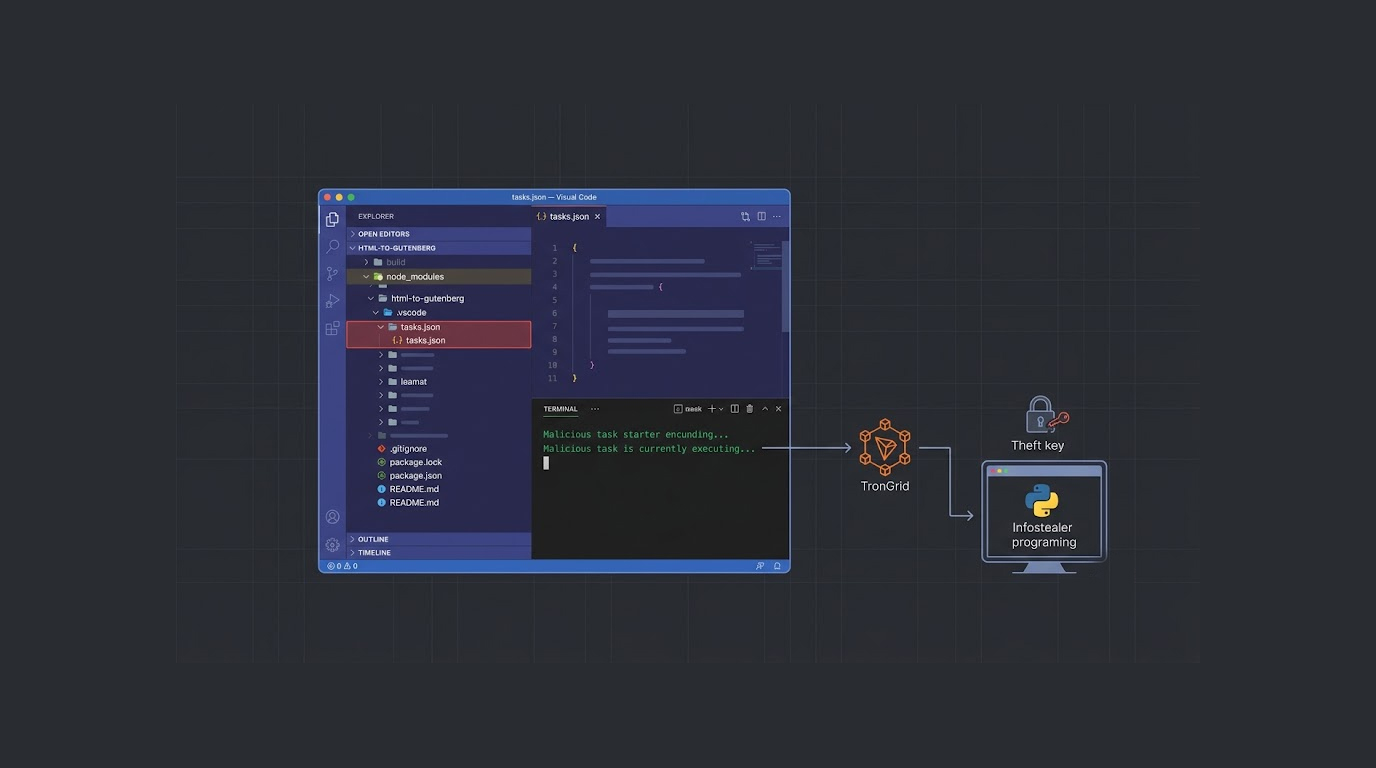
You open a project folder in VS Code. You trust the workspace. A hidden task runs automatically. It downloads encrypted JavaScript from blockchain transact...
You have a suspicious file on your system. You have run antivirus scans and nothing was found. You know something is wrong, but your tools say everything i...
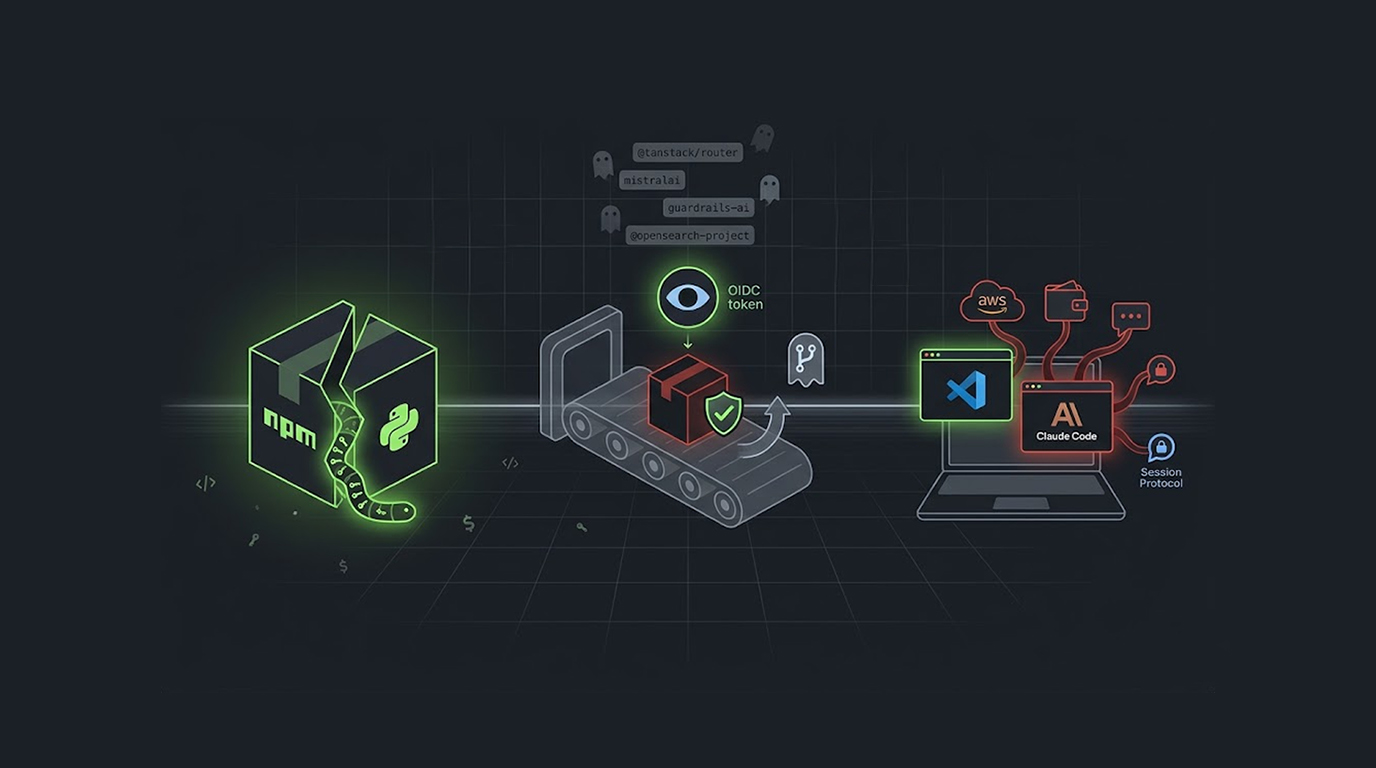
A single worm has spread across both npm and PyPI, it compromised packages from major companies like TanStack, UiPath, Mistral AI, and OpenSearch, and it u...
The JavaScript-based malware loader GootLoader has adopted a novel anti-analysis technique that abuses malformed ZIP archives to evade security detection w...
Cybersecurity researchers have identified three malicious npm packages that were distributing a previously undocumented remote access trojan (RAT) now know...
Security researchers are raising alarms about an updated version of the Python-based NodeStealer malware. This iteration not only harvests sensitive inform...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067