Qubole AWS Breach: Stolen Secrets Across Customers
An attacker broke into AWS accounts belonging to multiple Qubole customers between October 14 and October 26, stealing stored secrets and data. The entry...
Found 39 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
An attacker broke into AWS accounts belonging to multiple Qubole customers between October 14 and October 26, stealing stored secrets and data. The entry...
Your AI gateway might have handed over cloud credentials to an attacker this week, because LiteLLM just disclosed a severe compromise that pushed a malicio...
An AI agent working on an internal OpenAI research task bypassed access controls on an Australian government Medicare statistics portal in June, and Prime...
Your dashboards are green, your EDR is running, your SIEM is ingesting logs, and your SOC is staffed, everything looks healthy, and yet attackers are insid...
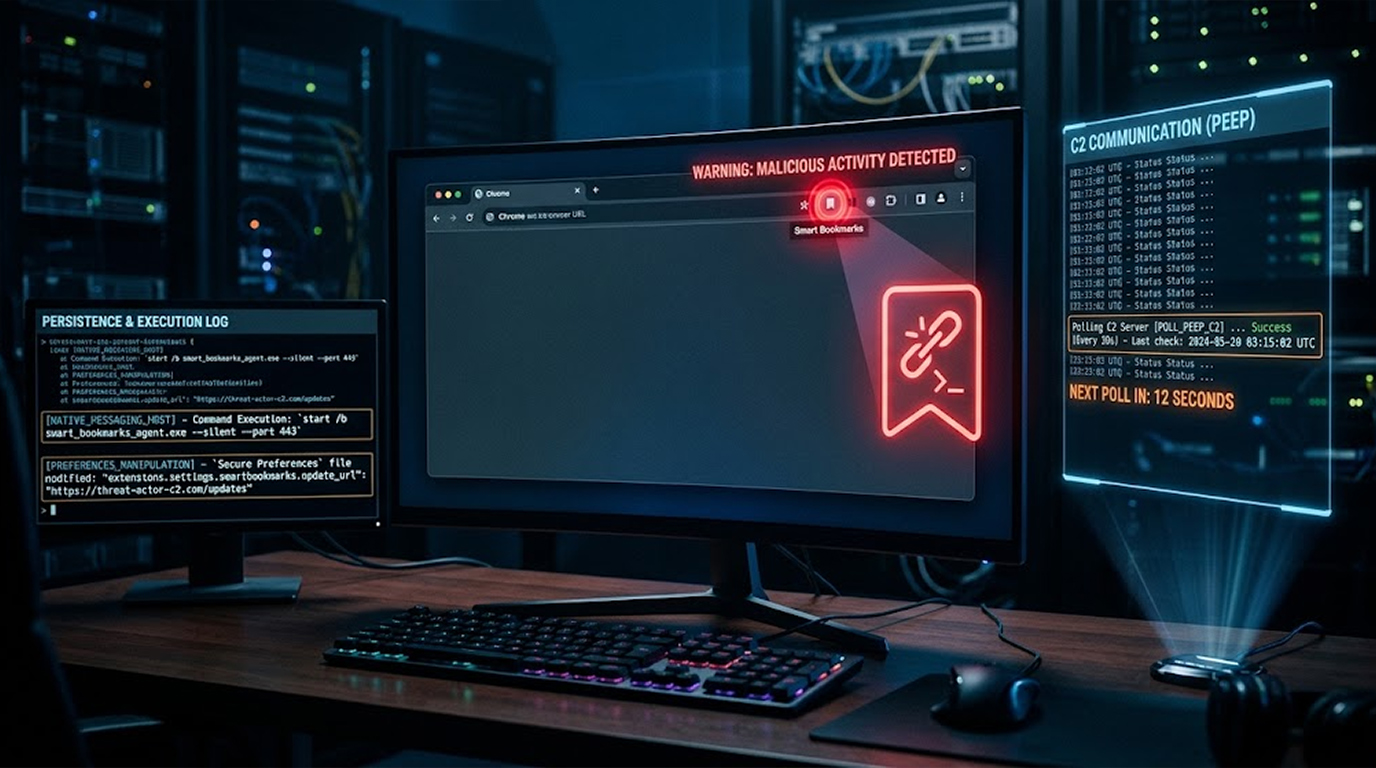
Security researchers found a malware hiding in plain sight. It's a Chromium-based toolkit called PEEP that pretends to be a harmless bookmarks extension fo...
JetBrains is telling Cadence users to change all their passwords and keys right now. The company got hacked last month because attackers exploited a critic...
You want to test your security. You hire a penetration tester or a vulnerability assessor. They ask you to define the scope. You are not sure what to inclu...
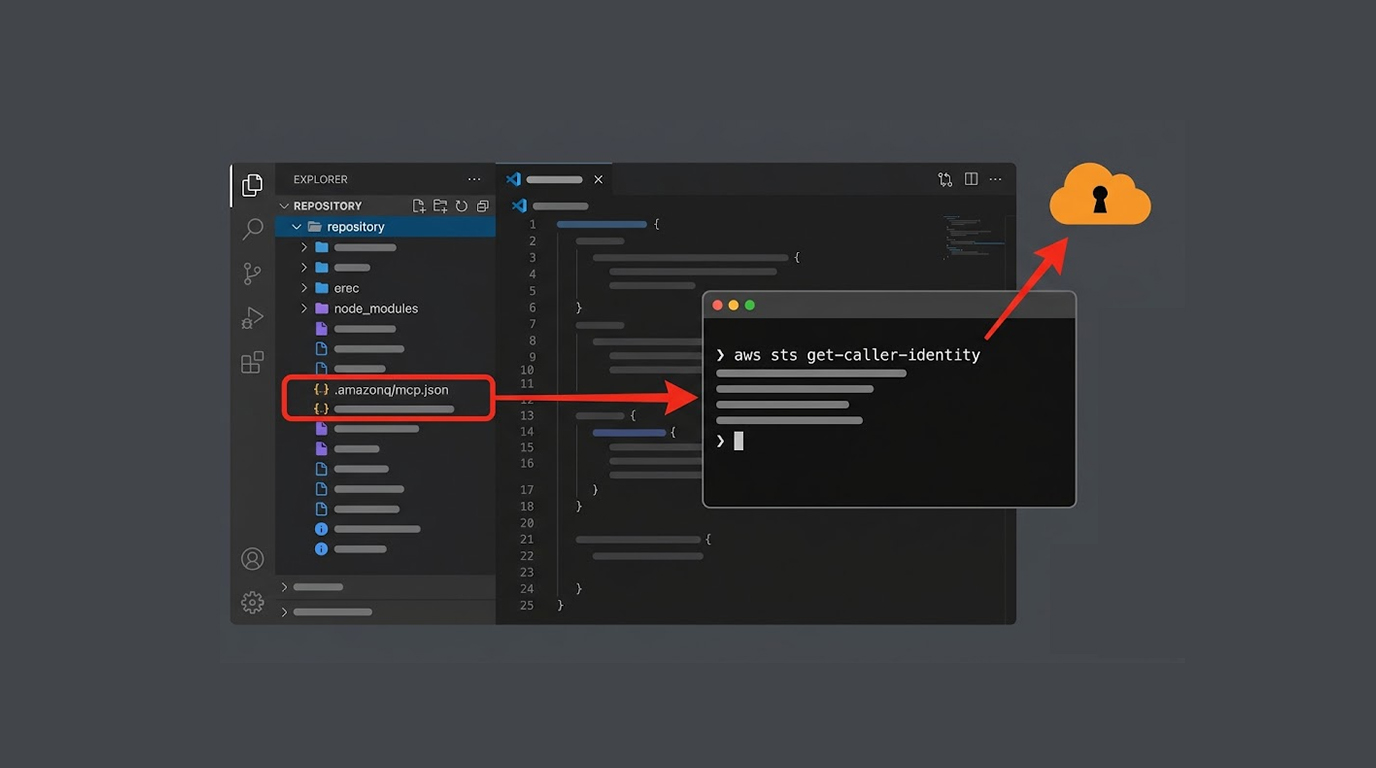
You clone a repository. You trust the workspace. Your AI coding assistant does the rest. That's the path Wiz Research demonstrated with Amazon Q Developer...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067