ChocoPoC Malware Targets Researchers via Fake Exploits
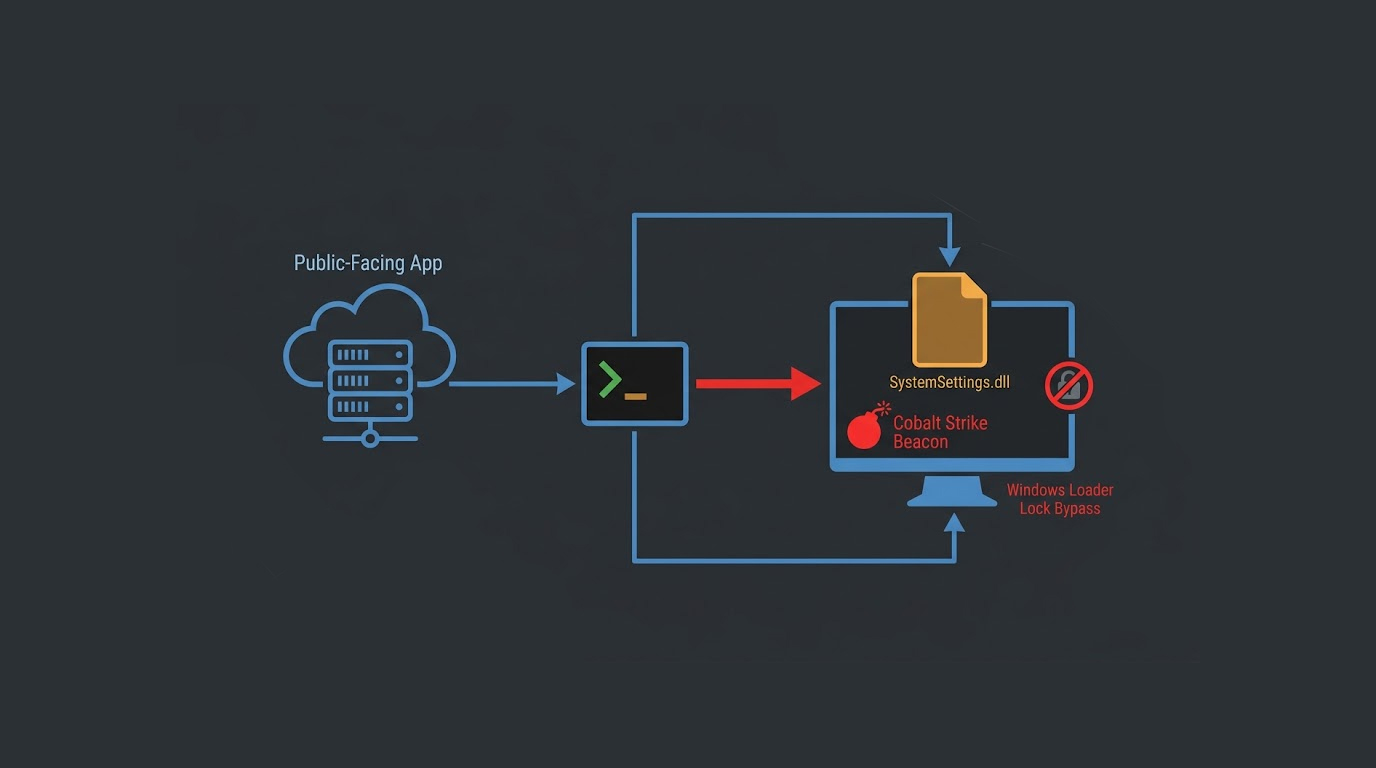
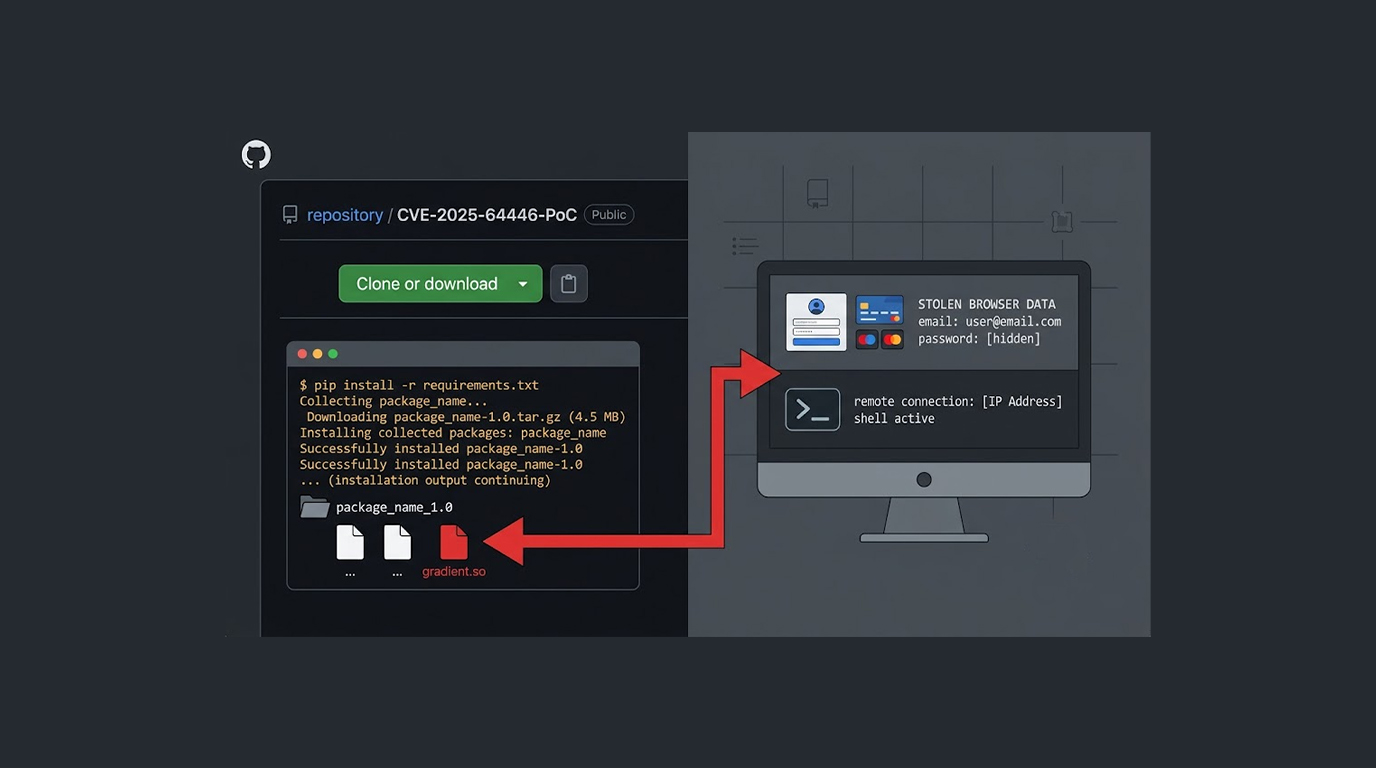
There's a new twist in the ongoing battle between researchers and attackers. Malicious actors are now planting data-stealing malware inside proof-of-concep...
Found 9 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There's a new twist in the ongoing battle between researchers and attackers. Malicious actors are now planting data-stealing malware inside proof-of-concep...
This new wave of attacks includes an unknown variant of malware known as SharkLoader. SharkLoader functions as a loader for distributing Cobalt Strike Beac...
A critical (CVSS = 9.8) security vulnerability has been found in React Server Components (versions 19.0.0-19.2.0), with the ability for an attacker to exec...
Modern software applications continue to fuel a significant increase in zero-day vulnerabilities and their associated exploitation. Zero-day vulnerabilitie...
Flare, a cybersecurity company, announced a new type of large-scale initiative -- the PCPcat campaign -- which is a worm-like cyberattack that will exploit...
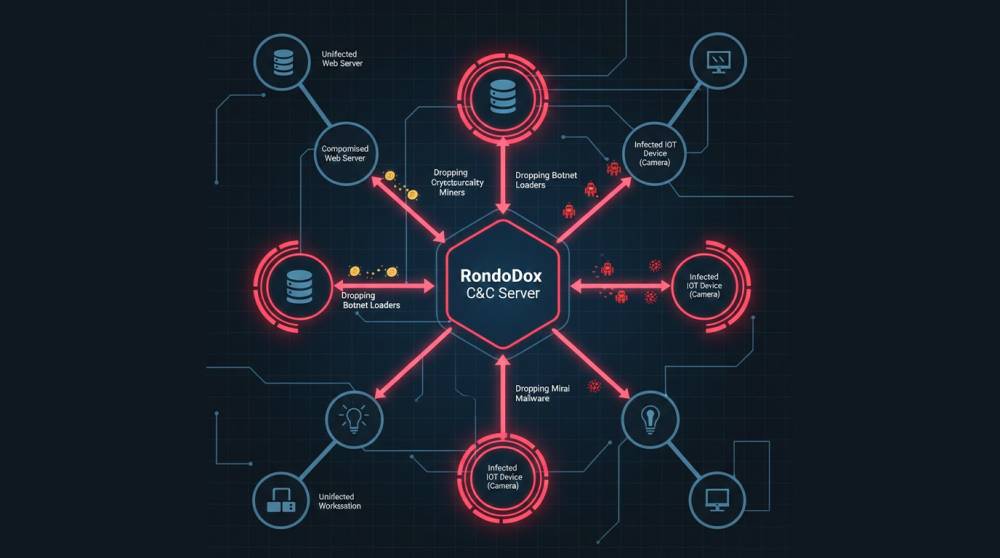
An analysis conducted by Cybersecurity experts has revealed that there is a nine-month continuity for the exploitation of many Internet of Things (IoT) dev...
Security teams are now seeing real-world exploitation of the React2Shell vulnerability to deliver advanced Linux malware, including KSwapDoor and ZnDoor, a...
The React team has shipped another round of security fixes, this time addressing two new weaknesses in React Server Components (RSC) that could allow denia...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067