PetitPotam Attack: Coercion, Relay, and Domain Takeover
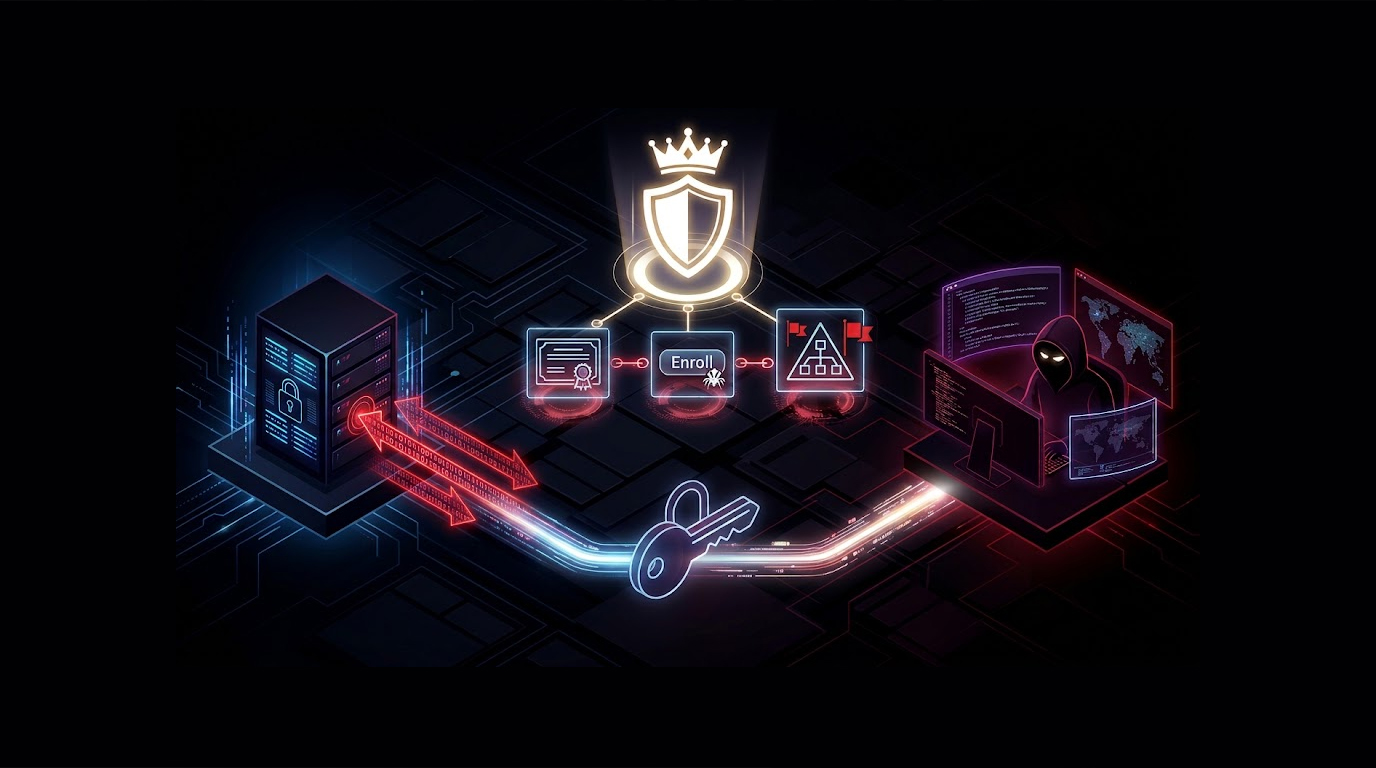
Most Active Directory attacks require credentials, which means the attacker has to steal something first, and that theft is the hard part that gets them ca...
Found 46 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Most Active Directory attacks require credentials, which means the attacker has to steal something first, and that theft is the hard part that gets them ca...
No zero-day. No malware-laced attachment. No exploit chain worth a conference talk. Microsoft just published an investigation into two intrusions where th...
Two days. That's all it took. SonicWall disclosed CVE-2026-15409 on July 14, 2026. By July 16, someone was already scanning for vulnerable appliances at sc...
Most security teams are drowning in work. There are applications to test, compliance deadlines to hit, and a never-ending stream of vulnerabilities to chas...
Cybersecurity researchers have found that the Cavern command and control framework set continues to evolve. The toolkit is used by Iranian nation-sta...
Picture this. You check into a hotel, connect to the Wi-Fi, and see a browser update prompt. It looks legitimate. You click it, install the update, and go...
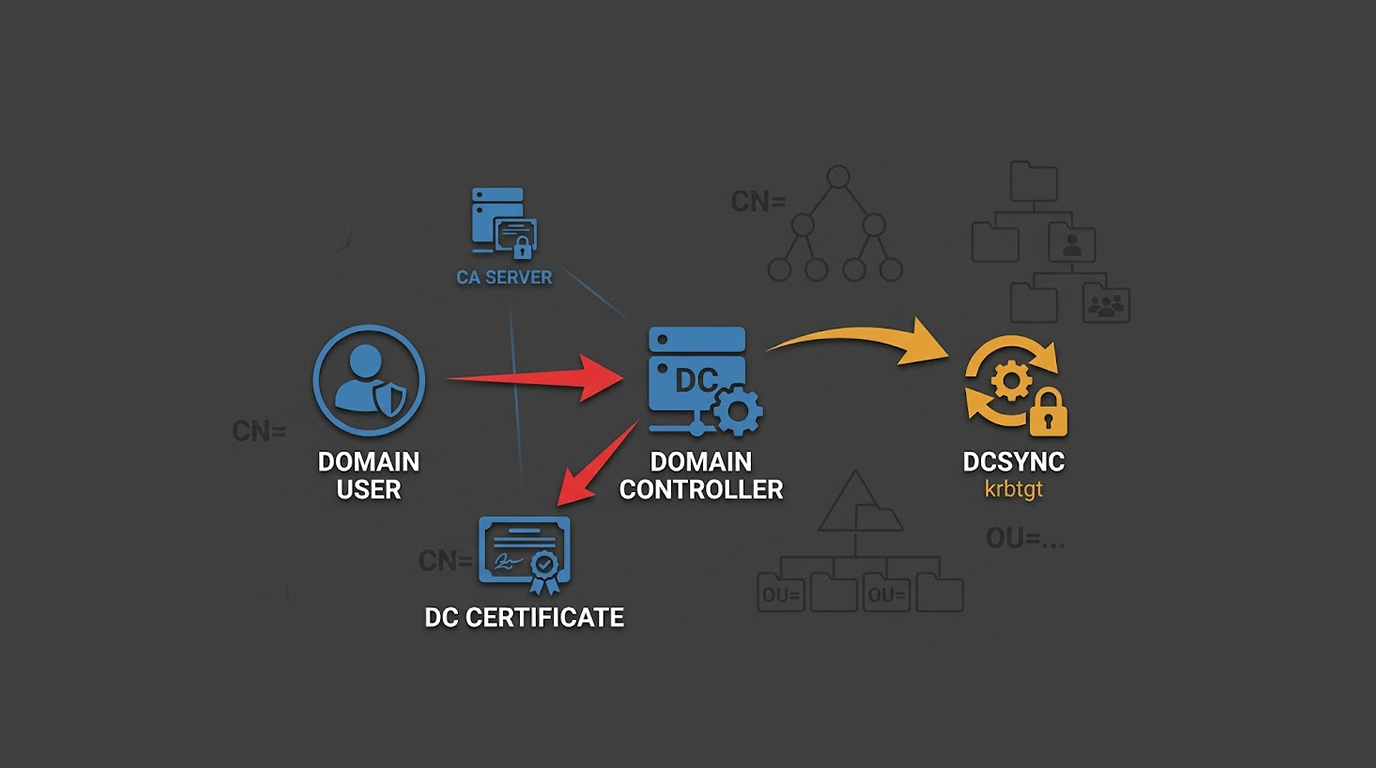
Let me paint you a picture. A regular employee with basic domain user privileges, no admin rights, no special access can walk away with a certificate that...
You want to test your security. You hire a penetration tester or a vulnerability assessor. They ask you to define the scope. You are not sure what to inclu...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067