Check Point Gateway: PHP2Shell to Root to Wiper
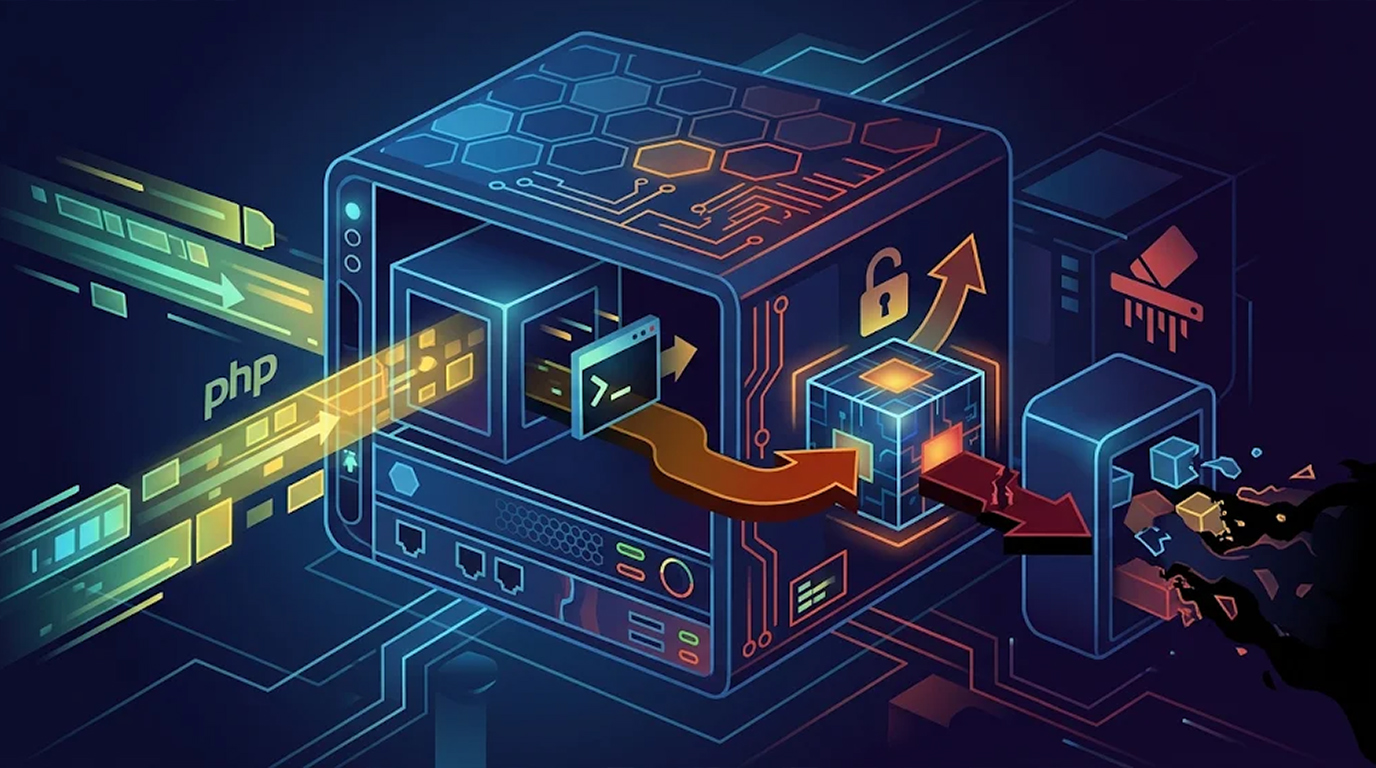
Check Point published an incident report this week that reads like a chain-of-custody document, and the chain has five links. Initial access through PHP2Sh...
Found 76 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Check Point published an incident report this week that reads like a chain-of-custody document, and the chain has five links. Initial access through PHP2Sh...
Apache released version 2.4.71 yesterday, and the reason is CVE-2026-119618, a critical flaw in the HTTP/2 module that allows a remote attacker to run code...
Two researchers took over the login systems behind two car brands' mobile apps, and from there they unlocked doors and started engines. The entry point wa...
Nine hundred and forty-eight working local privilege escalation exploits. That is the number OpenAI published on Wednesday, and it came from a single mid-O...
The mental image most people still carry of a DDoS attack is a wall of traffic, a graph that goes vertical, and a site that falls over because the pipe fil...
Every engineering team has a version of the same message in their incident channel, which is a screenshot of an error, a timestamp, and the words "it crash...
You see the advisory, you see the severity rating, and you think you understand the risk, and then you patch it and move on, and that is where most people...
Most site owners think they know their PHP version, because they ran php -v once, saw a number, and assumed that was the answer. It usually is not the ans...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067