The 24 Hours Before a Breach Seen in Security Logs
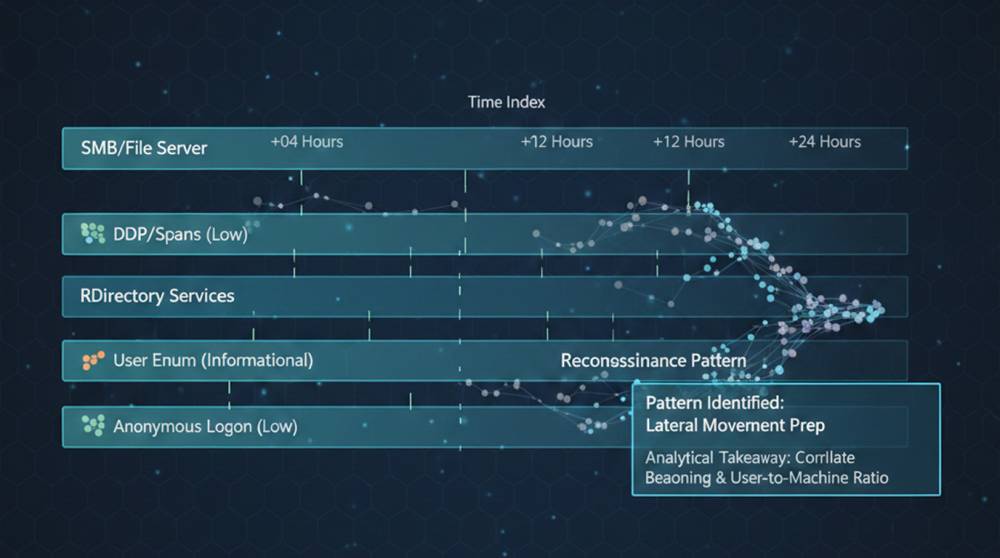
Most breaches don’t begin with malware detonating everywhere.They begin quietly.Someone logs in.They look around.They test limits.If you replay the l...
Expert analysis, threat intelligence, and practical guidance from Red Secure Tech's security specialists — covering penetration testing, vulnerability assessment, incident response, and secure development for UK businesses.
Most breaches don’t begin with malware detonating everywhere.They begin quietly.Someone logs in.They look around.They test limits.If you replay the logs from the day before a breach, the signs a...
Read Full ArticleMost breaches don’t begin with malware detonating everywhere.They begin quietly.Someone logs in.They look around.They test limits.If you replay the l...
Network reconnaissance isn’t loud, it doesn’t trip alarms or crash systems, it’s someone looking around carefully, touching many things a...
In critical infrastructure, IoT devices don’t just collect data.They open valves, regulate pressure, manage traffic, and balance power loads.These de...
The WordPress Quiz Maker plugin has been found to have a severe SQL injection vulnerability that could allow an unauthenticated attacker to retrieve sensit...
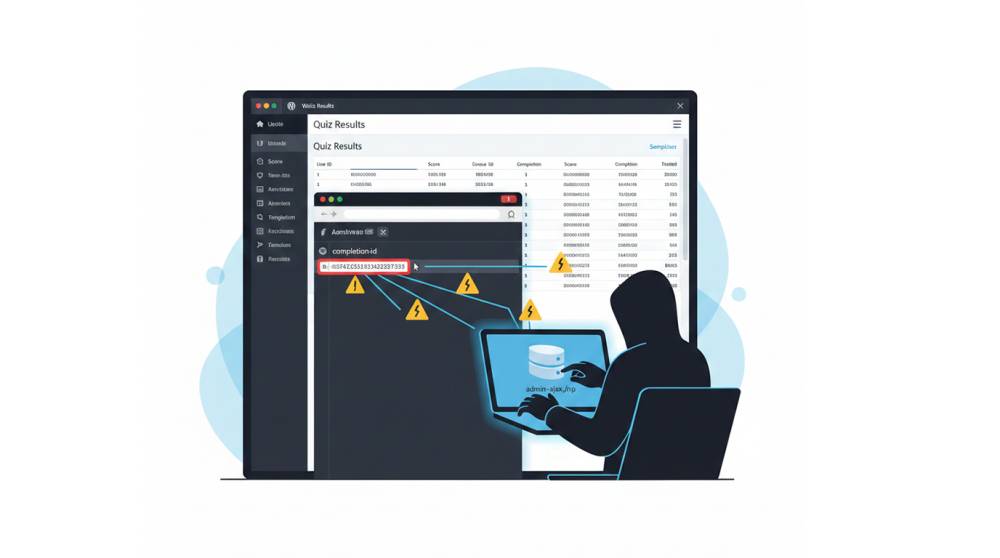
A serious authorization flaw has been discovered by security researchers in Chained Quiz WordPress plugin that allows attackers to change others’ qui...
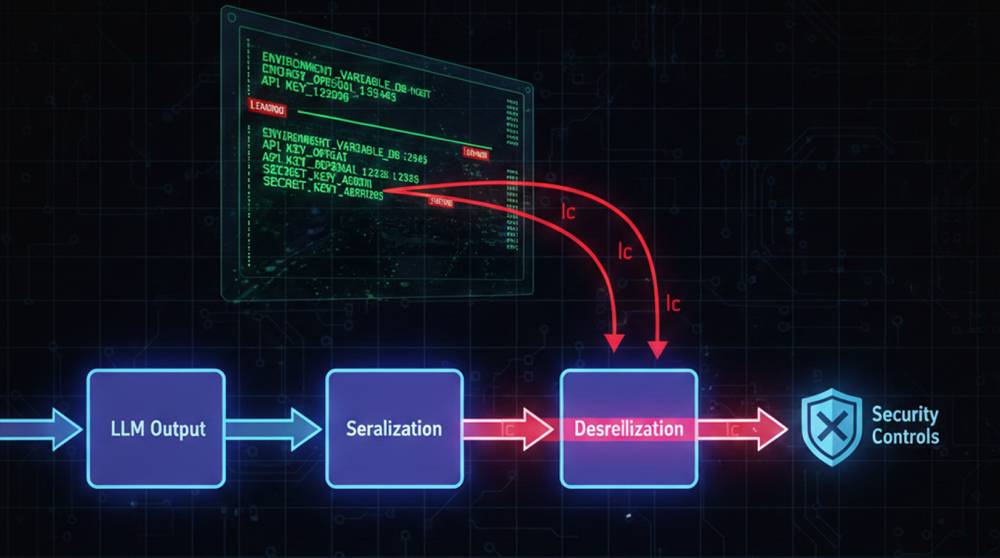
Security researchers have discovered a serious flaw in LangChain Core that could be exploited by malicious users to access confidential secrets by manipula...
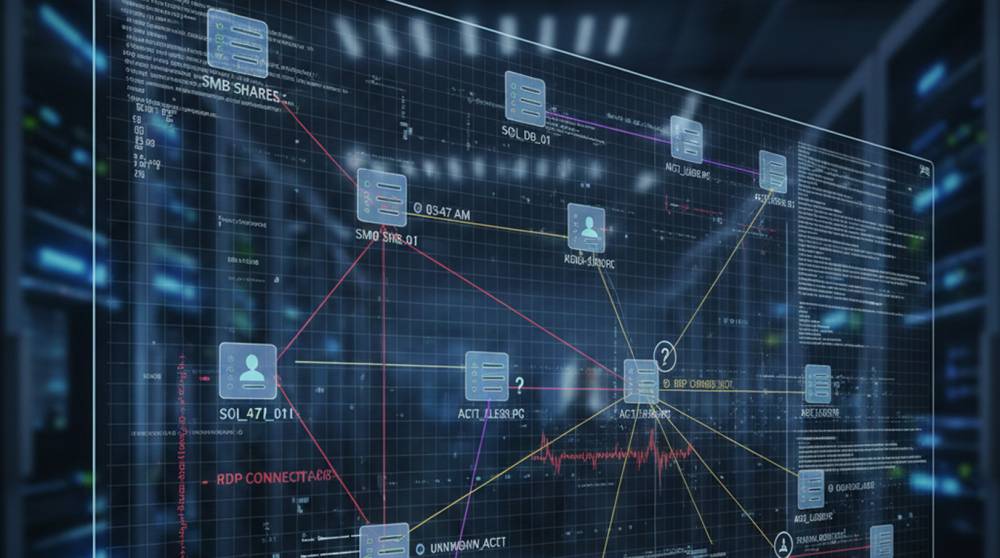
The Server Message Block (SMB) and Remote Desktop Protocol (RDP) are essential tools for the daily functioning of organizations. System Administrators use...
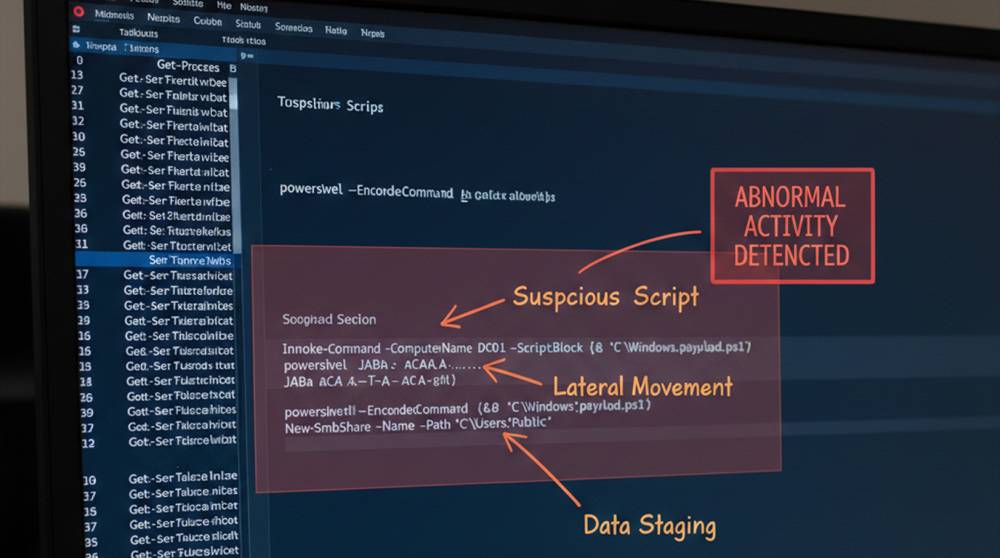
PowerShell is one of the most useful tools in a Windows environment.Admins rely on it daily. So do attackers.The challenge isn’t blocking PowerShell....
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Advanced adversary simulation testing your organisation's detection and response capabilities against real-world threat actor behaviour.
Actionable intelligence on threat actors, attack vectors, and emerging risks targeting your sector — enabling proactive defensive decisions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067