Apache HTTP/2 Flaw: CVE-2026-119618 RCE
Apache released version 2.4.71 yesterday, and the reason is CVE-2026-119618, a critical flaw in the HTTP/2 module that allows a remote attacker to run code...
Found 11 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Apache released version 2.4.71 yesterday, and the reason is CVE-2026-119618, a critical flaw in the HTTP/2 module that allows a remote attacker to run code...
If you run a BTCPay Server instance on an older version, your hot wallet funds may already be at risk. The project issued an urgent warning this week after...
VulnCheck has confirmed what every industrial security team was dreading. A maximum-severity vulnerability in Siemens SIMATIC IoT2050 Advanced devices is n...
Your Dell storage infrastructure might be wide open to attackers right now, because Dell just dropped a bombshell security advisory, revealing six critical...
Cisco just dropped patches for a critical security flaw affecting 10 of its Nexus 9000 switches. The vulnerability, tracked as CVE-2026-20212, allows attac...
Metabase has warned that a maximum-severity security flaw impacting its business intelligence and data visualization software has been exploited in the wil...
cPanel has released a targeted security update addressing a vulnerability that could let an authenticated hosting customer execute SQL in the database's ro...
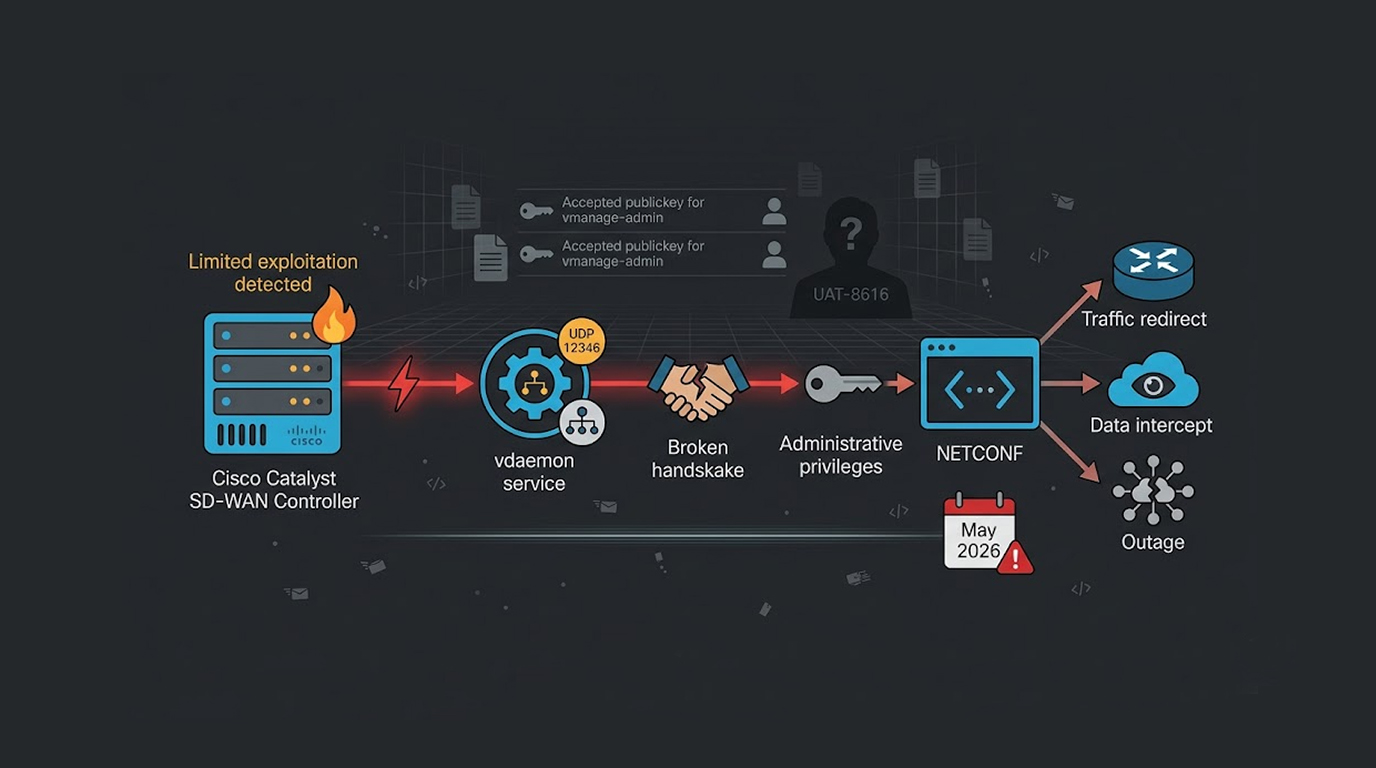
Cisco has released emergency updates for a critical vulnerability in its Catalyst SD-WAN Controller, and the flaw carries a CVSS score of 10.0 which is the...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067