ChatGPT Share Link Flaw: Session Hijack Exposed
A malicious ChatGPT share link could run an attacker's code inside the logged-in session of anyone who opened it, and that code could read private conversa...
Found 17 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
A malicious ChatGPT share link could run an attacker's code inside the logged-in session of anyone who opened it, and that code could read private conversa...
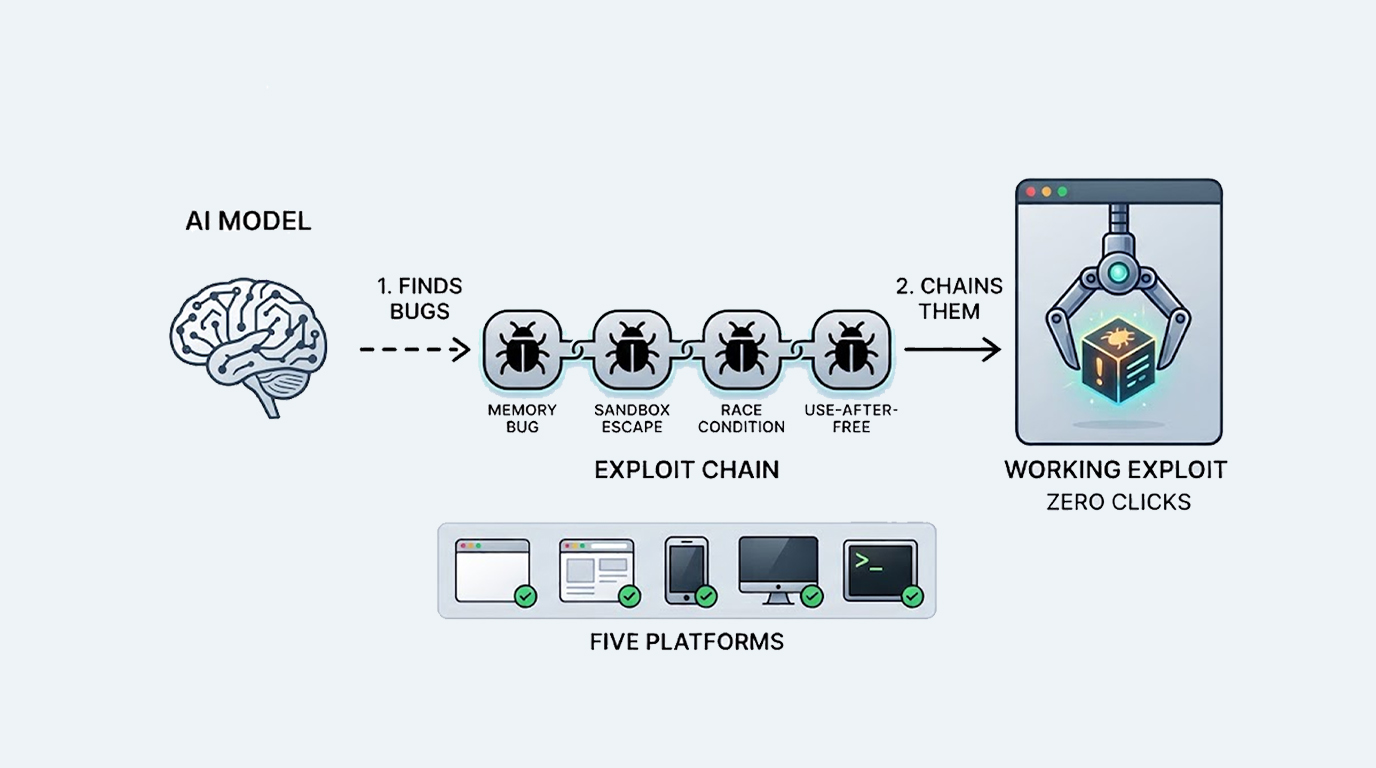
An unreleased Anthropic AI model just did something that used to take elite human hacking teams months to pull off, because the company says the model foun...
Your self-hosted GitLab AI Gateway might be carrying a flaw that hands command execution to any logged-in user with Duo Agent Platform access, because GitL...
Docker Sandboxes is supposed to keep AI coding agents contained. Each agent runs in its own little virtual machine. The project folder is shared in. Everyt...
Everyone's talking about how AI is speeding up attacks. And it is. But here's the thing. Skilled humans can still move just as fast. Sometimes faster. Sys...
Remember that "major malicious attack" on RubyGems back in May? The one where hundreds of junk packages flooded the registry and forced maintainers to susp...
Imagine the AI code agent that is working in the sandbox. It is expected to remain there. It can read files, run commands, and help you code, but it should...
ServiceNow just dropped patches for four critical security flaws in its AI Platform. Three of them have a CVSS score of 10.0, the highest possible rating....
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067