Was the Malware Sample Planted to Mislead You?
There's a question that arrives at some point in almost every serious investigation, usually late at night, and it goes something like this, which is that...
Found 12 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There's a question that arrives at some point in almost every serious investigation, usually late at night, and it goes something like this, which is that...
You have heard the terms. Red team attacks. Blue team defends. But when you look at the actual commands, what is the difference? The answer is not the too...
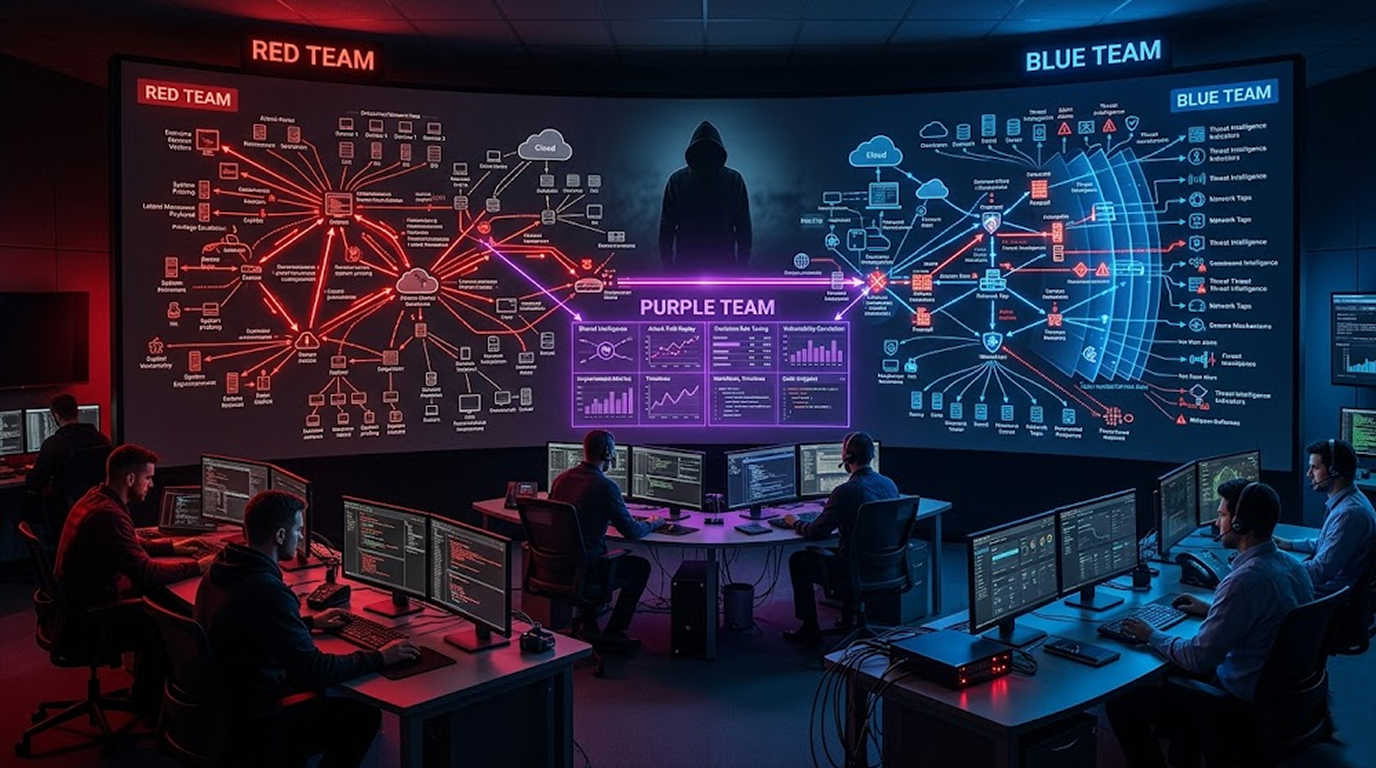
You have heard the terms thrown around at security conferences and in vendor pitches. Red team finds vulnerabilities. Blue team defends. Purple team does b...
You run a vulnerability scan. You fix the critical findings. You feel safe.Then a real attacker breaks in through a phishing email your security team never...
Atomic Red Team is an open-source library of small, focused tests mapped to the MITRE ATT&CK framework. These tests simulate real adversary behaviors t...
Many traditional red team exercises are ineffective for a single reason: they focus on testing types of attack instead of the detection effectiveness. ...
Advanced attacks rarely fail because an exploit did not work.They fail because something felt wrong.APT groups succeed by blending into normal operations.G...
Metasploit results are usually clear to security teams.They are rarely clear to executives.Screenshots show shells, sessions, and exploits.Executives hear...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067