Detecting a Vendor Breach From Your Own Logs
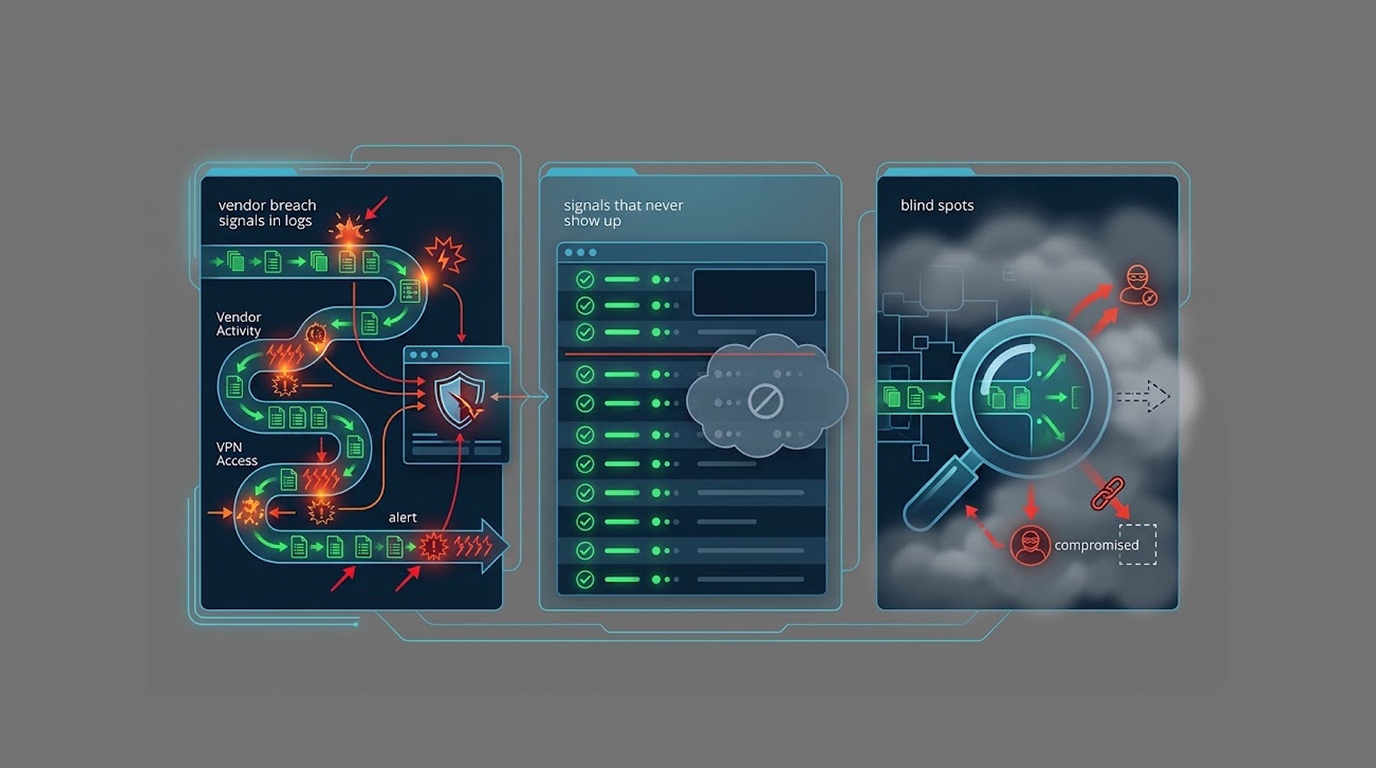
When a vendor gets breached, the first thing most organizations discover is that they have almost no visibility into what happened, because the compromised...
Found 134 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
When a vendor gets breached, the first thing most organizations discover is that they have almost no visibility into what happened, because the compromised...
A spear-phishing email arrives. It looks like a routine message from a trusted sender, and it contains what appears to be an attachment preview, rendered e...
Microsoft has warned about phishing campaigns that distribute an installer for MSP360 Remote Monitoring and Management software, and the lures are the usua...
Threat actors have found a new way to turn a trusted platform into a malware delivery system, and this time they are using ChatGPT Custom GPTs to disguise...
There is an email sitting in a university researcher's inbox right now. It looks like a research proposal, or a conference invitation, or a document from a...
For twenty years, email security worked on a simple assumption, if a thousand people received the same malicious email, you only needed to catch it once, b...
You get an email from your CEO, it looks completely normal, the tone is right, the signature is right, and it references a real project you have been worki...
You receive a phone call. The voice on the other end sounds exactly like your grandson. He is scared. He says he is in trouble and needs money fast. You pa...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067