AI Malware Distribution: How Attacks Get Faster and Stealthier
There was a time when malware distribution had a rhythm. A campaign would appear, it would spread for a few weeks, defenders would write signatures, and th...
Found 28 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
There was a time when malware distribution had a rhythm. A campaign would appear, it would spread for a few weeks, defenders would write signatures, and th...
Every week brings a headline about a new malware family, a new name, a new logo, a new dashboard on some leak site, and it is easy to get pulled into chasi...
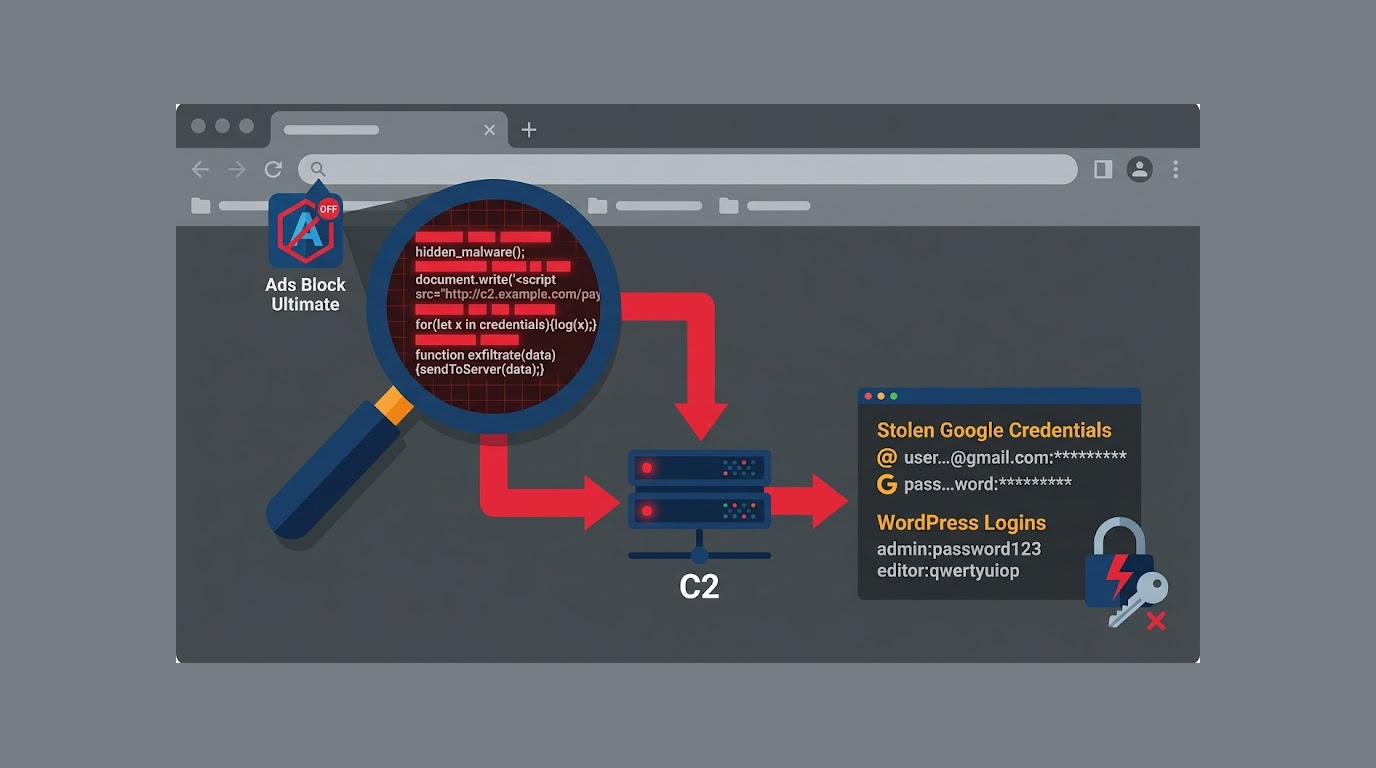
You install an ad blocker. It blocks ads. It has good reviews. You forget about it. For years, it sat quietly in your browser. Then one day, it woke up. I...
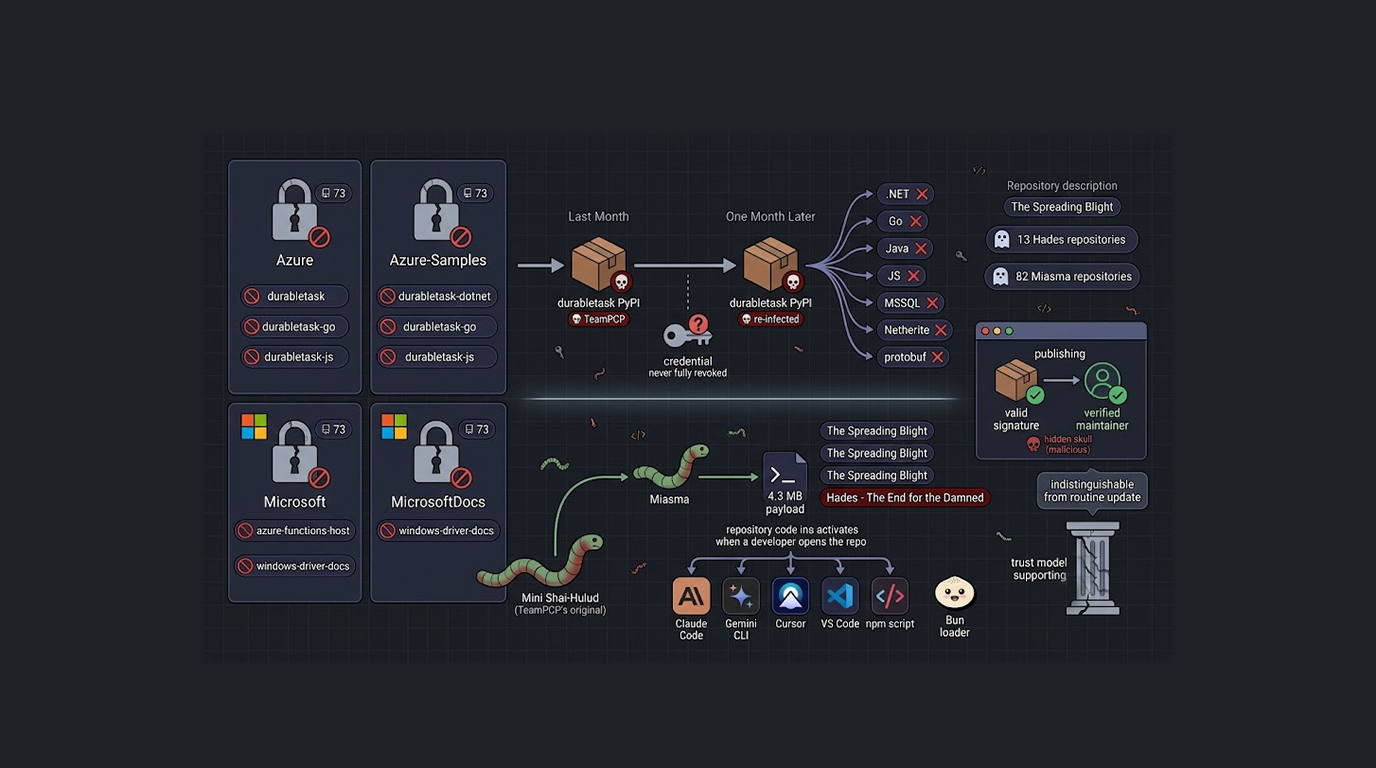
A recent Miasma self-replicating supply chain attack hit 73 different GitHub repositories owned by Microsoft in four different organizations: Azure, Azure...
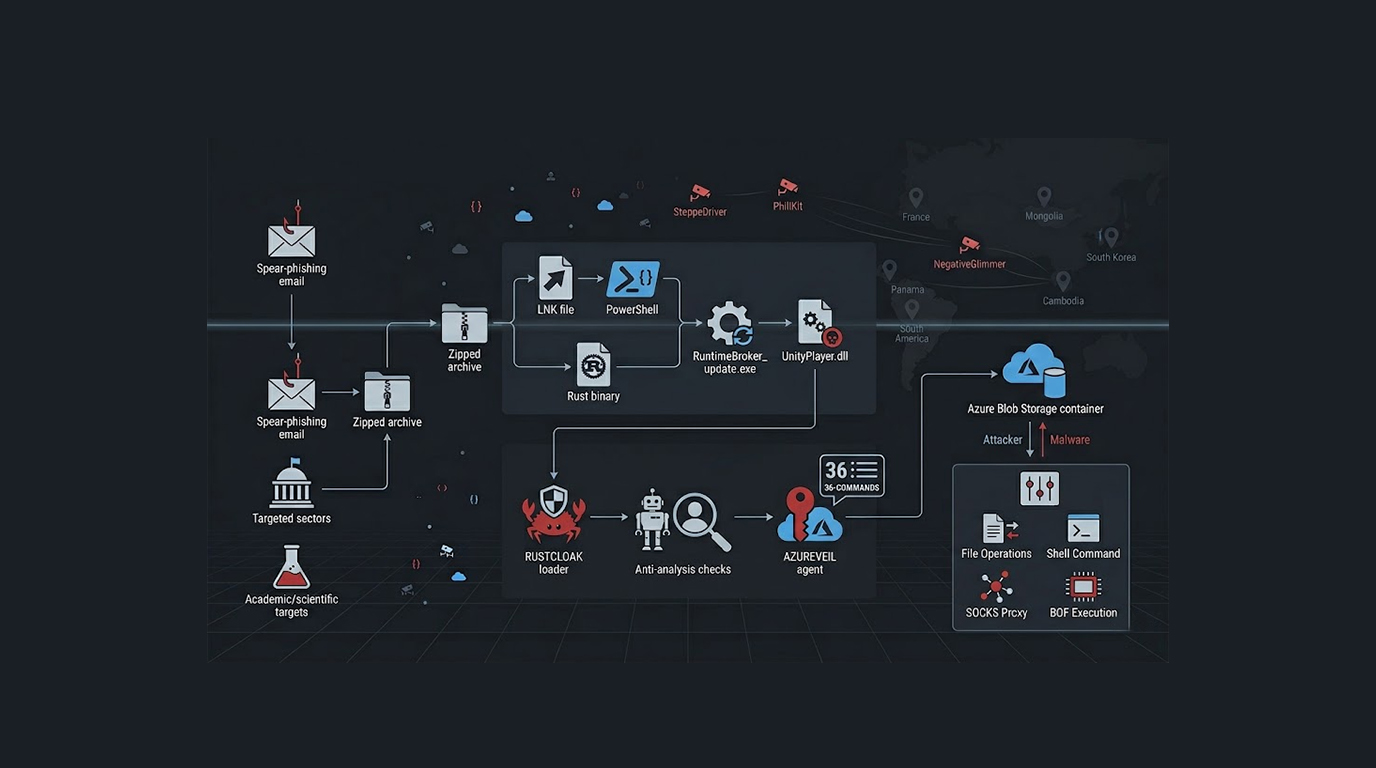
Officials and citizens in the Czech Republic and Taiwan have become victims of a new cyber espionage operation called Operation Dragon Weave. Attackers are...
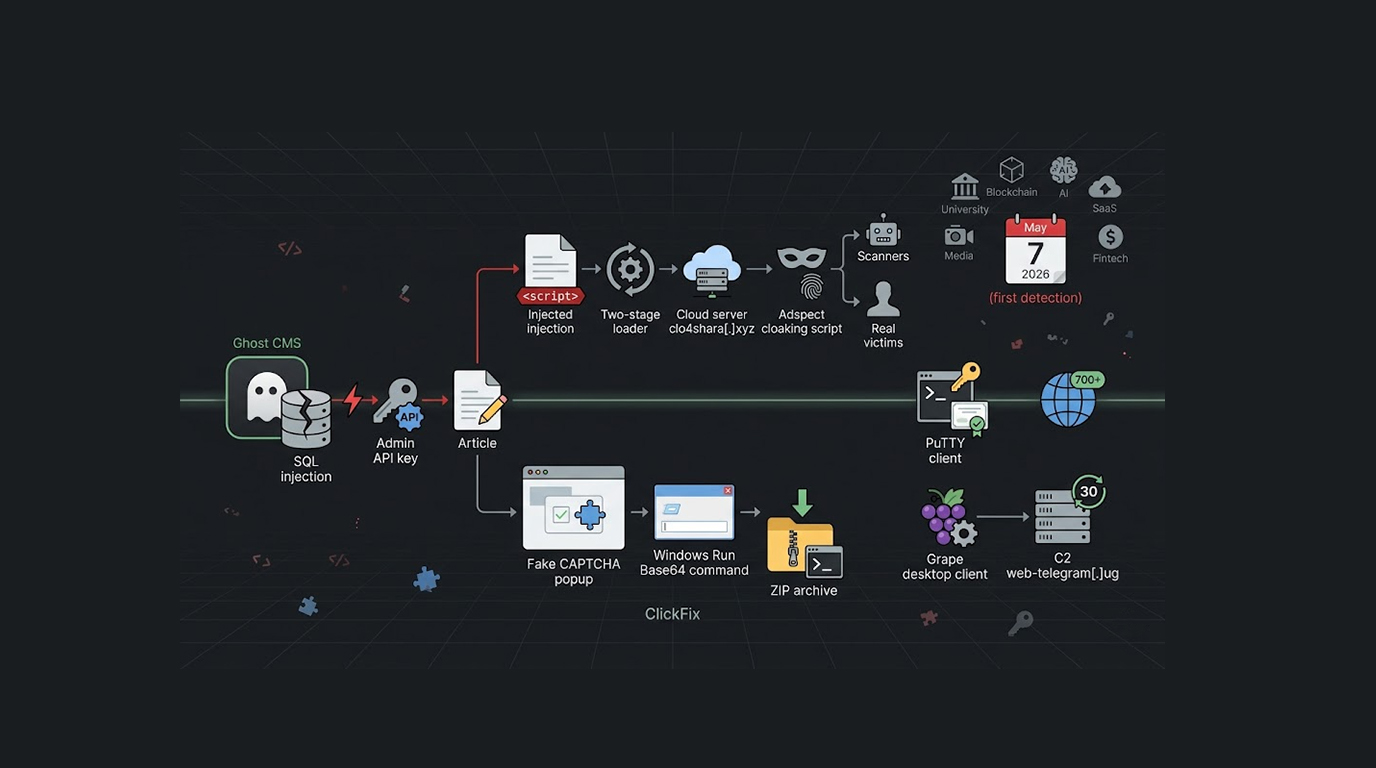
Threat actors took advantage of a critical SQL injection vulnerability present in Ghost CMS to insert malicious Javascript code into ClickFix campaigns lau...
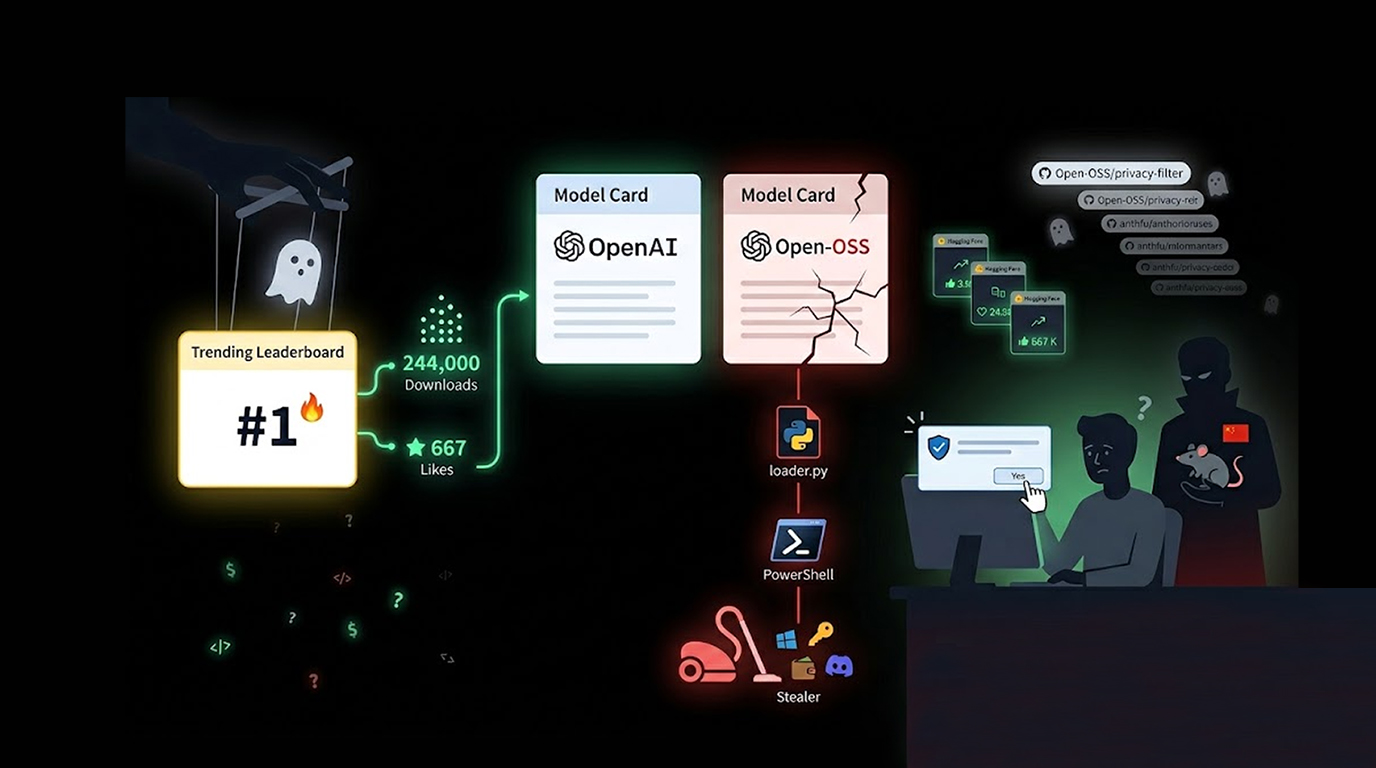
A malicious repository on Hugging Face ranked #1 on the platform by impersonating OpenAI's just-released Privacy Filter model while delivering a Rust-based...
You have run Cobalt Strike for years, it works, but it is also the most signatured tool on the market, every defender knows how to spot it Havoc is differ...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067