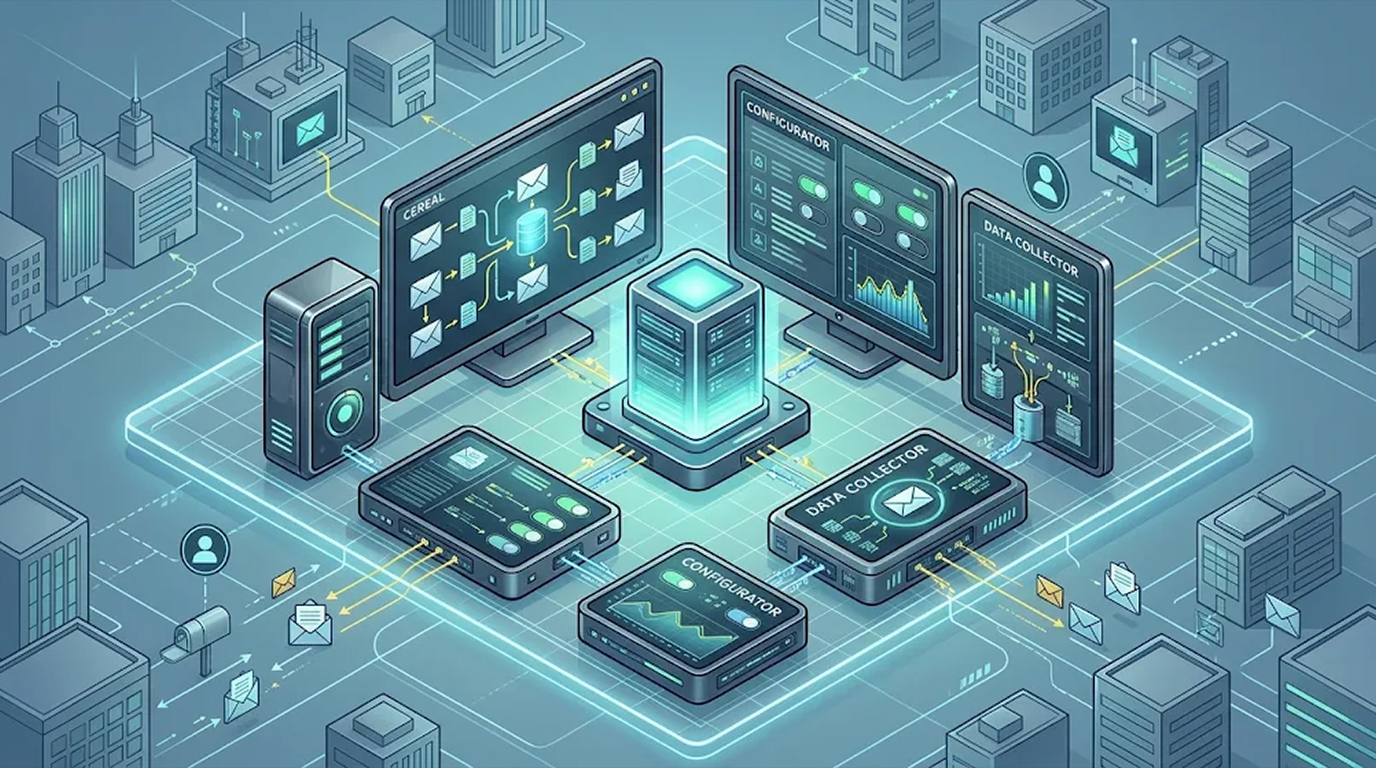
Cereal Espionage Toolset: Stealing Email From Exchange
Most breaches you read about are loud in the way that matters to defenders, because they involve ransomware, a leak site, a demand, and a countdown, and th...
Found 142 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Most breaches you read about are loud in the way that matters to defenders, because they involve ransomware, a leak site, a demand, and a countdown, and th...
Scoping sounds like the easy part of incident response, because you already know how to search a filesystem and you already know how to read an audit log,...
The mental image most people carry of state-sponsored espionage is a team of elite operators, custom zero-days, and infrastructure that costs more than a s...
No zero-day. No malware-laced attachment. No exploit chain worth a conference talk. Microsoft just published an investigation into two intrusions where th...
Most malware you read about wants files, which means documents, credentials, or customer records, and the damage gets measured in what was copied and how m...
Two incidents can look identical in the alert queue and be entirely different animals underneath, because one of them means somebody read data they shouldn...
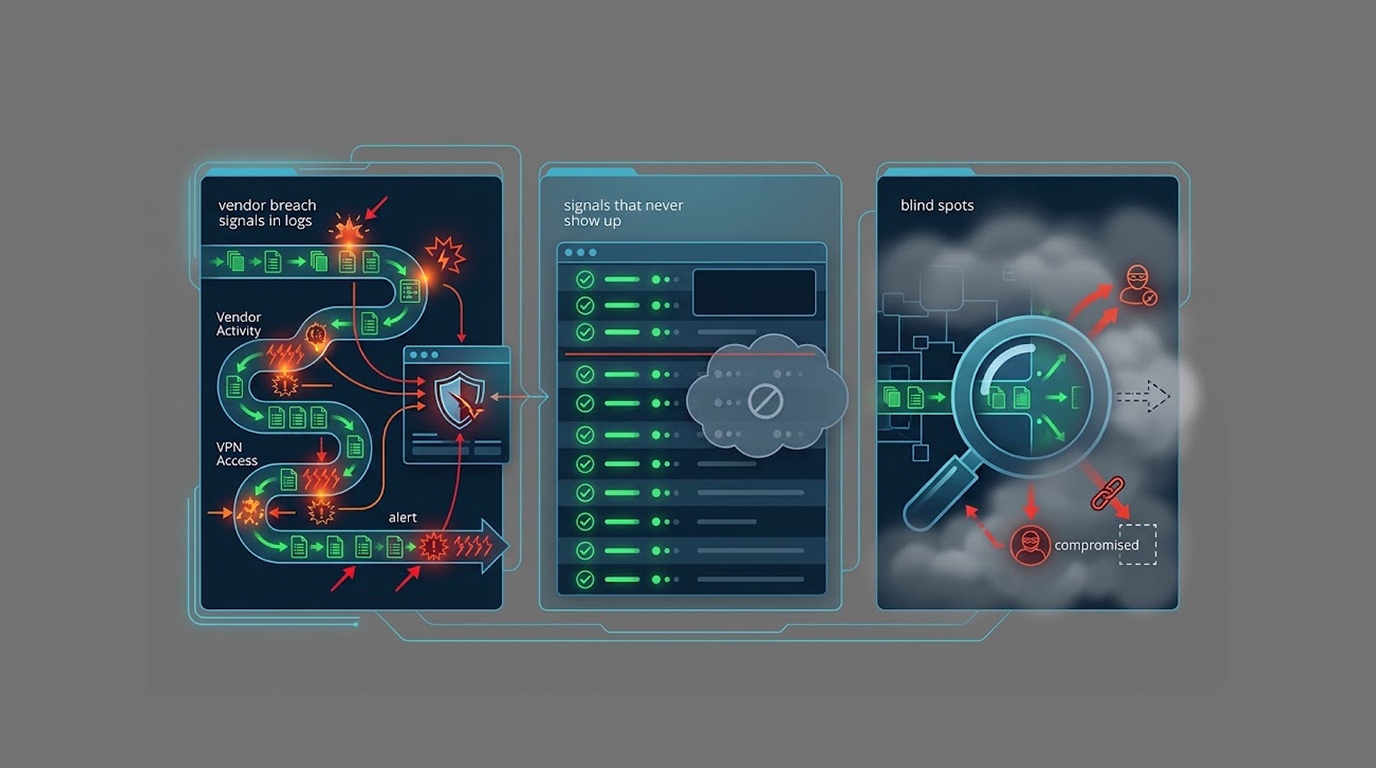
When a vendor gets breached, the first thing most organizations discover is that they have almost no visibility into what happened, because the compromised...
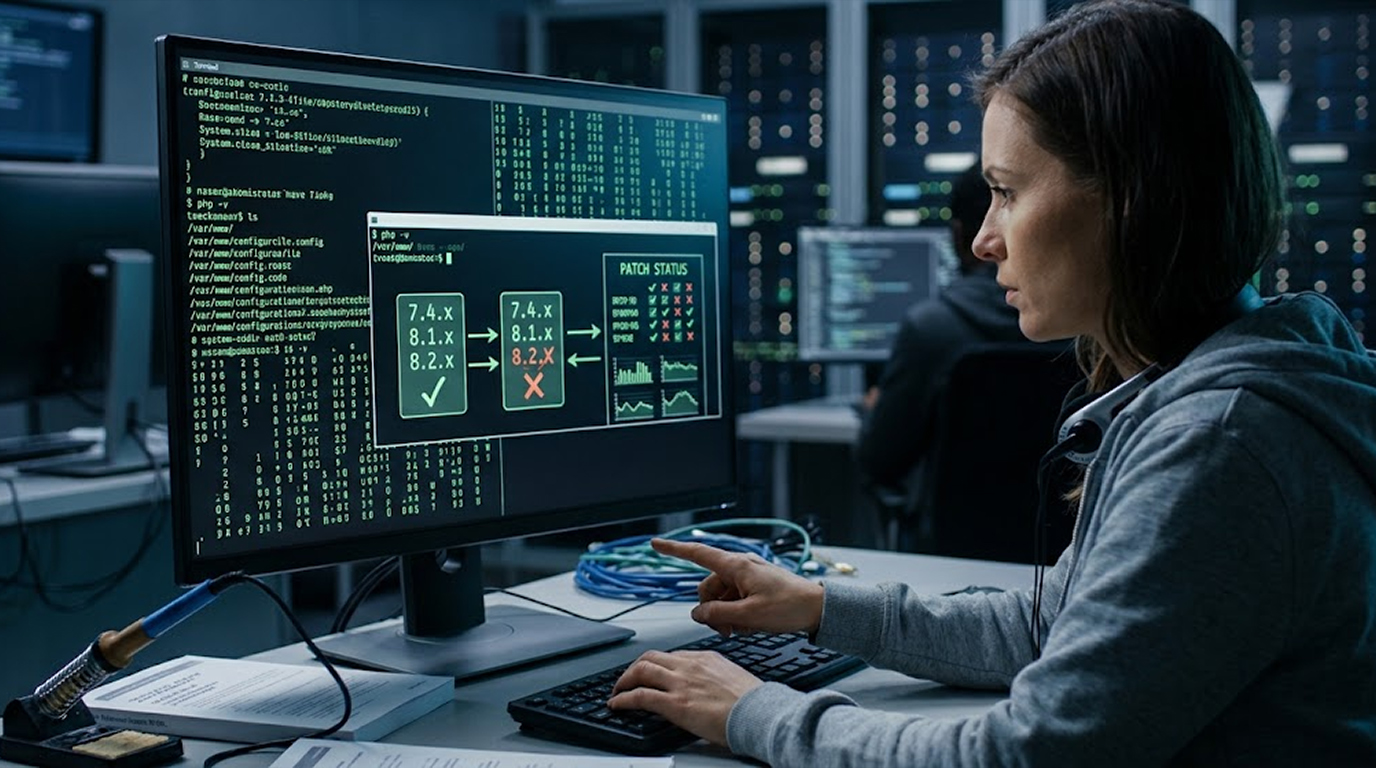
Most site owners think they know their PHP version, because they ran php -v once, saw a number, and assumed that was the answer. It usually is not the ans...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067