Fake Web3 Accelerator Pushes npm Malware at Founders
Your npm install might have handed a stranger your browser cookies, your wallet files, and a persistent backdoor, because researchers just documented a fak...
Found 27 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your npm install might have handed a stranger your browser cookies, your wallet files, and a persistent backdoor, because researchers just documented a fak...
Your endpoint detection and response tool is running. It is watching for malicious behavior. It is blocking known attacks. You feel protected. Then an att...
Qilin is not just another ransomware group. It is the most operationally active ransomware operation on the planet. And it has figured out how to use artif...
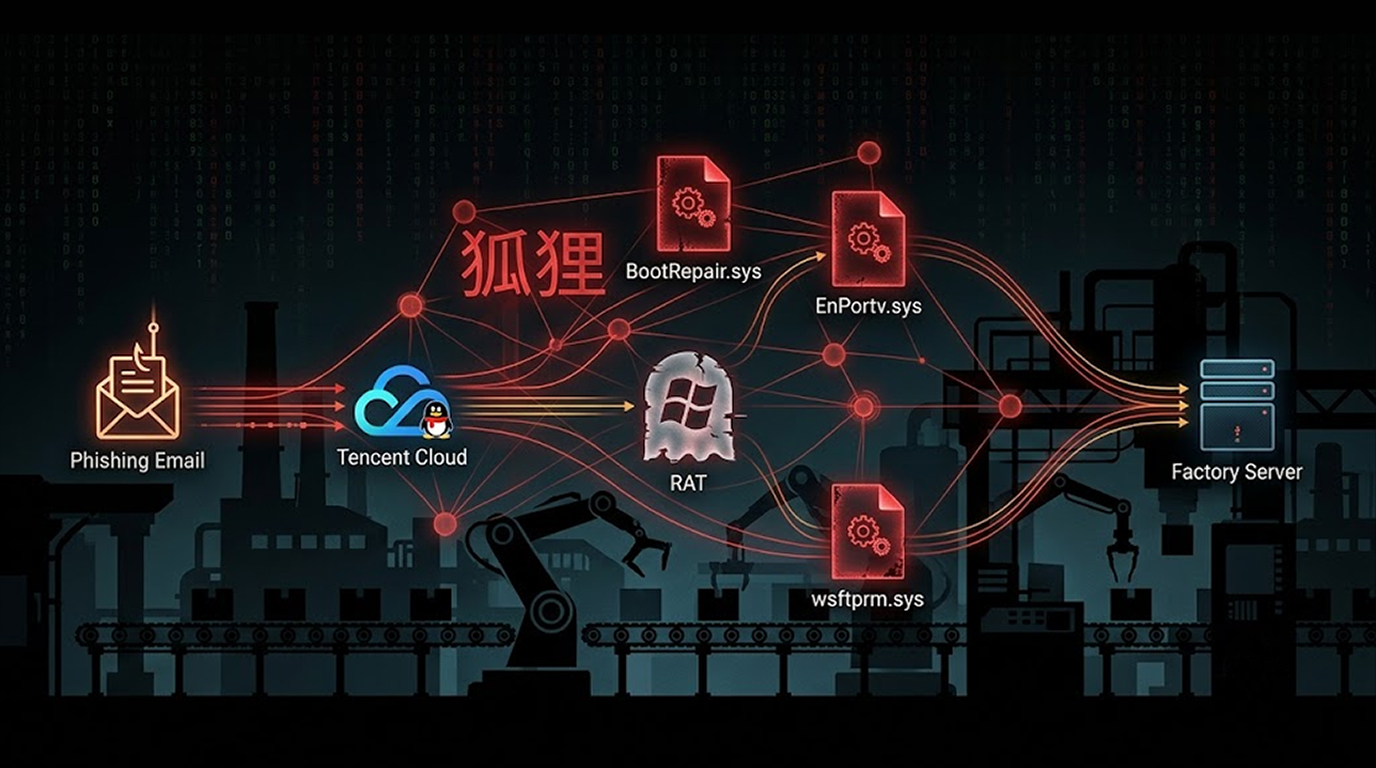
A Chinese cybercrime group known as Silver Fox is back with new tricks. The threat actors have been observed using previously unreported drivers as part of...
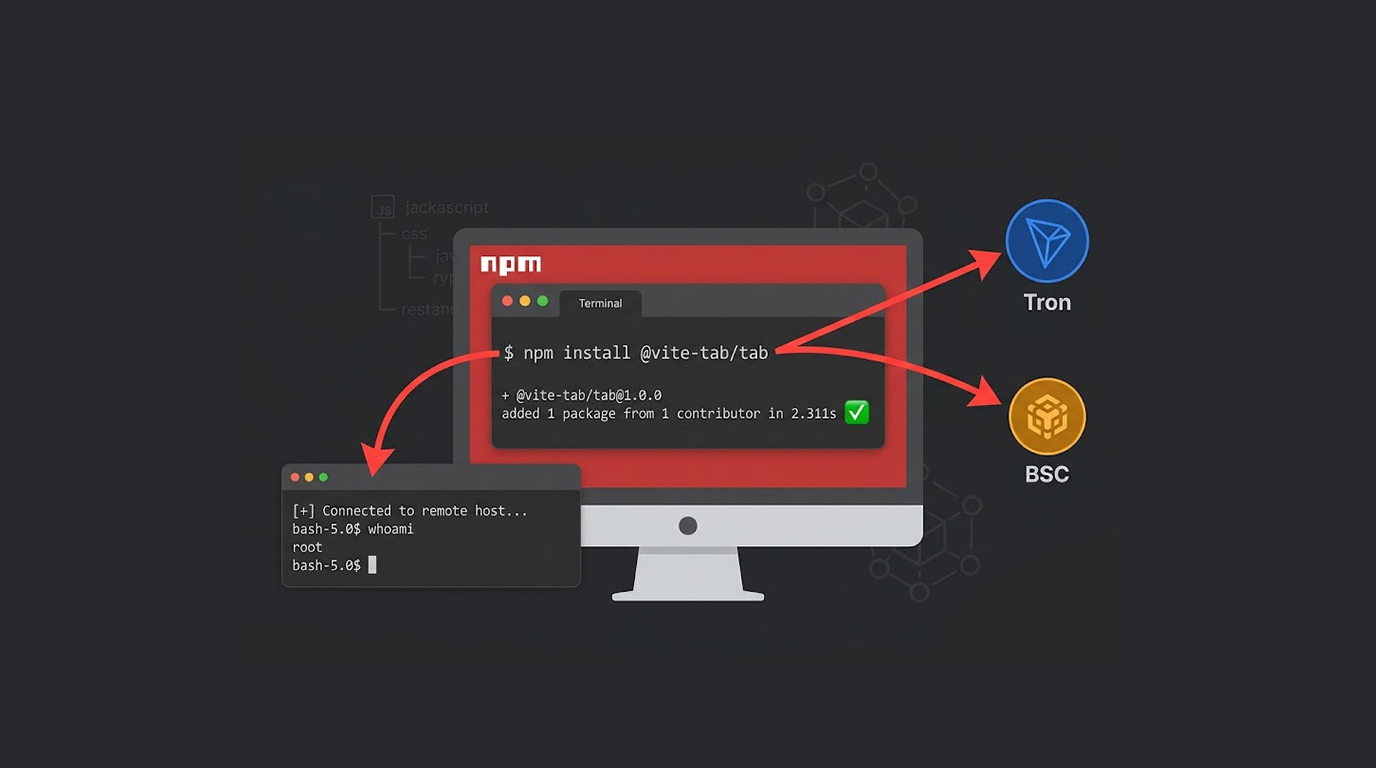
A cluster of seven malicious npm packages is targeting the Vite frontend tooling ecosystem. The campaign, codenamed ViteVenom, marks an expansion of ChainV...
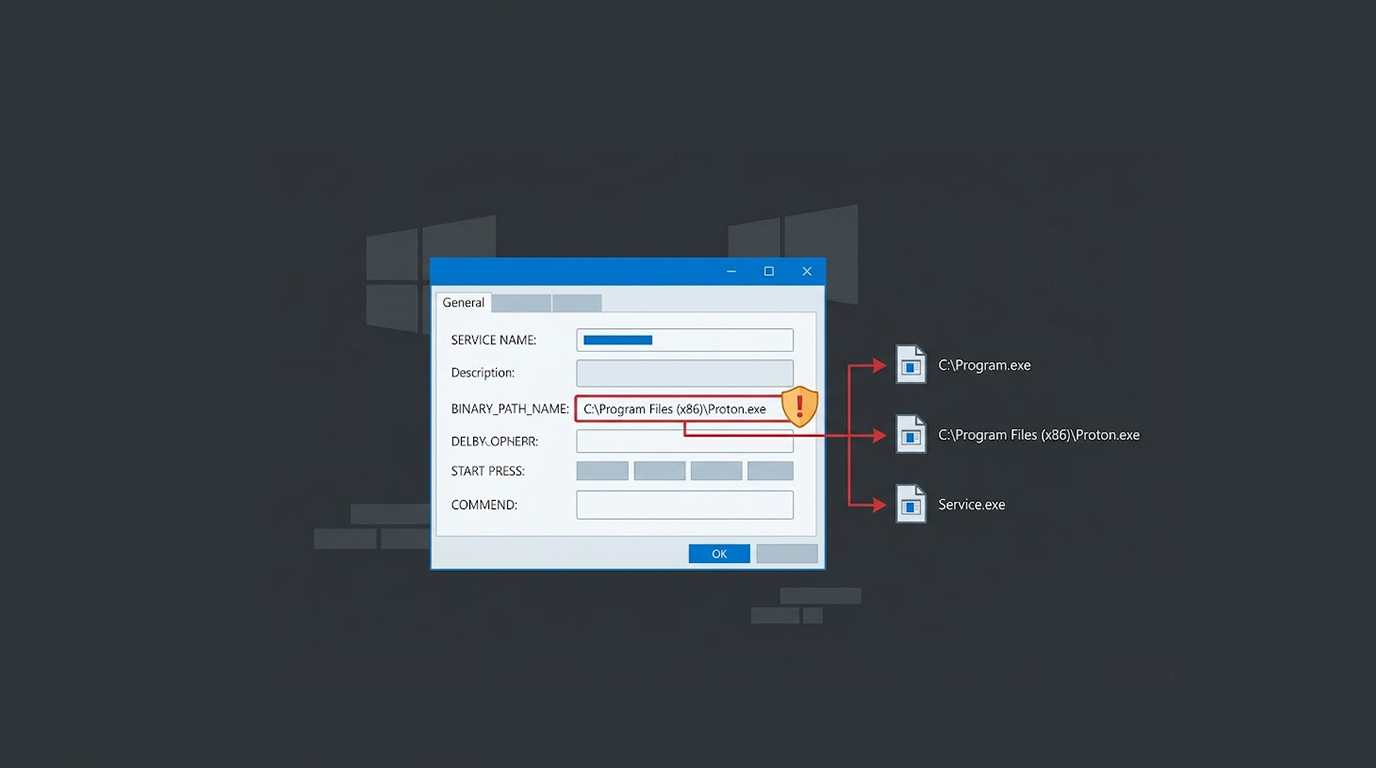
A security vulnerability in ProtonVPN version 4.4.1 could allow a local user to escalate their privileges to the highest level available on the system. The...
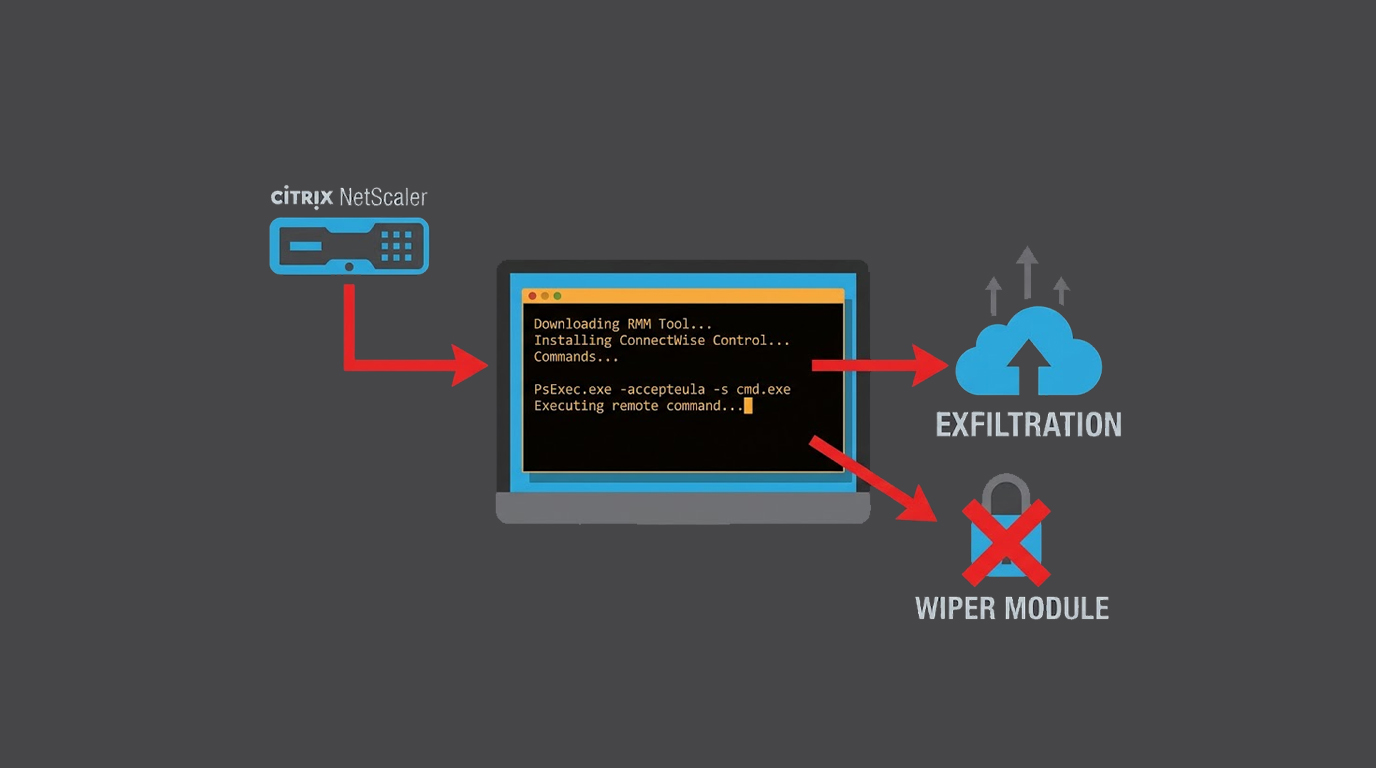
The Anubis Ransomware Campaigns are known to exploit the Citrix Bleed 2 Vulnerability as an initial access vector. The Citrix Bleed 2 Vulnerability i...
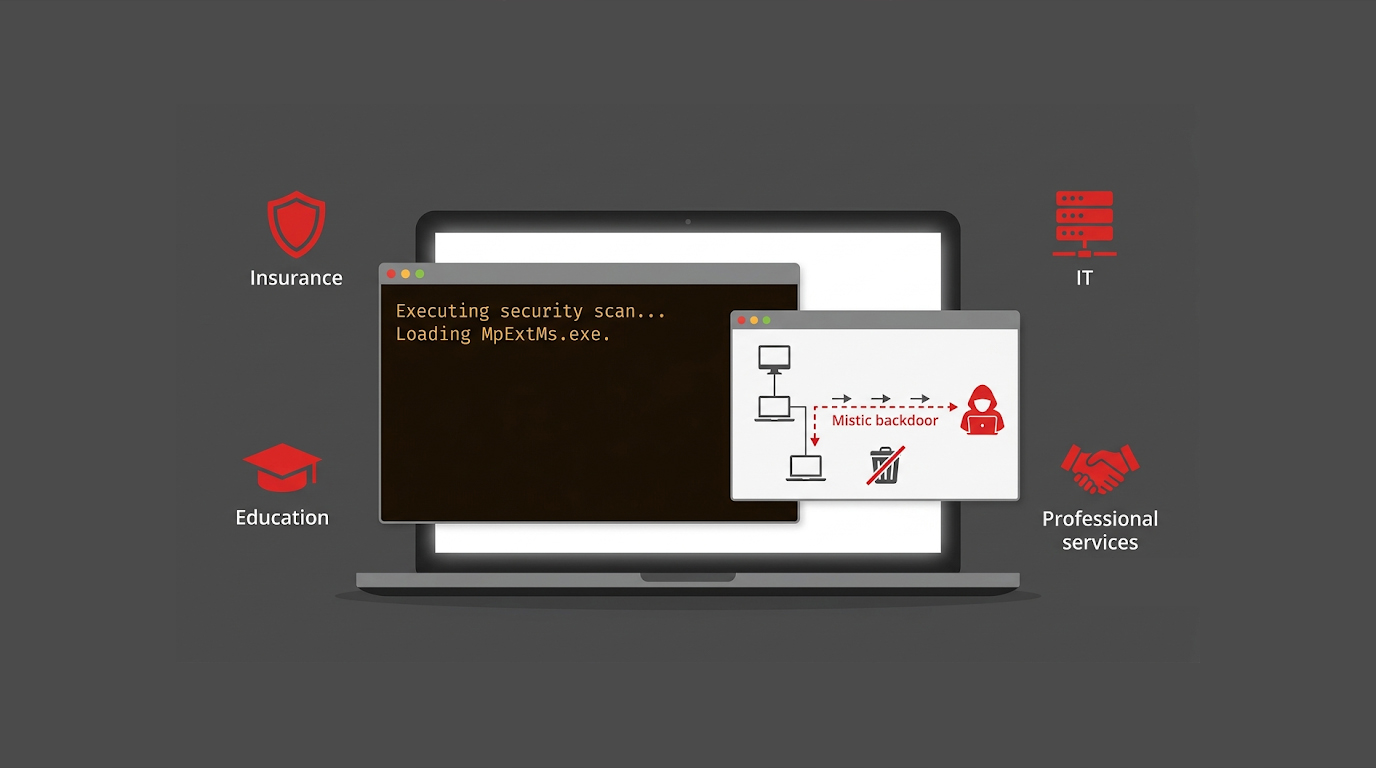
The latest stealth backdoor which has been used to conduct an attack with financial gains as the main objective since April 2026 in various industries has...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067