GitLab AI Gateway Flaw: CVE-2026-90970 Patch Guide
Your self-hosted GitLab AI Gateway might be carrying a flaw that hands command execution to any logged-in user with Duo Agent Platform access, because GitL...
Found 31 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Your self-hosted GitLab AI Gateway might be carrying a flaw that hands command execution to any logged-in user with Duo Agent Platform access, because GitL...
CISA added three Linux kernel vulnerabilities to its Known Exploited Vulnerabilities catalog on Friday. All three are being exploited in the wild. Red Hat...
The U.S. government just issued a warning that should make anyone in critical infrastructure sit up and take notice. An active threat is targeting industri...
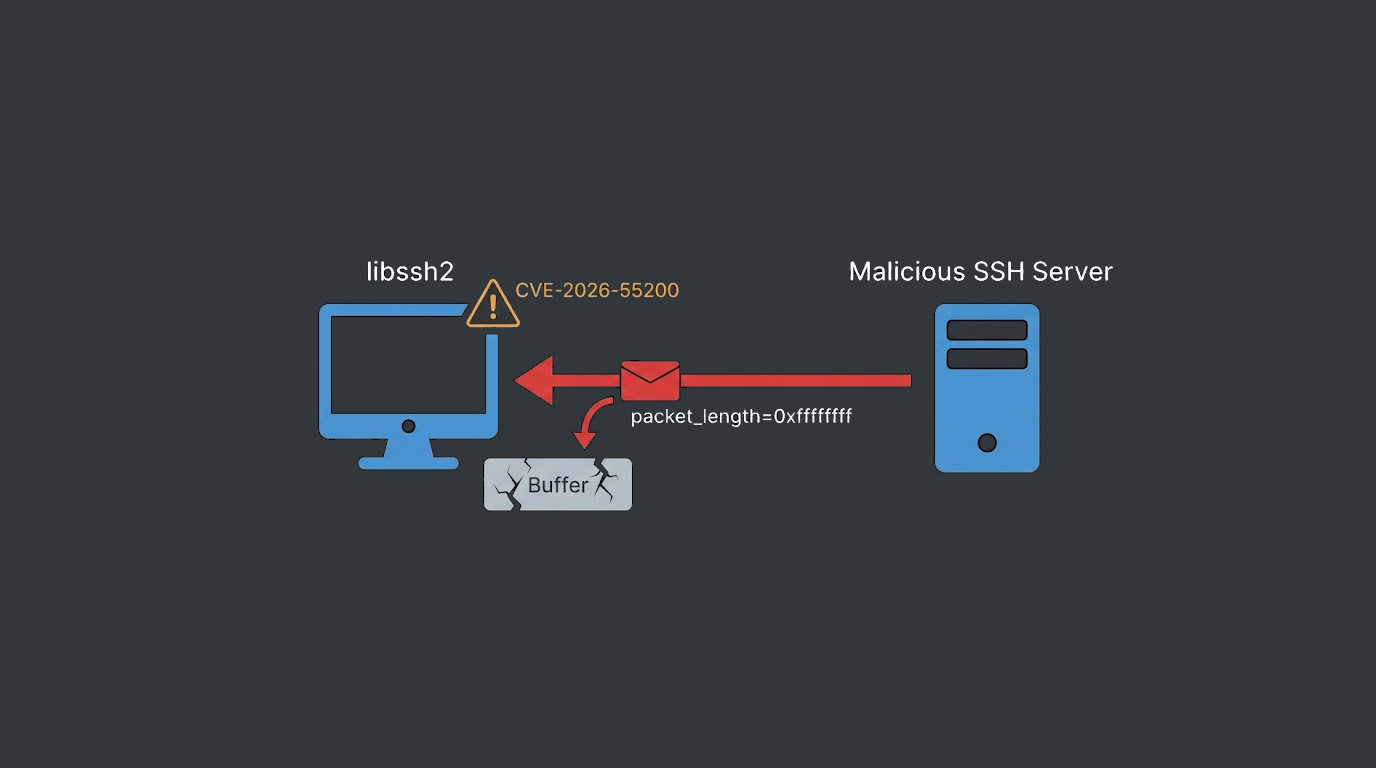
Proof of concept released to the public for CVE-2026-55200 – an extremely critical vulnerability in libssh2 where a malicious SSH server can cause me...
Is your business truly safe from a cyberattack? Many managers and entrepreneurs are somewhat ignorant toward digital resources, so many of them feel that...
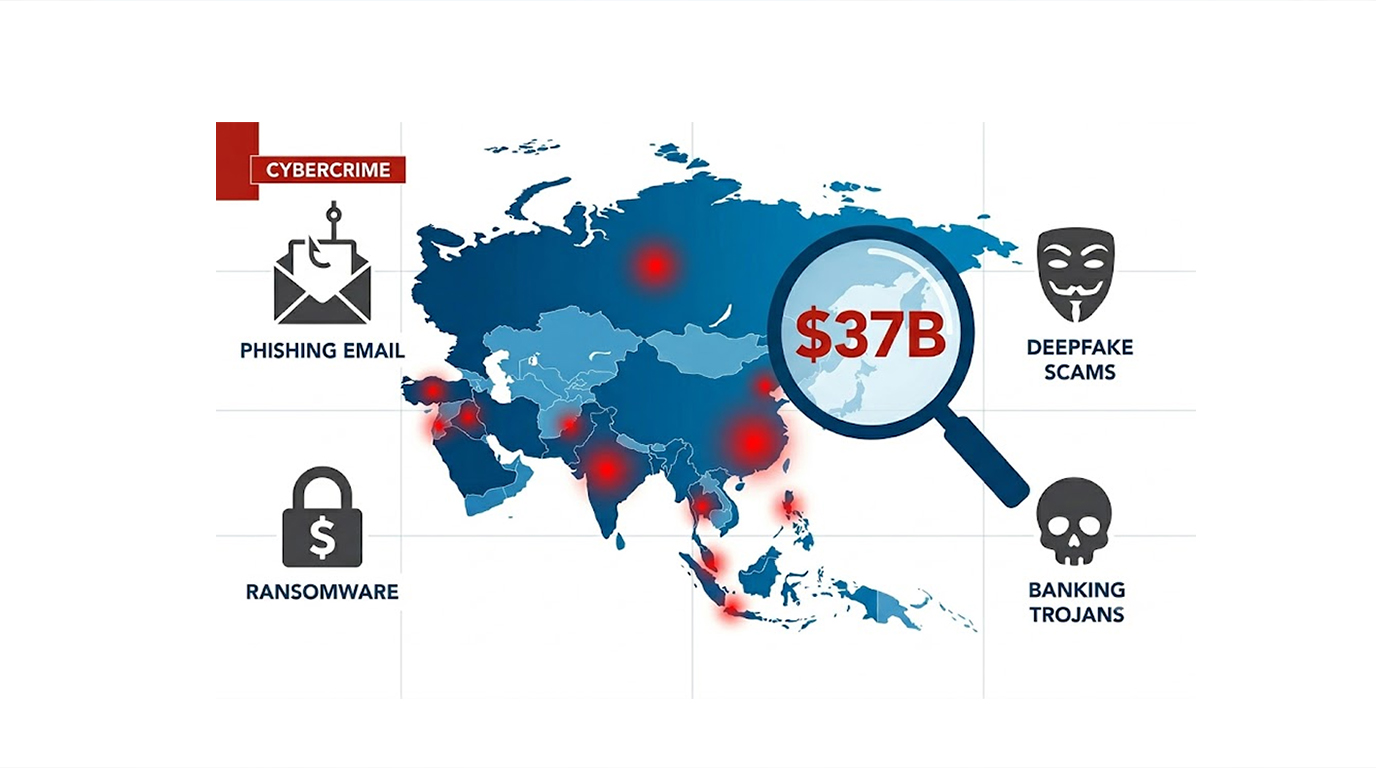
The report from INTERPOL indicates that there has been a dramatic increase in Internet crimes in Asia and the South Pacific. This rise in cybercrime has be...
A newly discovered denial-of-service exploit affects major web servers including NGINX, Apache HTTPD, Microsoft IIS, Envoy, and Cloudflare Pingora, and the...
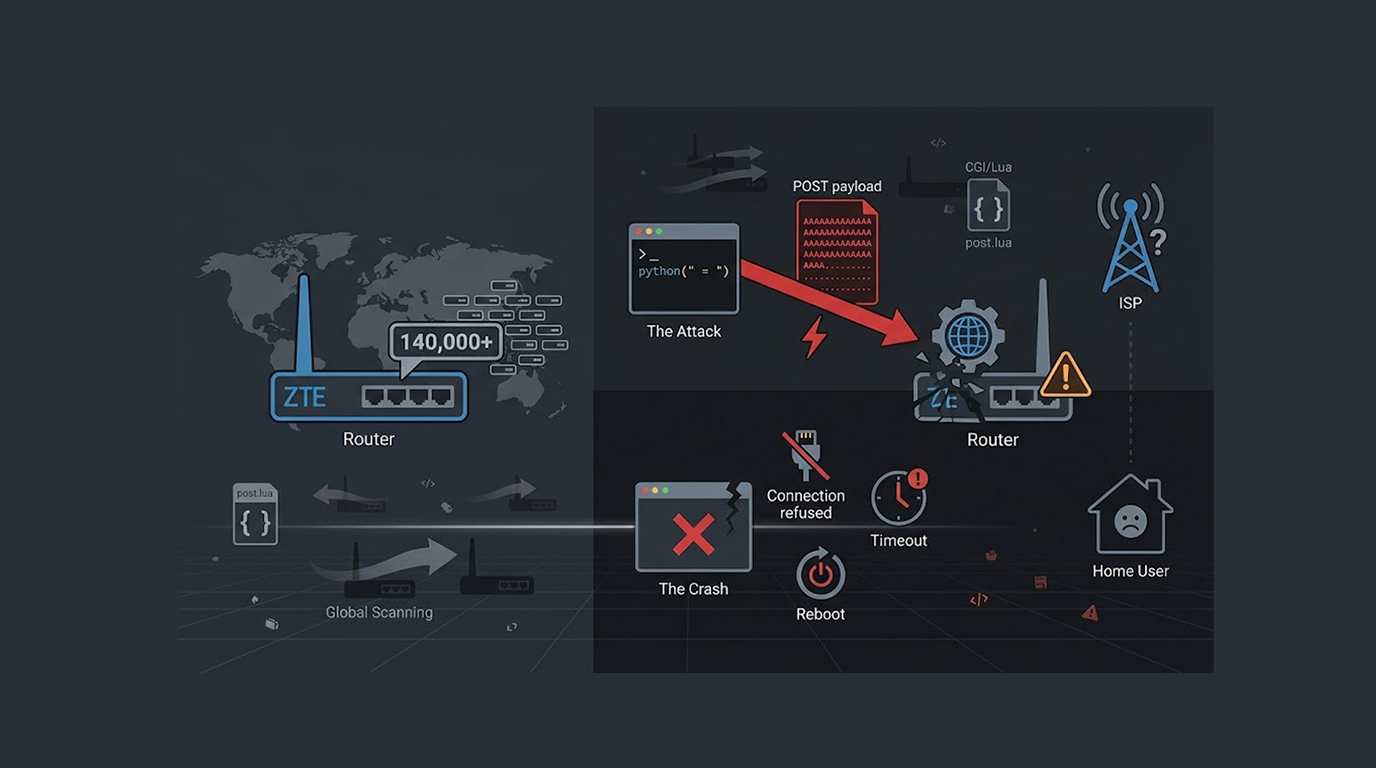
A flaw in ZTE router devices creates a vulnerability that permits unauthenticated users an ability to crash their management interface with a single, large...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067