HTTP Header Injection: When Metadata Becomes Executable
Most security reviews look at the body of a request, the parameters, the JSON, the form fields, the file uploads, because that is where the interesting log...
Found 7 relevant articles matching your search. Browse our cybersecurity insights and expert analysis below.
Most security reviews look at the body of a request, the parameters, the JSON, the form fields, the file uploads, because that is where the interesting log...
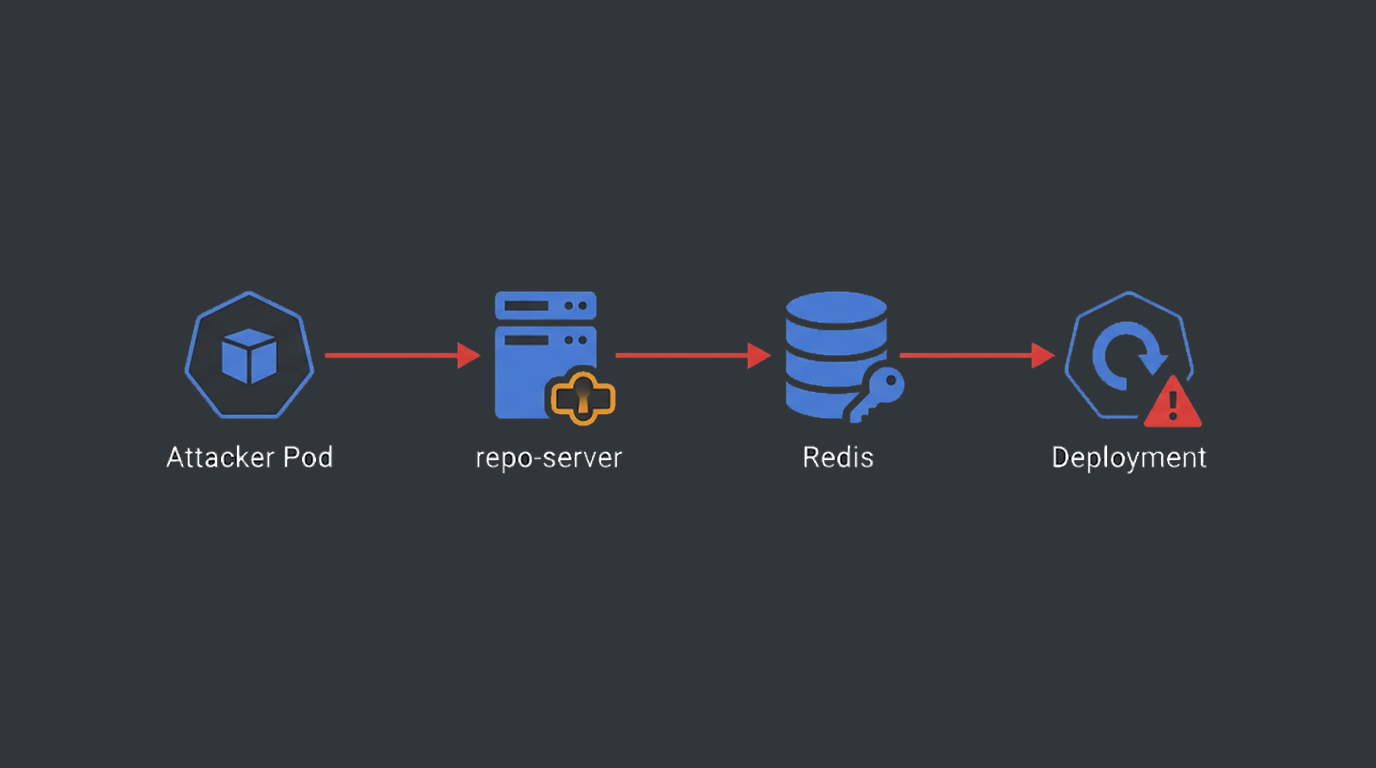
Argo CD is the backbone of GitOps for countless Kubernetes deployments. It reads Git repositories, builds manifests, and keeps clusters in sync. It also ha...
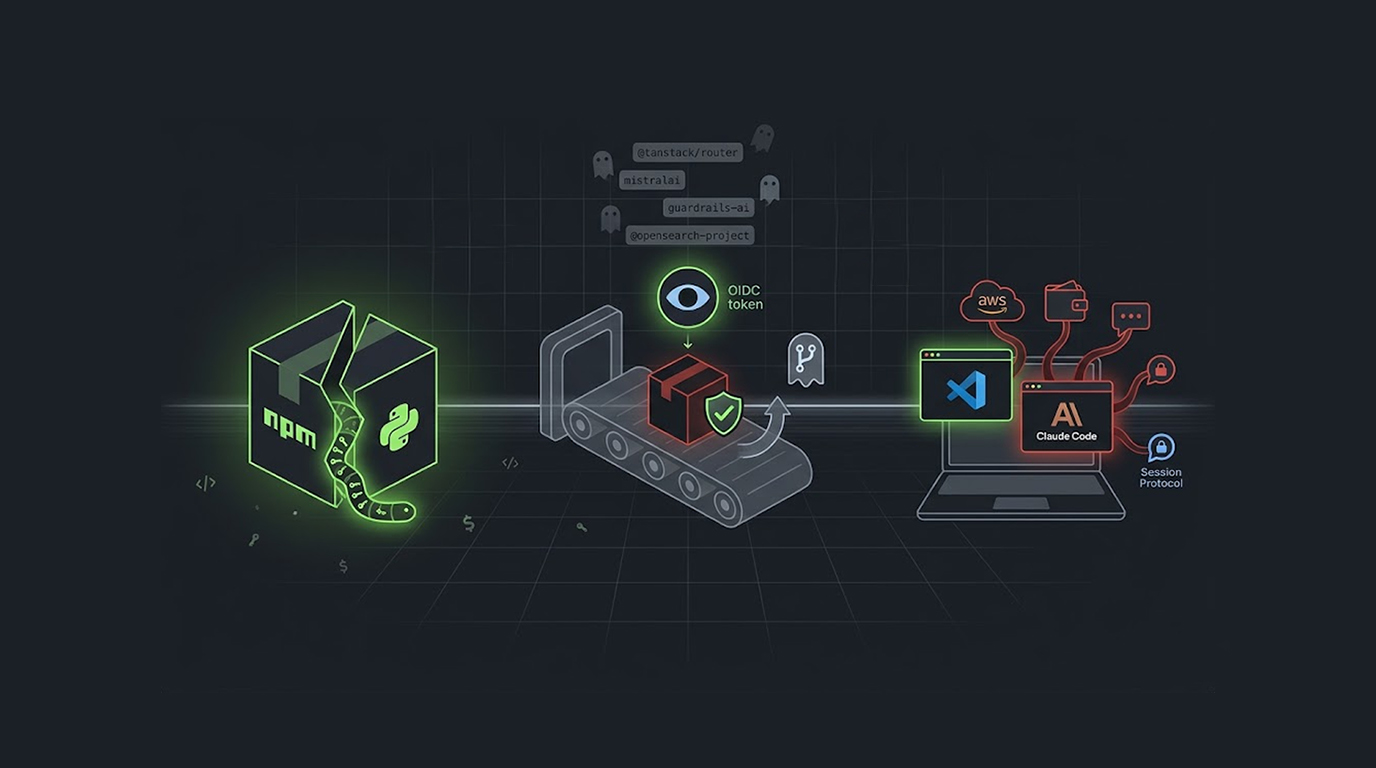
A single worm has spread across both npm and PyPI, it compromised packages from major companies like TanStack, UiPath, Mistral AI, and OpenSearch, and it u...
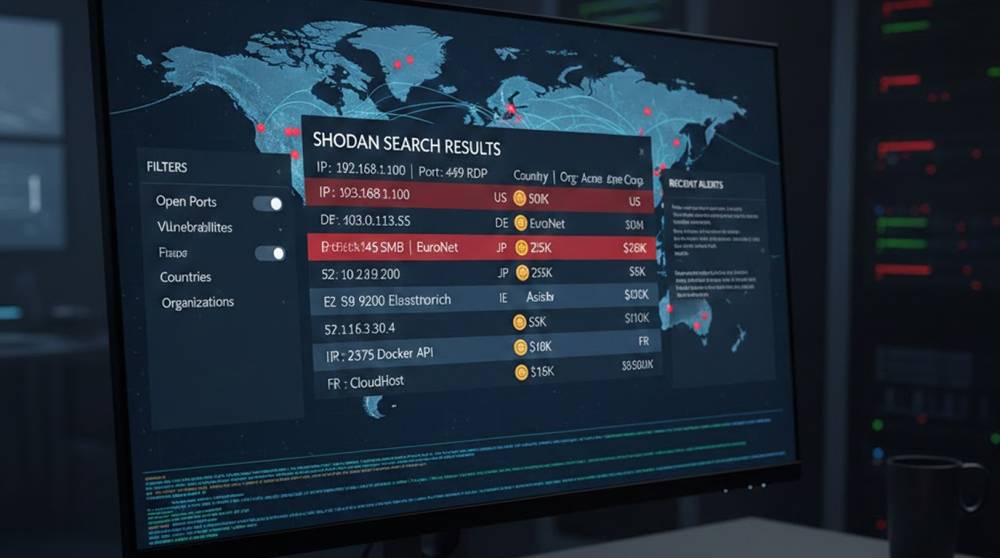
Bug bounty programs in 2026 still pay the highest rewards for vulnerabilities that give an attacker unauthenticated remote code execution (RCE), full serve...
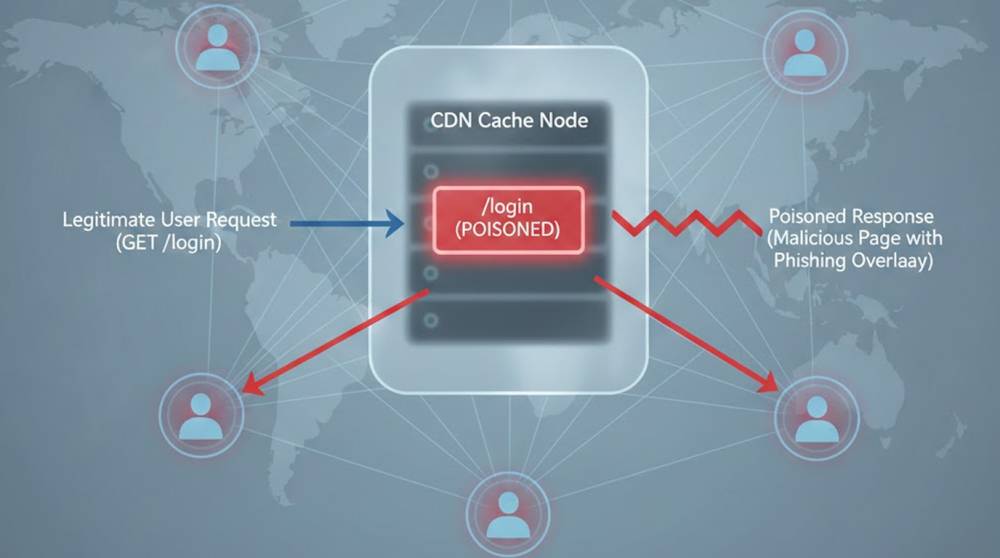
Web cache poisoning never really went away, but in 2026 it has become far more dangerous and far easier to execute than most security teams realize. The c...
On February 17, 2026, at 3:26 AM PT, an unauthorized actor used a compromised npm publish token to release version 2.3.0 of the popular AI-powered coding a...
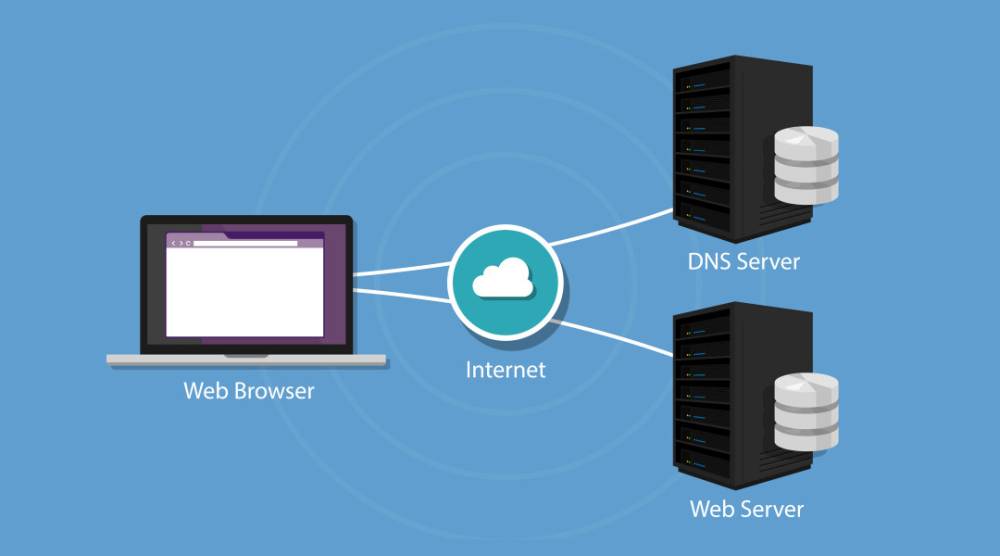
DNS attacks exploit vulnerabilities in the Domain Name System (DNS), the internet's "address book" that translates domain names into IP addresses. Hackers...
Our blog insights are backed by hands-on service delivery. Whether you need a penetration test, vulnerability assessment, emergency website recovery, or secure web development — our UK cybersecurity specialists are ready to help.
Emergency malware removal, backdoor elimination, blacklist delisting, and full post-incident hardening for compromised websites.
Authorised simulated attacks exposing real vulnerabilities in your web applications, networks, and infrastructure before attackers do.
Systematic identification and prioritisation of security weaknesses across your digital estate — with actionable remediation guidance.
OWASP-aligned web application development with security engineered in from architecture through to penetration-tested deployment.
Simulated, targeted adversarial attacks that test your people, processes, and technology under real-world conditions.
© 2016 – 2026 Red Secure Tech Ltd. Registered in England and Wales — Company No: 15581067